Coruna and DarkSword Exploit Kits Compromise Vulnerable iPhones Through Website Visits
Active Exploitation · 7 sources · Updated 10d ago · First seen Mar 19, 2026
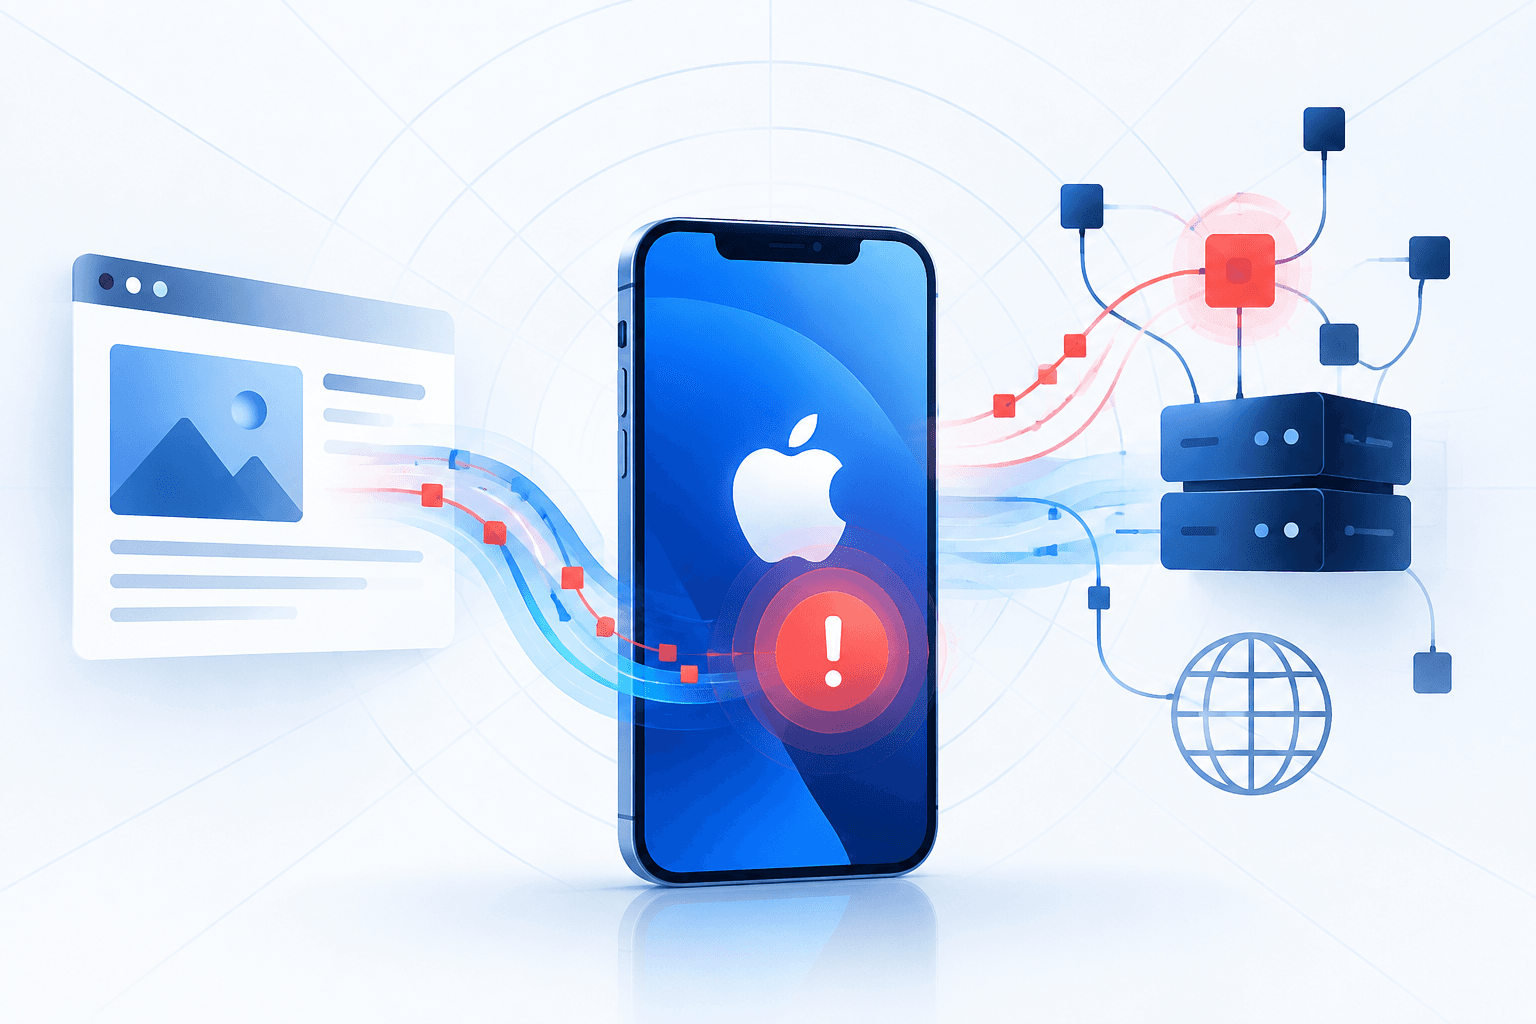
Coruna and DarkSword can turn a visit to a malicious or compromised website into full compromise of a vulnerable iPhone, without app installation or additional prompts. Coruna contains 23 exploits targeting iOS 13.0–17.2.1, while DarkSword chains six vulnerabilities against iOS 18.4–18.7, progressing through browser exploitation, sandbox escape, and kernel access. Attackers have combined the kits to expand device coverage, and reporting describes their spread from surveillance and state-linked operations into financially motivated campaigns, including targeting Ukrainian users. DarkSword’s publicly leaked source code has accelerated reuse and variant development. An iVerify investigation identified a modified version, P7 DarkSword, capable of collecting keychain and cryptocurrency wallet data and communicating bidirectionally with attacker infrastructure.
The kits put enterprise credentials, messages, location history, and other sensitive information at risk. DarkSword implements its exploitation logic in JavaScript and calls existing native functions rather than introducing native shellcode, avoiding defenses focused on newly introduced executable code. Enterprises should prioritize current iOS updates and fleet-wide version visibility, restrict mobile access to essential privileges, and monitor identity activity and device behavior for compromise. Lockdown Mode can block DarkSword’s initial exploitation stage when enabled before exposure, although it introduces usability and management restrictions. Suspected devices should be isolated and preserved for forensic investigation, with potentially exposed credentials rotated from a trusted device.