AI Agent Abuses Exposed LLMs for Credential Theft and XMRig Deployment
Emerging Technology Risk · 2 sources · Updated 4d ago · First seen Oct 29, 2026
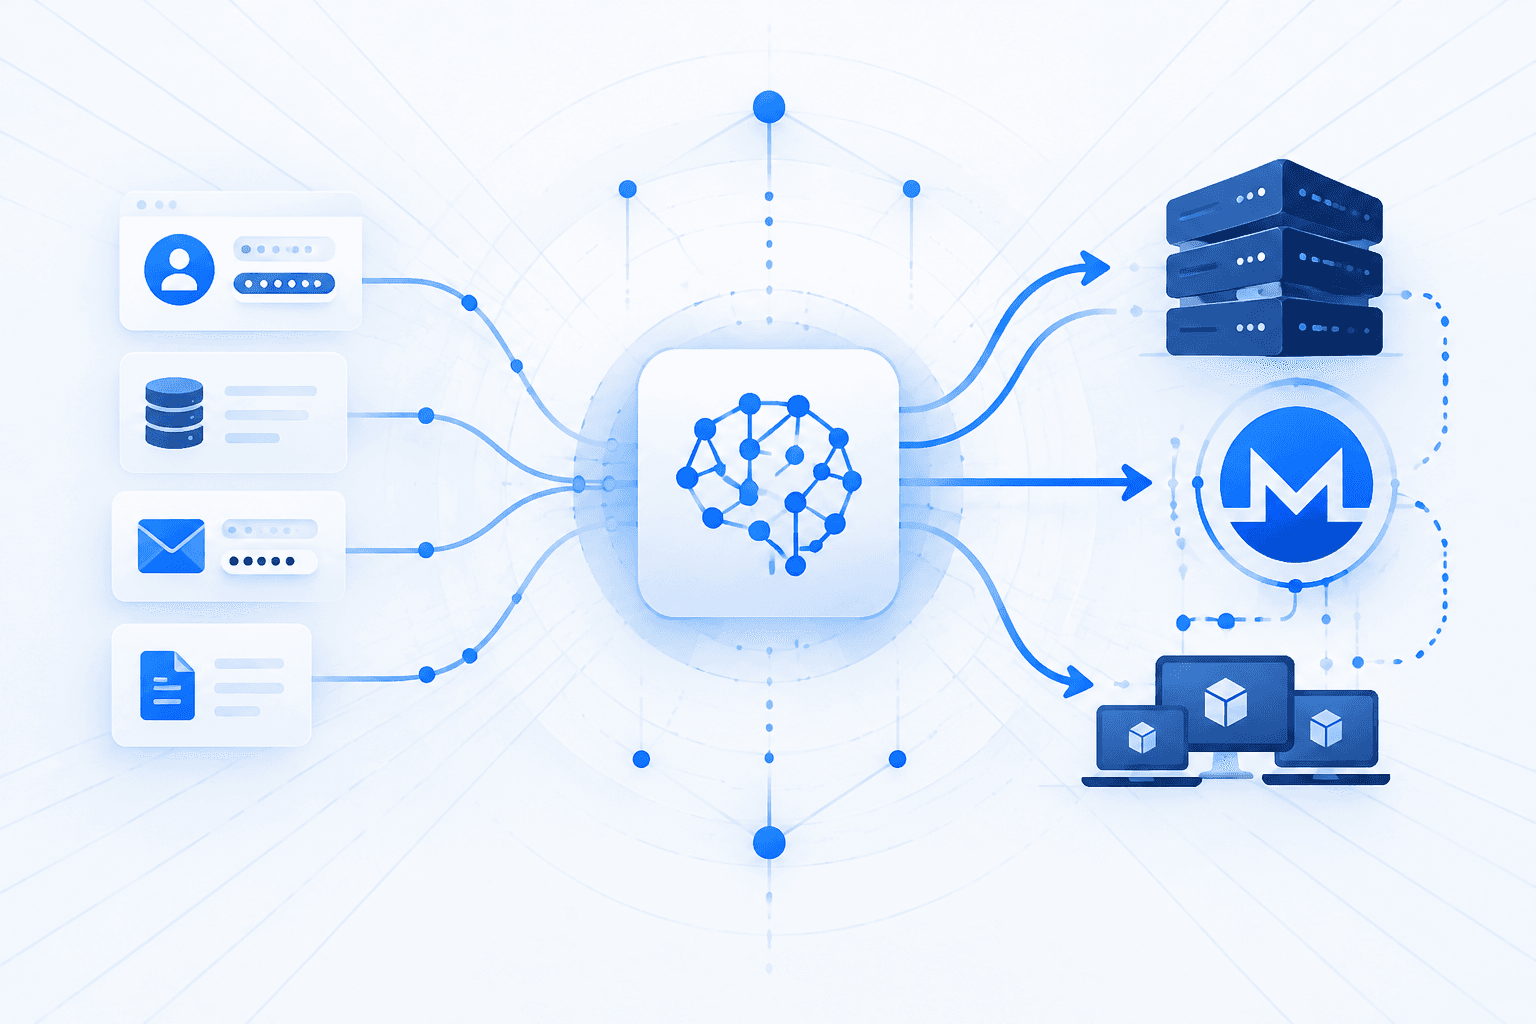
Symantec identified an AI agent using a mode called “Skynet” to discover unprotected AI models online and enlist them in autonomous attacks. Researchers captured the agent’s instructions through a honeypot impersonating an exposed AI service. The instructions directed models to find vulnerabilities, steal credentials and install the XMRig miner to generate Monero, with support for up to 100,000 actions without human supervision. The captured instructions demonstrate the intended workflow, but the supplied reporting does not establish the scale of successful compromises.
The operation combines LLMjacking—unauthorized use of another organization’s AI resources—with attempts to compromise additional servers for credential theft and cryptocurrency mining. Exposed-model owners bear the inference and computing costs, while agents with internet access, shell capabilities and excessive permissions can chain discovery and exploitation tasks. Organizations should require authentication for LLM endpoints, remove unnecessary public exposure and enforce least-privilege access to agent tools, credentials and downstream systems.