Help Desk Impersonation Leads to AD CS Abuse Through ESC1 and ESC8
Attack Tradecraft · 13 sources · Updated 13d ago · First seen Oct 30, 2026
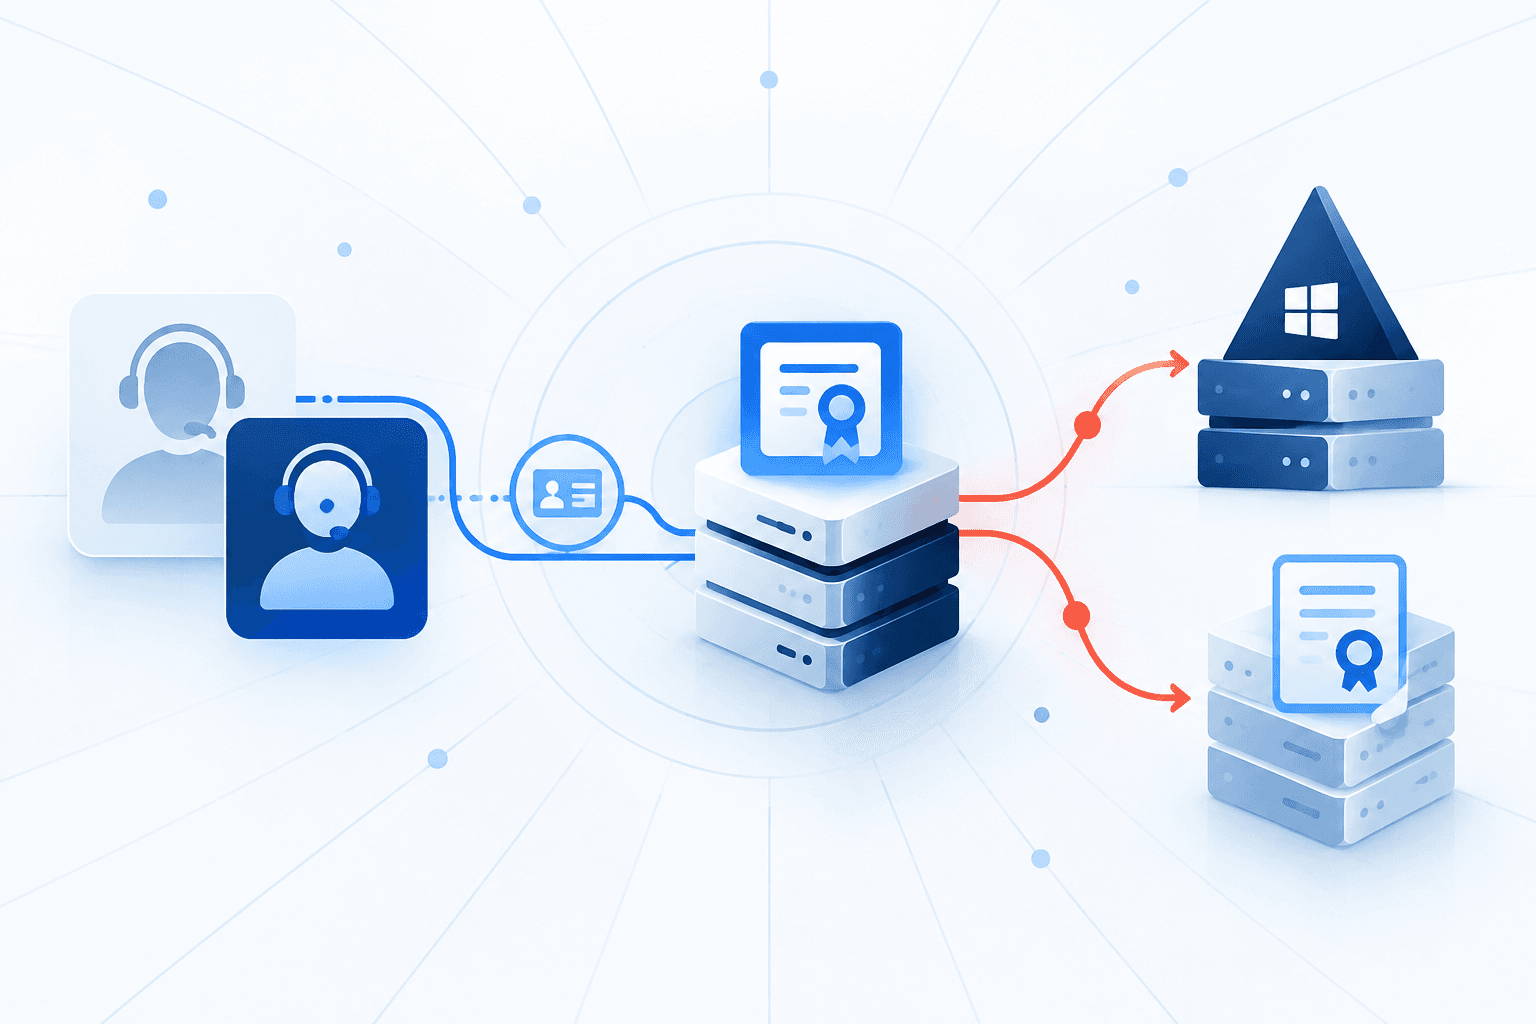
Microsoft Threat Intelligence investigated two unattributed intrusions in which attackers impersonated IT help desk staff through Microsoft Teams and persuaded users to approve remote access, primarily through Quick Assist. The attackers staged portable runtimes, performed discovery, and exploited insecure Active Directory Certificate Services (AD CS) configurations—not a vulnerability in Teams. In the first intrusion, ESC1 certificate-template abuse compromised privileged identities and enabled DCSync. Automated containment blocked substantial follow-on activity, but a privileged account excluded from containment remained usable and supported data exfiltration.
In the second intrusion, attackers used PetitPotam and ESC8 NTLM relay to obtain a domain-controller certificate and a Kerberos ticket-granting ticket; customer-led workstation isolation stopped further observed progression. The incidents highlight the need to tighten remote-support verification, harden certificate templates and enrollment endpoints, and ensure containment covers all compromised privileged accounts. Recovery must address certificate and Kerberos persistence separately: password resets do not revoke issued certificates, and certificate revocation does not invalidate previously issued Kerberos tickets.