Attacker Uses 1,438 Fake FOFA Accounts to Harvest Exposed OpenAI and DeepSeek API Keys
Breach & Incident Intelligence · 2 sources · Updated 7d ago · First seen Nov 10, 2026
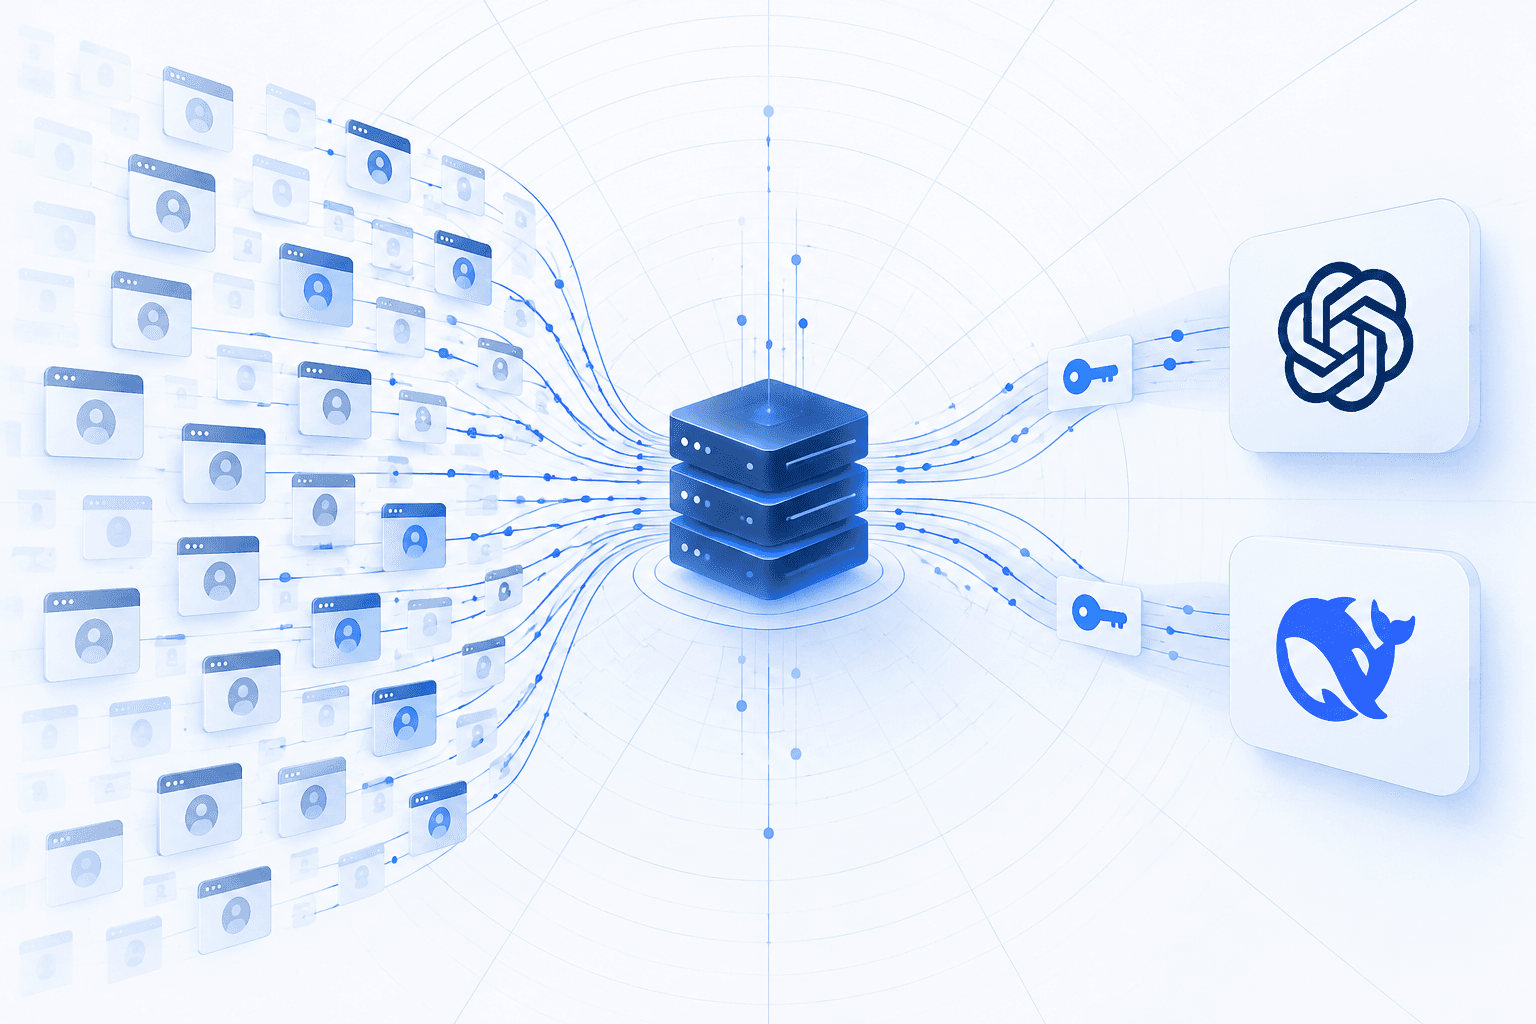
An unidentified threat actor automated the creation of at least 1,438 fake FOFA accounts to locate and harvest exposed OpenAI and DeepSeek API keys from misconfigured internet-facing servers, according to VECERT. The operation extracts credentials, checks their validity and remaining credit, and uses working keys to power the actor’s AI coding assistant and other scripts. Affected organizations face unauthorized AI consumption, depleted credits, and unexpected charges.
VECERT tracked the activity as VECERT-TI-2026-1107-B and linked it to Operation Ghost-Campus, tentatively assessing that the actor may be based in China. The same attacker server reportedly hosted tools that collected sensitive information about 5,132 students at Shanghai Publishing and Printing College and automated fraudulent reading activity to earn school points. Organizations should revoke exposed keys, review usage logs, prevent secrets from being publicly accessible, and set AI spending limits. Reported infrastructure indicators contain an unresolved discrepancy between two purported mail-server IP addresses and should be validated before operational use.