Mallory
← Back to News
credential-stealer-activityinitial-access-methodloader-delivery-mechanismcredential-access-method

Fake macOS Script Editor Error Tricks Users Into Installing Odyssey Stealer

Malware Intelligence · 6 sources · Updated 1h ago · First seen Nov 17, 2026
Fake macOS Script Editor Error Tricks Users Into Installing Odyssey Stealer

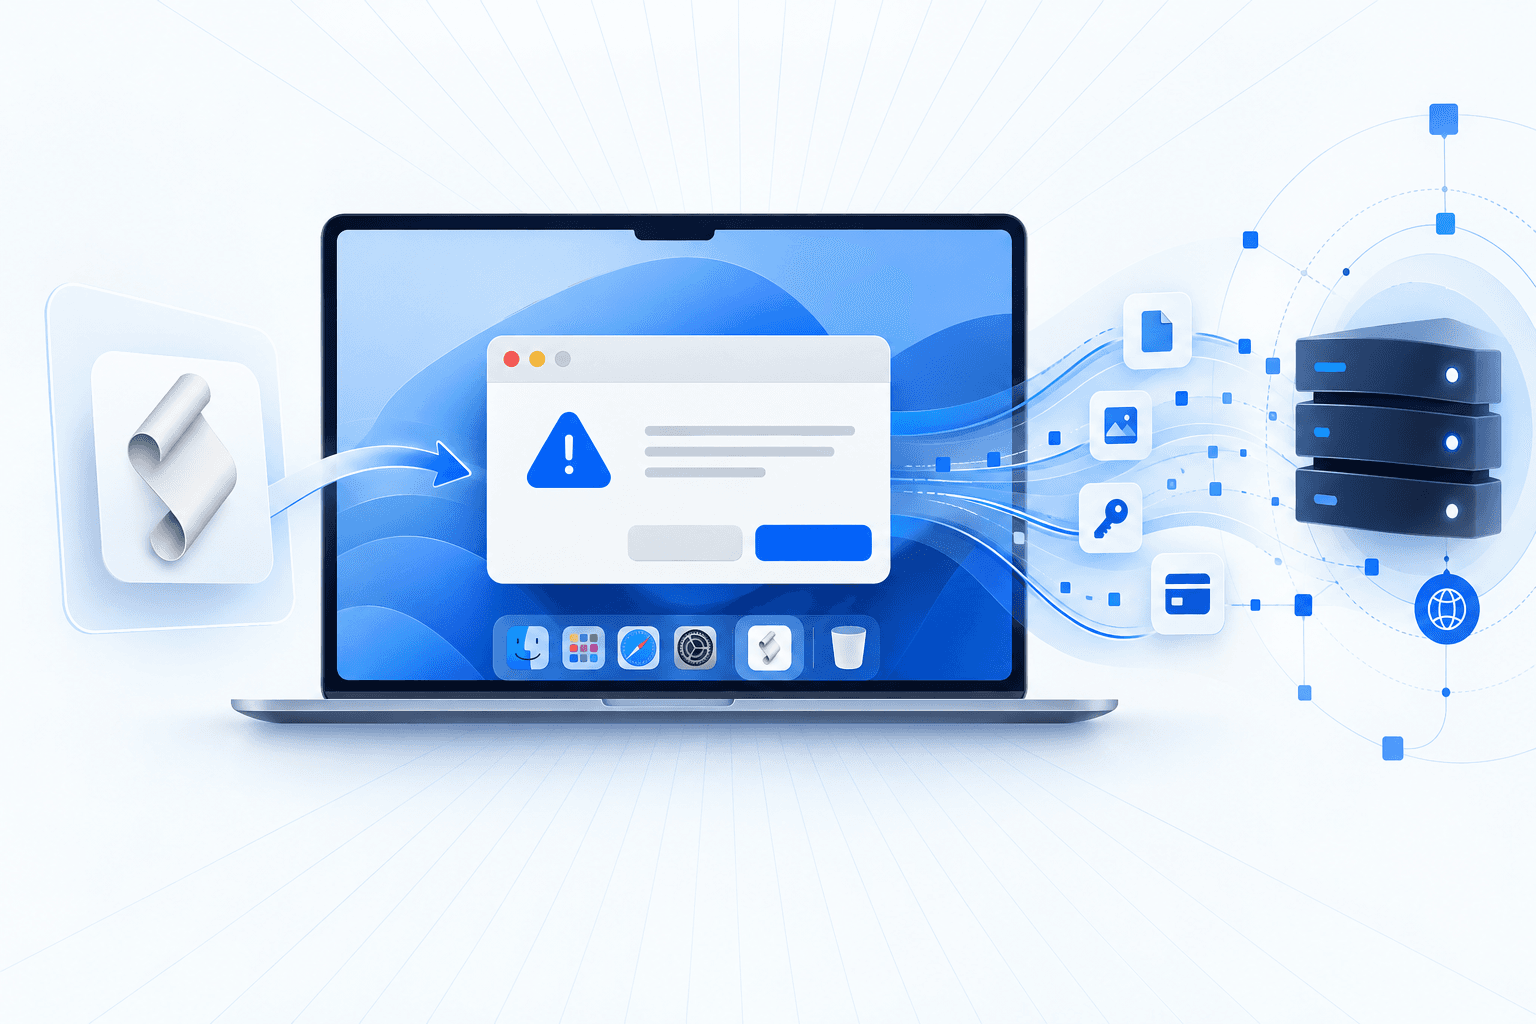
A malicious compiled AppleScript named Installer GoogleCert.scpt uses a fake “Error 0x0013” message to persuade macOS users to press Run in Script Editor, downloading and executing Odyssey Stealer, according to Rogue Authority. The payload targets Intel and Apple Silicon Macs, stealing passwords, keychain data, browser information, cryptocurrency wallets, and sensitive files before uploading them to attacker infrastructure. It also replaces installed Ledger and Trezor applications with fraudulent versions that request wallet recovery phrases and, for hidden Trezor wallets, an additional passphrase. A downloaded, obfuscated Go bot contained components suggesting remote-access tunneling, but researchers did not confirm its full capabilities or find a mechanism to restart either payload after reboot.

The technique extends Odyssey’s use of user-assisted execution rather than software exploits. CloudSEK previously documented fake Microsoft Teams and TradingView download lures that induced users to run encoded AppleScript, while Red Canary identified a broader shift toward ClickFix delivery following Apple’s October 2024 patch of a widely abused Gatekeeper bypass. Earlier Odyssey samples used LaunchDaemon persistence, underscoring that behavior varies across deployments. Defenders should prioritize monitoring unusual Script Editor and AppleScript execution followed by payload downloads, sensitive-data collection, outbound transfers, or replacement of wallet applications. Red Canary cautions that Odyssey, Atomic, and Poseidon share substantial tradecraft, so attribution should rely on multiple indicators rather than AppleScript activity alone.
Hunt this familyPull IOCs and campaign context straight into your stack.
Get the IOCs
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

8 events · 2024 – Aug 2025
  1. Reported Nov 17, 202622h ago

    Fake Script Editor error exposes Odyssey infection and wallet-phishing chain

    An analysis revealed that Installer GoogleCert.scpt hides executable commands beneath 222 blank or comment lines and uses a fake “Installer Error 0x0013” to persuade users to run an Intel- and Apple Silicon-compatible Odyssey payload. The payload steals sensitive data, launches an obfuscated Go bot with suspected tunneling functionality, and replaces Ledger and Trezor applications with recovery-phrase phishing wrappers; the analysis found no mechanism to restart the stealer or bot after reboot.

    A fake “Error 0x0013” in Script Editor that installs Odyssey Stealer on your Mac - rogueauthority.org
  2. Reported Oct 9, 20251y ago

    Red Canary details Odyssey evolution and distinctions from Atomic

    Red Canary documented Odyssey's addition of anti-sandboxing, launch daemon persistence, and botnet-style remote execution, noting that Atomic later adopted the same features. Its analysis identified subtle family distinctions, including Atomic's frequent use of the BuildID HTTP header versus Odyssey's lowercase buildid.

    Distinguishing Atomic, Odyssey, and Poseidon stealers on macOS
  3. Reported Sep 5, 20251y ago

    CloudSEK uncovers fake Microsoft Teams site delivering Odyssey

    CloudSEK identified teamsonsoft[.]com impersonating Microsoft Teams and persuading macOS users to execute a base64-encoded AppleScript that delivered Odyssey, linking the campaign to an infrastructure cluster containing 24 unique IP addresses. The analyzed malware stole credentials and wallet data, exfiltrated an archive to 185.93.89.62, installed LaunchDaemon persistence, and replaced Ledger Live with a trojanized application.

    Threat Actors Impersonate Microsoft Teams To Deliver Odyssey macOS Stealer Via Clickfix
  4. Aug 2025

    Forcepoint reports TradingView-themed ClickFix campaign

    Forcepoint reported a TradingView-themed ClickFix campaign that CloudSEK subsequently linked to Odyssey delivery through Microsoft Teams impersonation.

    Threat Actors Impersonate Microsoft Teams To Deliver Odyssey macOS Stealer Via Clickfix
  5. Mar 2025

    macOS stealer activity resumes with ClickFix delivery and Odyssey

    macOS stealer activity resumed in March 2025 as attackers shifted toward paste-and-run or ClickFix delivery following the Gatekeeper fix. Odyssey emerged as an evolution of Poseidon, and Red Canary initially tracked its newer instances under Poseidon's profile.

    Distinguishing Atomic, Odyssey, and Poseidon stealers on macOS
  6. Oct 2024

    Apple patches Gatekeeper bypass used to deliver macOS stealers

    Apple released a macOS update that closed a widely abused right-click-and-open Gatekeeper bypass used to distribute Atomic and Poseidon. The change disrupted their traditional delivery methods and preceded a temporary lull in observed activity.

    Distinguishing Atomic, Odyssey, and Poseidon stealers on macOS
  7. 2024

    Poseidon operator reportedly sells the stealer

    Poseidon operator Rodrigo4 reportedly sold the malware in fall 2024 and was said to retire from malicious activity. Poseidon subsequently evolved into the rebranded Odyssey Stealer.

    Distinguishing Atomic, Odyssey, and Poseidon stealers on macOS
  8. 2024

    macOS information-stealer activity surges

    Red Canary observed a surge in adversaries targeting macOS devices during 2024 to steal sensitive information from browsers, extensions, and other applications.

    Distinguishing Atomic, Odyssey, and Poseidon stealers on macOS
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

2 linked

Affected products

2 linked
MacosLedger Live

Organizations

2 linked
TrezorLedger

Observables

22 linked

Indicator values are masked on this page. View all 22 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
Hunt This Malware
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.