Mallory
← Back to News
phishing-campaign-intelligencecredential-access-methodinitial-access-methodidentity-impersonation-fraud

Microsoft 365 Device-Code Phishing Uses Fake SharePoint Lures to Gain Access Tokens

Social Engineering & Fraud · 2 sources · Updated 29m ago · First seen Nov 19, 2026
Microsoft 365 Device-Code Phishing Uses Fake SharePoint Lures to Gain Access Tokens

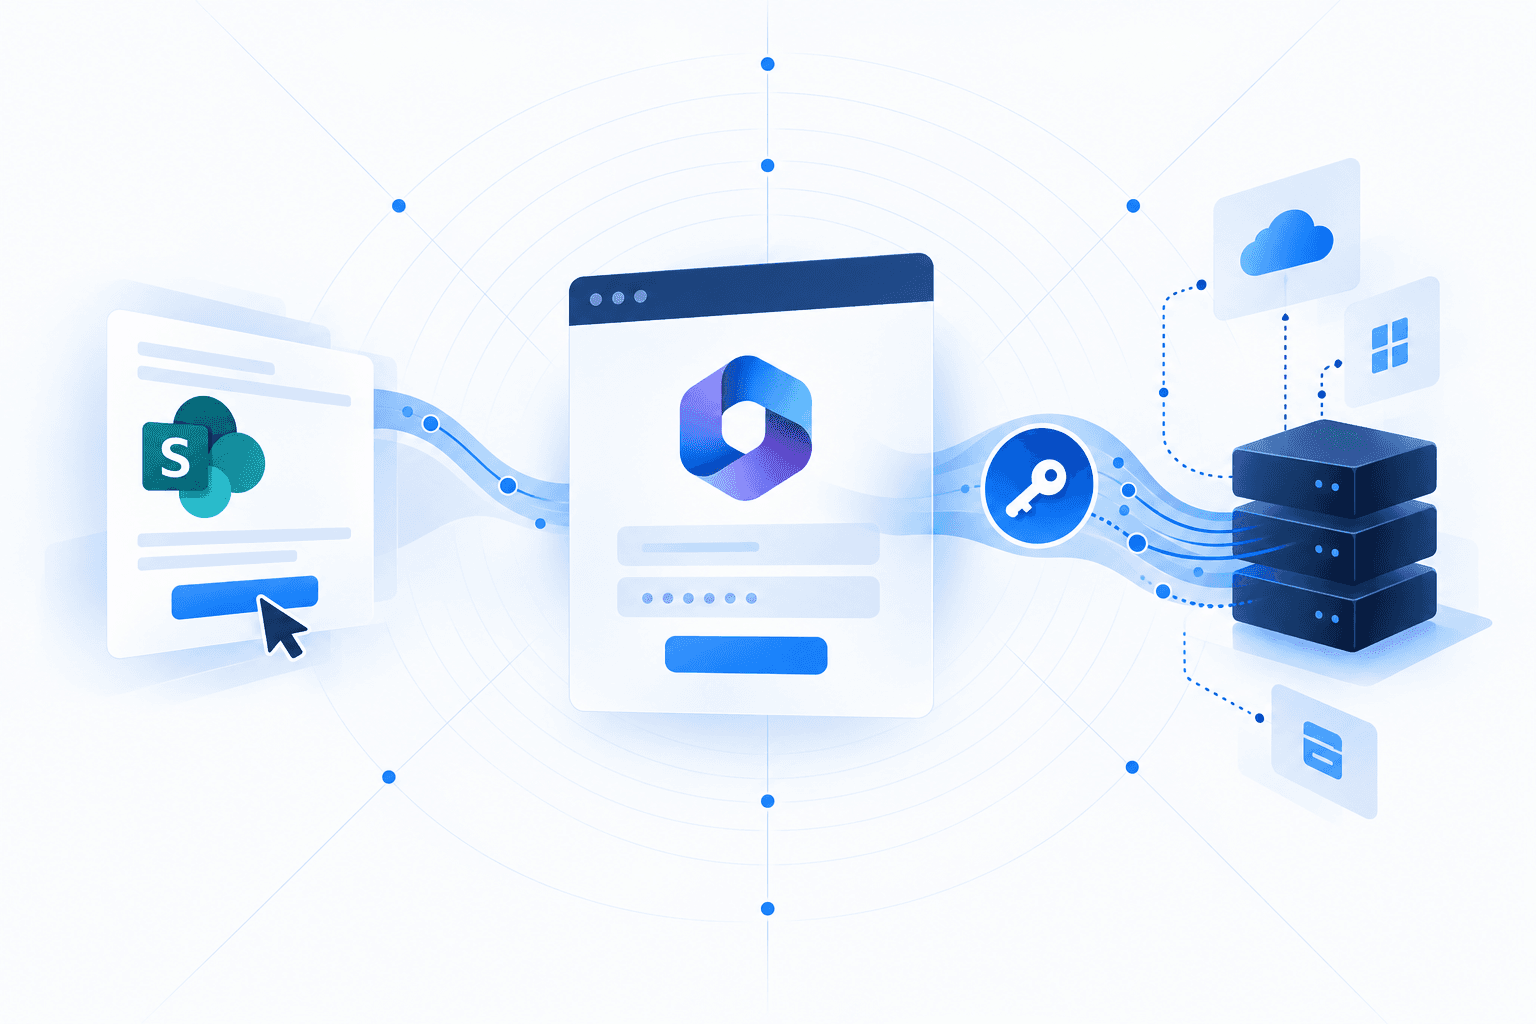
Phishing campaigns analyzed by Hornetsecurity’s Threat Intelligence Lab used payment-themed emails, malicious HTML/SVG attachments and counterfeit SharePoint workspaces to target Microsoft 365 accounts. Obfuscated attachments redirected recipients to hosted lures that supplied verification codes and document-access instructions, steering them into Microsoft’s legitimate device-authorization flow. When victims signed in and completed any required MFA, they authorized an attacker-controlled client to receive access tokens rather than simply opening a document. The technique did not require stealing passwords or technically defeating MFA; potential access to corporate email and files depended on the permissions granted.

Investigators identified multiple attachment variants, campaign domains, and backend status and heartbeat mechanisms coordinating the lures, but did not identify the operators or disclose confirmed compromise counts. Defenders should inspect attachment contents and redirects, correlate campaign-related traffic with Microsoft Entra device-code sign-ins, and restrict unnecessary device-code authentication through Conditional Access. Suspicious authorizations warrant prompt investigation and revocation of affected sessions.
Is your org in this campaign?Get the infrastructure and lures behind it.
Hunt this campaign
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

5 events · Nov 2026
  1. Reported Nov 19, 20267h ago

    Funds-transfer email delivers an HTML/SVG payment-remittance redirector

    An electronic-funds-transfer email delivered ElectronicFundsTransferRemittanceAdvice.html alongside a ZIP attachment. The HTML used a full-canvas SVG click target and layered decoding to redirect recipients to 5txpm30dqe.krointechbillpaycheckingusalexingto[.]sbs.

    Device Code Phishing in Microsoft 365: Attack Analysis
  2. Reported Nov 19, 20267h ago

    Payment-advice ZIP redirects recipients through a Workers-hosted endpoint

    Another payment-advice ZIP contained an SVG page displaying a 'One tap to proceed' prompt. Clicking it redirected the browser through base-hub-yw7q.p-xxorevv8.workers[.]dev.

    Device Code Phishing in Microsoft 365: Attack Analysis
  3. Reported Nov 19, 20267h ago

    Joint-check lure uses an encoded SVG redirect to shared campaign infrastructure

    Researchers identified a joint-check and updated-statement variant presenting an HTML attachment as securely shared payment advice. Its SVG verification prompt decoded a redirect to tgg5rqrdcb.synerghylnksloads[.]cfd, sharing a parent domain with the first campaign.

    Device Code Phishing in Microsoft 365: Attack Analysis
  4. Nov 2026

    Electronic-payment campaign delivers an obfuscated SharePoint document lure

    A second November 2026 campaign distributed SpwcinBillPaymentReports.zip using scheduled electronic-payment notices. Its HTML loader reconstructed a counterfeit SharePoint page from 475 obfuscated fragments; the page obtained device-authorization codes from its backend and used heartbeat and session-status requests to track progress.

    Device Code Phishing in Microsoft 365: Attack Analysis
  5. Nov 2026

    Payment-advice campaign lures Microsoft 365 users into device-code authorization

    A November 2026 campaign used single-period email subjects and personalized ZIP attachments containing interactive SVG redirectors to reach counterfeit SharePoint workspaces. The workspaces presented attacker-supplied device codes for entry on Microsoft's genuine authorization page, where successful authentication, including required MFA, would authorize tokens for the attacker's client.

    Device Code Phishing in Microsoft 365: Attack Analysis
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Affected products

1 linked
Microsoft 365

Observables

12 linked

Indicator values are masked on this page. View all 12 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
Hunt This Campaign
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.