COLDRIVER APT Deploys New Malware in ClickFix Espionage Campaign
2 sources · Updated 5mo ago · First seen Sep 29, 2025
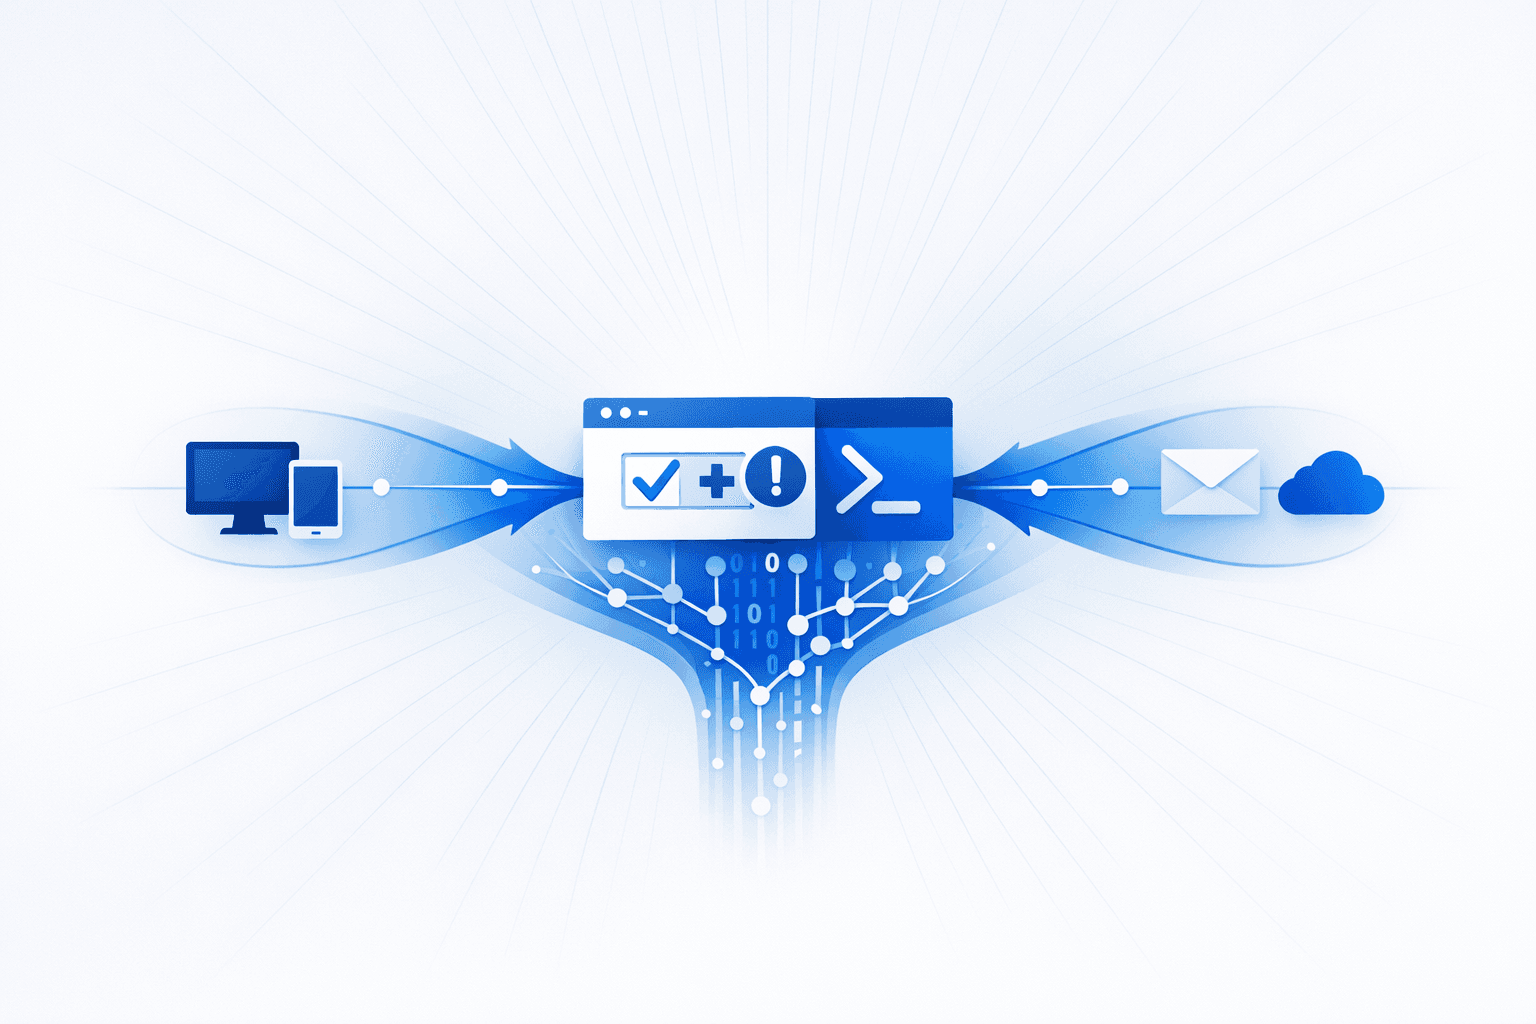
The Russian state-linked advanced persistent threat group COLDRIVER, also known as Star Blizzard, Callisto, and UNC4057, has expanded its cyber-espionage toolkit by launching a new campaign utilizing novel malware payloads. In this operation, COLDRIVER has introduced the BAITSWITCH and SIMPLEFIX payloads, which are delivered through a ClickFix-like campaign targeting individuals and organizations associated with civil society, NGOs, human rights defenders, and think tanks, particularly those with connections to Russia or residing in Western regions. The campaign employs malicious CAPTCHA checks to deceive victims into executing the BAITSWITCH DLL via the Windows Run dialog box. Once executed, BAITSWITCH retrieves the SIMPLEFIX payload, which enables the execution of PowerShell scripts, commands, and remote binaries hosted on external URLs, thereby granting attackers significant control over compromised systems. Security researchers from Zscaler ThreatLabz have highlighted that this campaign closely aligns with COLDRIVER’s established victimology, focusing on entities critical of or exiled from Russia. The use of these new malware strains demonstrates COLDRIVER’s ongoing efforts to update and diversify its attack arsenal, making detection and mitigation more challenging for defenders. The campaign’s technical sophistication is evident in its use of social engineering tactics, such as fake CAPTCHA prompts, to bypass user suspicion and security controls. The deployment of BAITSWITCH and SIMPLEFIX represents a notable evolution from previous COLDRIVER operations, which relied on more traditional phishing and malware delivery methods. The campaign’s infrastructure allows for flexible payload delivery, enabling attackers to adapt their tactics based on the target’s environment. Security analysts have warned that the campaign’s focus on civil society organizations increases the risk of sensitive information theft and potential disruption of advocacy activities. The operation’s timing coincides with heightened geopolitical tensions, further raising concerns about the potential for state-sponsored cyber-espionage to influence international affairs. Defensive recommendations include heightened vigilance for suspicious CAPTCHA prompts, monitoring for unusual DLL executions, and restricting PowerShell and remote binary execution where possible. The campaign underscores the persistent threat posed by Russian APT groups to Western civil society and the need for robust security awareness and technical controls. Organizations are advised to review their security postures and update detection mechanisms to identify the new BAITSWITCH and SIMPLEFIX payloads. The ongoing evolution of COLDRIVER’s tactics highlights the importance of continuous threat intelligence sharing and collaboration among targeted sectors. Security vendors and researchers continue to monitor the campaign for further developments and potential expansion of targeting. The incident serves as a reminder of the sophisticated and adaptive nature of state-linked cyber-espionage operations.