
Loading story…
Lunar Spider, a sophisticated cybercrime group, executed a highly targeted intrusion campaign that began with a single-click attack on a Windows system. The attack was initiated when a user was deceived into opening a JavaScript file disguised as a tax form, which triggered the remote download of an MSI package. This package subsequently launched a Brute Ratel DLL using the rundll32 Windows utility, marking the start of a multi-stage compromise. The attackers quickly injected the Latrodectus malware, which enabled the retrieval of a specialized credential stealer module. Within the first hour, credentials from over two dozen Chromium-based browsers were harvested, along with Microsoft Outlook email and server configurations. The threat actors escalated privileges by running the Isassa.exe binary, granting them high-level access to the domain environment. Throughout the nearly two-month intrusion, Lunar Spider employed a variety of malware, including Brute Ratel C4, Cobalt Strike, BackConnect, and a custom .NET backdoor, to maintain persistence and evade detection. The attackers utilized multiple evasion and persistence mechanisms, ensuring intermittent command and control connections and ongoing access to the compromised environment. Data exfiltration was conducted using Rclone and FTP, with significant file share server data stolen by the twentieth day of the compromise. The operation demonstrated advanced lateral movement and discovery techniques, as the attackers systematically explored the network and harvested credentials from sources such as LSASS, backup software, and Windows Answer files. The campaign highlighted the use of living-off-the-land techniques and the deployment of multiple malware families to achieve their objectives. The incident underscores the importance of user awareness, as the entire compromise stemmed from a single deceptive email attachment. The attackers' ability to maintain access for nearly two months without detection illustrates the sophistication of their tactics and the challenges defenders face. The use of Brute Ratel and Cobalt Strike, both advanced post-exploitation frameworks, enabled the attackers to blend in with legitimate administrative activity. The incident also revealed the threat group's focus on persistence, with multiple fallback mechanisms in place to reestablish access if disrupted. The detailed forensic analysis provided by incident responders offers valuable insights into the attack chain, detection opportunities, and recommended defensive measures. Organizations are advised to enhance email security, monitor for suspicious script execution, and implement robust credential protection strategies to mitigate similar threats.
Mallory correlates global threat intelligence with your attack surface — know if you’re exposed before adversaries strike.
14 events from the most recent confirmed update back to the earliest known activity.
On September 30, 2025, SC Media summarized the DFIR findings, highlighting that a single user click enabled a Windows compromise attributed to Lunar Spider. The coverage emphasized the attack chain and prolonged access described in the underlying report.
On September 29, 2025, The DFIR Report published a case study detailing the near two-month intrusion, its tooling, and its links to the Lunar Spider and Latrodectus ecosystem. The report provided technical details on initial access, persistence, lateral movement, and exfiltration.
On October 30, 2024, reporting described a recent LUNAR SPIDER campaign targeting financial-sector victims via malvertising and SEO-poisoned tax-themed lures that delivered an obfuscated Latrodectus JavaScript loader, MSI installer, and Brute Ratel C4. The analysis also documented persistence through a Windows Run key and infrastructure overlaps linking Latrodectus with IcedID and ransomware-associated ecosystems.
The actor maintained intermittent command-and-control access for almost two months using BackConnect, Latrodectus, Brute Ratel, and Cobalt Strike before being evicted from the environment. No ransomware deployment was observed during the incident.
In June 2024, tax-themed campaigns reappeared using Latrodectus v1.3 together with Brute Ratel after the Operation Endgame disruption. The report links this resurgence to the broader Lunar Spider and Latrodectus tradecraft ecosystem.
Later in the intrusion, the actor targeted backup infrastructure by running Veeam-Get-Creds.ps1 and conducted network scanning with rustscan. These actions suggested preparation for additional access or impact, although no ransomware deployment was observed.
From May 27 to May 29, 2024, Operation Endgame disrupted infrastructure associated with Latrodectus. The DFIR report cites this law enforcement action as relevant to the broader ecosystem tied to the intrusion.
On day 20 of the intrusion, the actor exfiltrated data from a file share server using a renamed rclone binary over FTP for roughly 10 hours. This marked a significant impact phase of the compromise.
During the intrusion, the threat actor also tried further lateral movement using a custom Zerologon exploit tool, zero.exe, targeting CVE-2020-1472, along with a failed Metasploit remote-service attempt. These efforts reflected continued expansion attempts inside the victim network.
After escalating privileges, the actor moved laterally with PsExec following an unsuccessful WMIC attempt, deployed multiple Cobalt Strike beacons, and installed a custom .NET backdoor named lsassa.exe for scheduled-task persistence and command-and-control.
By the third day of the intrusion, the actor recovered plaintext domain administrator credentials from an exposed unattend.xml Windows Answer file. This enabled rapid privilege escalation and broader Active Directory reconnaissance with AdFind.
Within hours of the initial infection, the threat actor deployed BackConnect/VNC to obtain interactive remote access to the environment. This expanded their ability to operate persistently on compromised systems.
Shortly after initial compromise, Latrodectus established command-and-control through multiple Cloudflare-proxied domains and retrieved a stealer module. The actor then performed host and domain reconnaissance using built-in Windows commands.
In May 2024, the intrusion began when a user executed a heavily obfuscated tax-themed malicious JavaScript file linked to the Lunar Spider initial access ecosystem. The script downloaded an MSI that launched a Brute Ratel DLL through rundll32, which then injected the Latrodectus downloader into explorer.exe.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 122 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
3 references tracked. Mallory keeps watching after this page renders.
scworld.com
Open sourcethedfirreport.com
Open sourcecontagiodump.blogspot.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Threat actors are increasingly relying on *living-off-the-land* techniques and trusted tooling to establish persistent access on Windows endpoints. One campaign used weaponized Windows shortcut (`.LNK`) files disguised as investment-related PDFs to deliver **MoonPeak**, a remote access trojan assessed as a **XenoRAT** variant and linked to North Korea–aligned activity targeting South Korean investors and cryptocurrency traders. Opening the `.LNK` launches an obfuscated PowerShell-driven, multi-stage infection chain while displaying a decoy PDF; analysis also tied payload hosting to attacker-controlled GitHub repositories, reflecting “Living Off Trusted Sites (LOTS)” tradecraft. A separate dual-wave intrusion chain used phishing emails masquerading as *Greenvelope* invitations to steal webmail credentials (e.g., Outlook, Yahoo, AOL), then used the compromised accounts to register for and silently deploy **LogMeIn Resolve** (formerly *GoTo Resolve*) for persistent remote access. The installer (`GreenVelopeCard.exe`) was described as signed and configured to connect to attacker-controlled infrastructure, with follow-on actions including modifying service settings for elevated access and creating hidden scheduled tasks for resilience. Related threat intelligence reporting also highlighted broader “rogue RMM” abuse trends, including **Remcos** and **NetSupport Manager** delivery via paste-and-run lures and PowerShell/`cmd` execution chains (including use of the `finger` utility to fetch remote payloads), underscoring that adversaries are operationalizing legitimate remote administration software as a stealthy backdoor mechanism.
Jun 29, 2026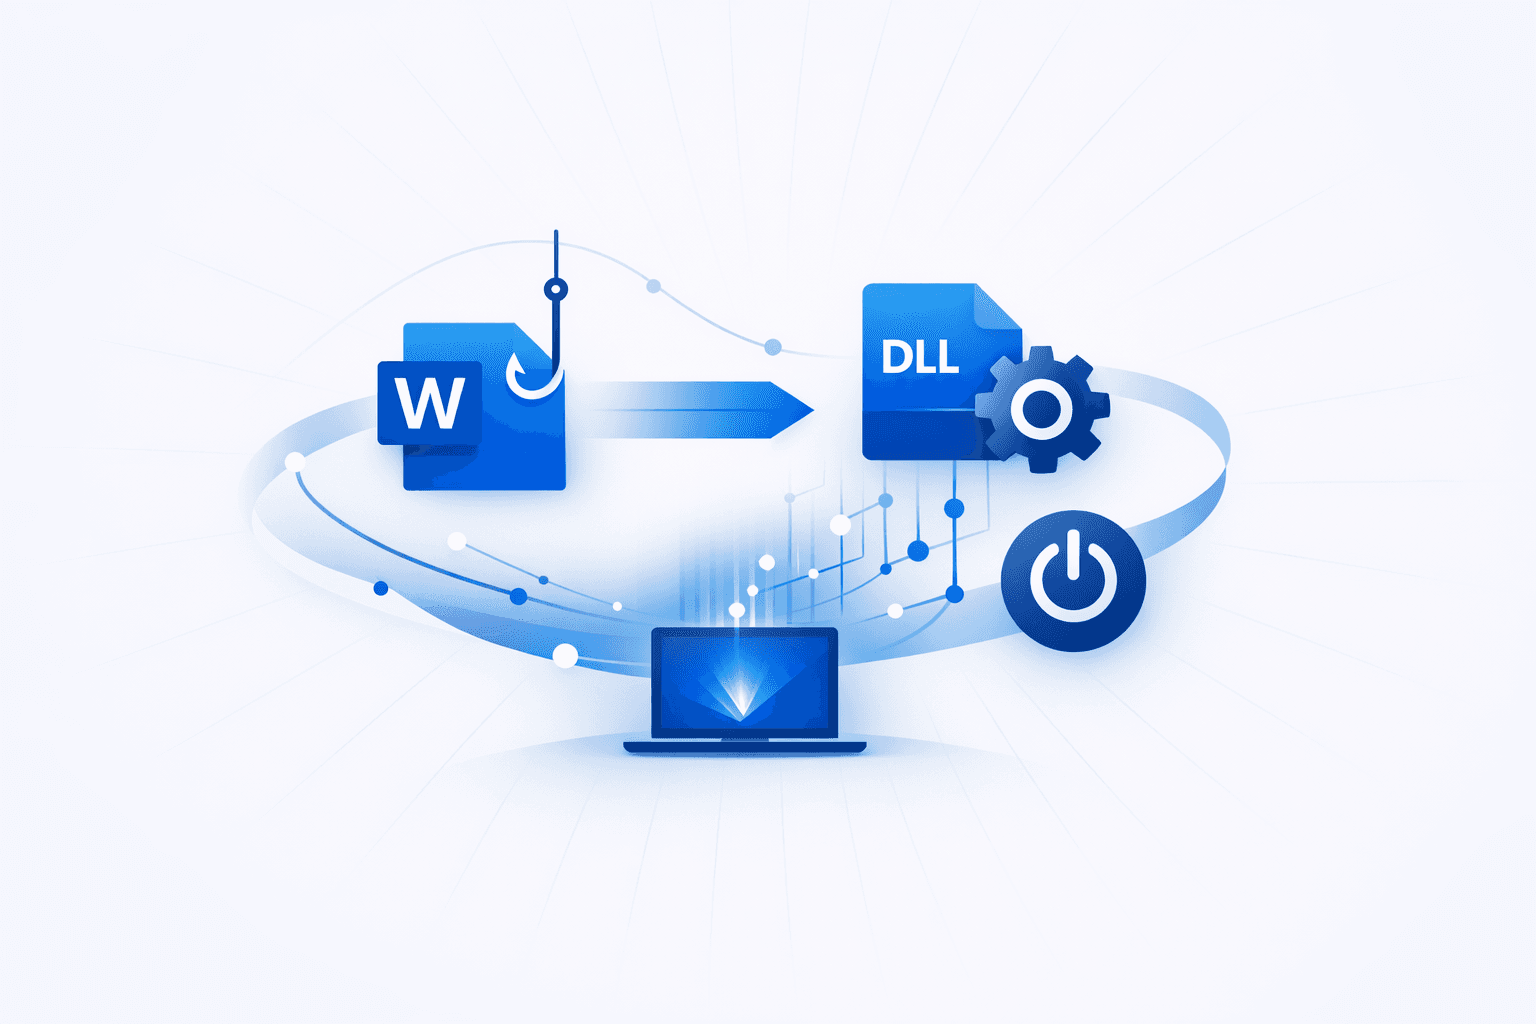
The **Lazarus Group** ran a spearphishing campaign that delivered malicious Microsoft Word documents to targets in aerospace, defense, research, and financial sectors, including organizations linked to Boeing, BAE Systems, Lockheed Martin, and the Republic of Korea Army. The infection chain used remote template injection to fetch an external `DOTM` file, whose macro dropped a lure document and a malicious DLL such as `onenote.db` into the victim’s `AppData` path, then executed the implant while showing a decoy file to reduce suspicion. Related reporting describes similar Lazarus lures sent in spoofed emails, with separate payloads for 32-bit and 64-bit systems and reconnaissance-focused first-stage malware. The implant executed through **`rundll32.exe`** and established persistence via the Windows **Startup folder**, techniques widely tracked in MITRE ATT&CK as `T1218.011` and `T1547.001`. Once active, it collected host, process, and disk information, compressed or encrypted the data, and exfiltrated it over HTTP POST using compromised or attacker-controlled infrastructure, including IIS/Plesk-hosted domains such as `elite4print.com` and `astedams.it`. Analysts linked the activity to Lazarus based on recurring tradecraft, lure themes, victim profiling, and overlap with operations such as **Operation Dream Job**, where the group similarly abused `rundll32.exe` and autostart mechanisms for stealthy execution and persistence.
Aug 15, 2026
Multiple campaigns are using phishing emails and archive-based lures to deliver remote access malware through stealthy, multi-stage infection chains. Point Wild documented **Remcos RAT**, **DesckVB RAT**, and a Rust-based **COVERT RAT** being delivered through ZIP attachments, weaponized `LNK` files, obfuscated JavaScript droppers, and hidden PowerShell execution, often with decoy documents to mask activity. The payloads were loaded filelessly through .NET reflection and in-memory execution, with operators abusing legitimate binaries and services such as `aspnet_compiler.exe`, GitHub, and paste or web-hosting platforms to stage malware while evading detection. Reported command-and-control infrastructure included `192.3.27.141:8087`, `172.245.246.77:8080`, and `181.231.253.69:4444`, while observed artifacts included `C:\ProgramData\remcos\logs.dat`, `C:\ProgramData\colors\logs.dat`, and payload names such as `ALTERNATE.dll`, `ClassLibrary3.dll`, `Keylogger.dll`, and `msedge_proxy.exe`. Separate reporting showed the same tradecraft extending beyond custom RATs to commodity remote-access software and credential theft. A campaign targeting Russian aerospace and aviation organizations used invoice-themed phishing and spoofed domains to install a portable **AnyDesk** instance for unattended access, maintain persistence with a scheduled task, minimize visibility with Tray Minimizer, and exfiltrate configuration data through a command-line SMTP mailer; Seqrite linked the activity to **Rare Werewolf (Librarian Ghouls)**. Securonix research cited by Trojan Killer described **VEIL#DROP** using fake document-style JavaScript files, Blogspot-hosted staging, PowerShell download cradles, XOR decoding, and in-memory .NET loading to deploy **PureLog Stealer**, which targets browser credentials, cookies, session tokens, wallet data, and host information. Across the campaigns, the common pattern is phishing-led initial access followed by LOLBins, PowerShell, staged downloads, persistence, and covert data theft or long-term remote control.
Jul 12, 2026