
Loading story…
Threat actors are distributing the Guloader malware through phishing emails disguised as employee performance reports. These emails claim to provide information about staff evaluations and potential dismissals, enticing recipients to open a compressed RAR file attachment. The archive contains an executable file named to appear as a PDF document, which, when run, deploys Guloader. This malware then downloads and executes shellcode from a remote server, ultimately installing Remcos RAT on the victim's system.
Remcos RAT enables attackers to perform a range of malicious activities, including keylogging, screenshot capture, webcam and microphone control, and the extraction of browser histories and passwords. The campaign leverages legitimate cloud storage services for command and control, increasing the difficulty of detection. Security researchers have provided indicators of compromise, such as specific MD5 hashes and C2 addresses, to aid in defense against this threat. Users are advised to exercise caution with unexpected emails and regularly update passwords to mitigate risk.

Get the infrastructure and lures behind it.
3 events from the most recent confirmed update back to the earliest known activity.
AhnLab disclosed technical indicators for the campaign, including the malicious file MD5 hash c95f2a7556902302f352c97b7eed4159 and Remcos RAT command-and-control communications to 196.251.116.219 over ports 2404 and 5000. Additional indicators were made available through AhnLab TIP.
In the observed infection chain, executing the fake document launched Guloader, which retrieved shellcode from a Google Drive URL and loaded Remcos RAT. The RAT provided remote access and surveillance capabilities including keylogging, screenshot capture, webcam and microphone access, and credential theft.
A phishing campaign was identified that used emails about employee performance reports and possible dismissals to trick recipients into opening a malicious RAR attachment. The archive contained an NSIS executable named "staff record pdf.exe" disguised as a document.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Attackers are distributing Guloader malware through phishing emails that masquerade as employee performance reports, exploiting workplace trust and urgency to trick recipients into opening malicious attachments. The emails, purporting to be from HR or management and referencing October 2025 performance reviews, use psychological manipulation by suggesting potential dismissals, increasing the likelihood that employees will open the attached file. The attachment is a compressed archive containing an executable file disguised as a PDF (e.g., 'staff record pdf.exe'), which, if file extensions are hidden, appears innocuous but actually initiates a multi-stage infection process upon execution. Once launched, the executable connects to a remote server—specifically a Google Drive URL—to download encrypted shellcode and further payloads. The infection chain ultimately leads to the deployment of Guloader, which can then download additional malware such as Remcos RAT, providing attackers with persistent access and control over the victim's system. This campaign leverages trusted cloud services to evade detection and highlights the ongoing evolution of social engineering tactics targeting organizations through familiar business processes and documents.
Jun 29, 2026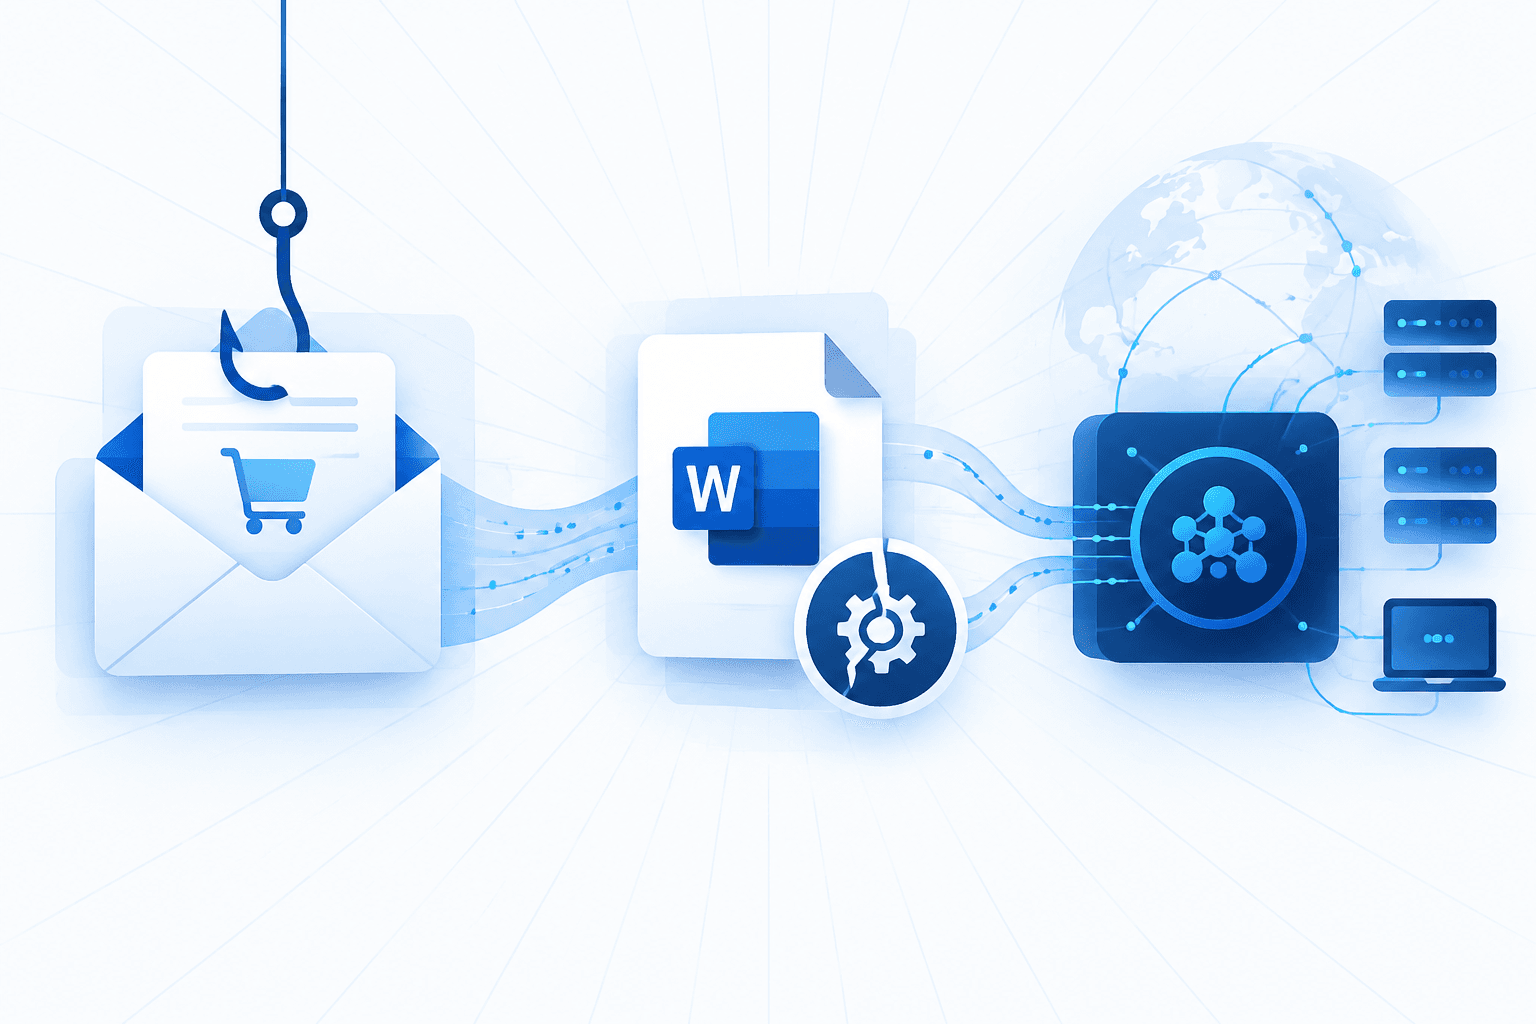
A phishing campaign impersonated employees of a South Korean company and sent project-material purchase-request emails carrying malicious XLS attachments. The spreadsheet displayed a credible decoy purchase form but exploited the Microsoft Office OLE2Link remote-code-execution flaw, `CVE-2017-0199`, to retrieve a malicious HTA payload. The HTA invoked WMI `Win32_Process.Create` to launch obfuscated PowerShell, which downloaded a steganographic PNG containing an in-memory .NET loader. The loader deployed **Remcos RAT**, giving operators remote command execution and the ability to collect system and user data, log keystrokes, capture screens, manipulate files, and exfiltrate data through command-and-control infrastructure.
Sep 30, 2026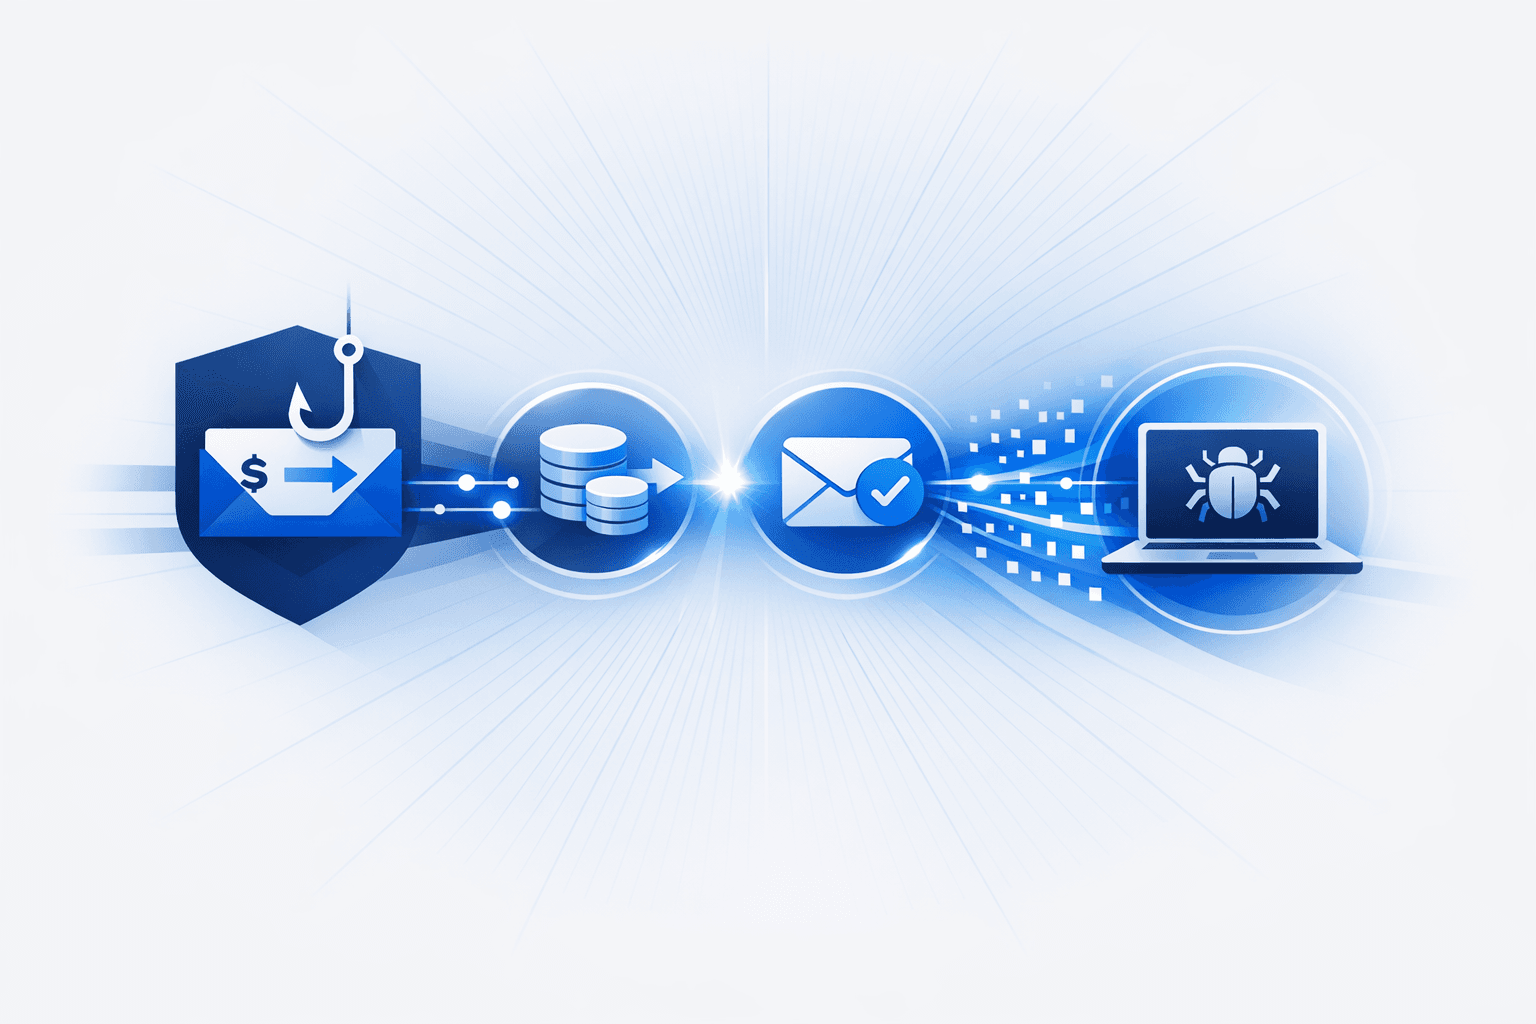
A phishing campaign is using emails disguised as payment or money transfer confirmations to trick recipients into opening a malicious **XLS** attachment. The messages impersonate employees of a specific company in Korea and present the spreadsheet as a legitimate payment slip, using a financial transaction lure to increase the likelihood that targets will open the file. When opened, the attachment exploits **`CVE-2017-0199`** in Microsoft Office to retrieve a remote **HTA** payload. The HTA then uses **WMI `Win32_Process.Create()`** to launch an obfuscated PowerShell script that downloads a steganographic **PNG** file, extracts and decrypts an in-memory **.NET** loader from embedded Base64 data, and ultimately installs **Remcos RAT**. The malware gives attackers remote access, including command execution, keylogging, screen capture, file manipulation, and data exfiltration to command-and-control infrastructure.
Jul 13, 2026