ClickFix Social-Engineering Campaigns Using Fake CAPTCHA and Fake Installer Pages
Attack Tradecraft · 2 sources · Updated 4mo ago · First seen Feb 17, 2026
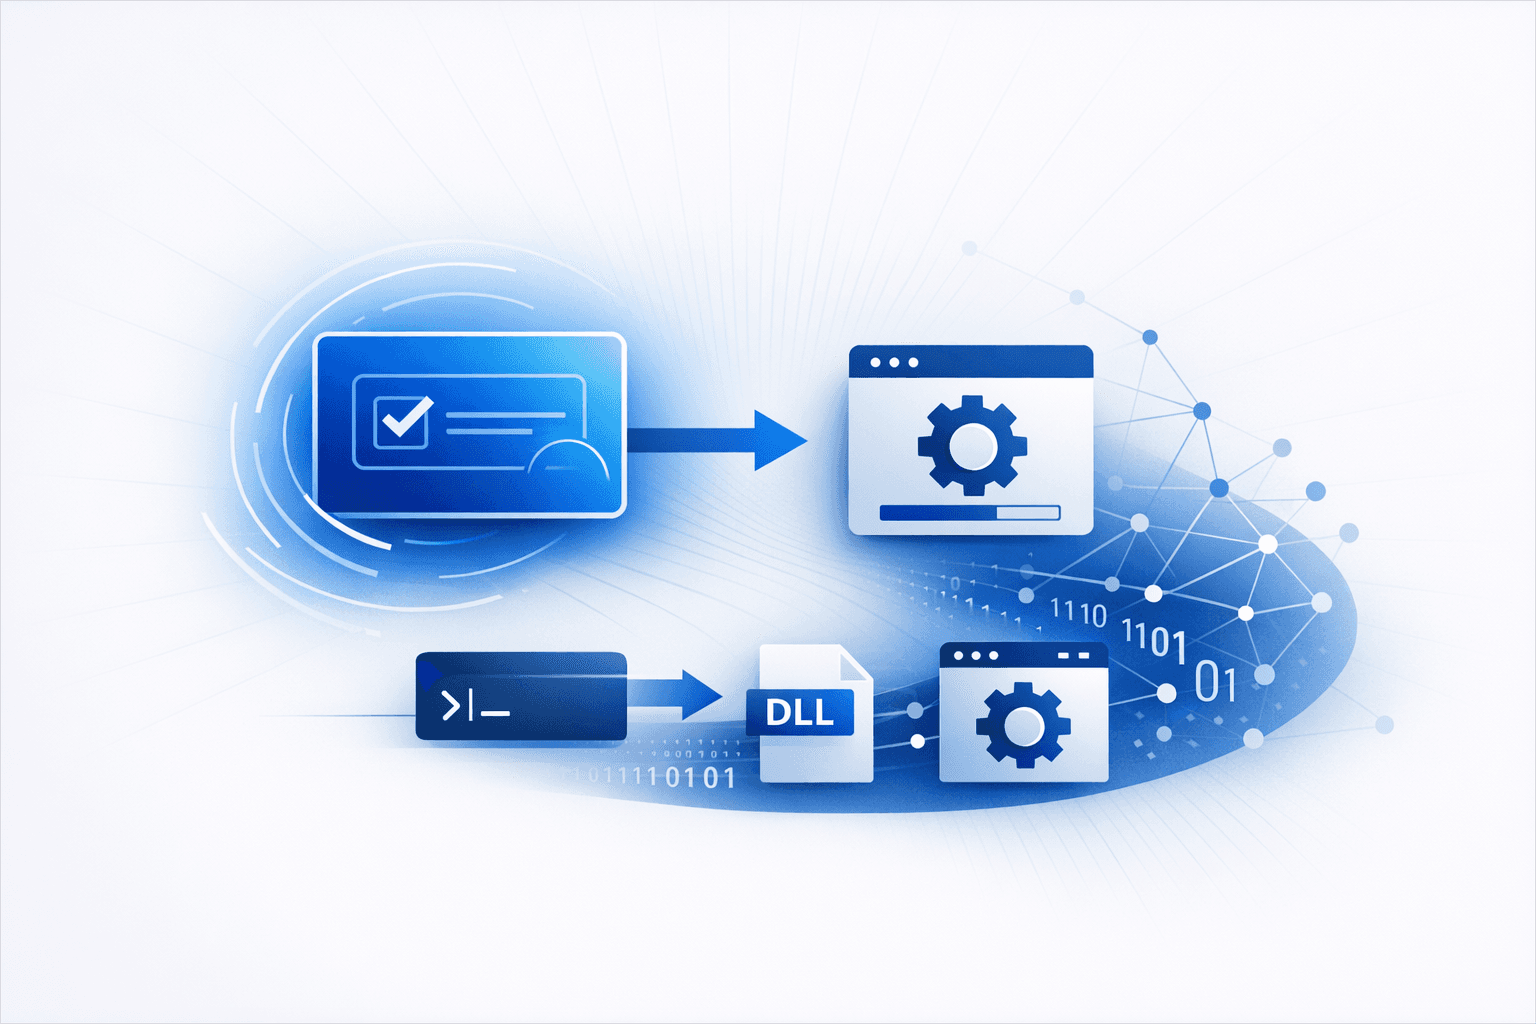
Security researchers reported multiple ClickFix campaigns that compromise endpoints by tricking users into manually executing attacker-provided commands rather than exploiting a software vulnerability. CERT Polska documented an incident response at a large Polish organization where a fake CAPTCHA prompt led a user to run a malicious snippet via Win+R, resulting in malware execution and suspected DLL side-loading from %APPDATA%\Intel (legitimate igfxSDK.exe/version.dll alongside a suspicious wtsapi32.dll). Investigators also identified additional suspicious DLLs in the user’s local AppData and recovered an execution trail consistent with a one-liner that fetched remote content and piped it into PowerShell (e.g., cmd /c curl ... | powershell).
Separately, threat hunting research described a macOS-focused ClickFix operation using typosquatted Homebrew lookalike sites to present a “copy/paste” install command that runs in Terminal. The first-stage script repeatedly prompted for a password and validated it using dscl authonly to harvest working credentials before deploying a second-stage infostealer dubbed Cuckoo Stealer, which was reported to establish LaunchAgent persistence, remove quarantine attributes, and communicate over encrypted HTTPS C2 while targeting browser credentials/session tokens, Keychain data, notes/messaging artifacts, VPN/FTP configs, and cryptocurrency wallets. Both reports highlight ClickFix as an increasingly common, opportunistic initial access technique that scales by abusing trusted user workflows on Windows and macOS.