
Loading story…
Security researchers reported new banking malware campaigns targeting Brazilian users and financial institutions, with one operation focused on Android devices and Brazil's Pix instant payment ecosystem, and another aimed at Windows users of at least 33 Brazilian banks. The Android trojan, dubbed PixRevolution, was identified by Zimperium as malware built to hijack mobile payments in real time, using a human operator to intervene at the moment of transaction and redirect funds. The campaign reflects the continued attractiveness of Brazil's heavily used digital payment environment to financially motivated attackers.
A separate but related report described VENON, a Rust-based Windows banking trojan disclosed by ZenoX that uses banking overlays, active window monitoring, and LNK hijacking techniques associated with Latin American banking malware. Researchers said VENON is delivered through a multi-stage infection chain involving DLL side-loading, likely social engineering, and a PowerShell-based downloader, then applies anti-analysis measures such as AMSI bypass, ETW bypass, anti-sandbox checks, and indirect syscalls before contacting cloud infrastructure. One additional reference about malicious Rust crates targeting developer secrets is not part of the same event, as it concerns software supply chain theft rather than banking malware aimed at Brazilian financial users.
See the actors and campaigns active against you right now.
3 events from the most recent confirmed update back to the earliest known activity.
Researchers disclosed a new Android banking trojan dubbed PixRevolution that targets Brazil's Pix instant payment system. The malware is spread via fake Google Play pages, abuses an accessibility service for device control, and enables operators to hijack transfers in real time by showing a fake wait overlay while redirecting funds.
Researchers reported a new Rust-based banking malware family called VENON targeting users in Brazil, marking a shift from the region's more common Delphi-based banking trojans. The malware was described as targeting 33 banks and digital asset platforms through a multi-stage DLL side-loading chain, banking overlays, shortcut hijacking, and multiple evasion techniques.
An earlier sample of the Rust-based Windows banking malware later named VENON was dated January 2026. Researchers noted developer path references to the username "byst4" and assessed the code structure may indicate AI-assisted development.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
See the adversaries and campaigns active against your sector right now, ranked by what they're exploiting.
3 references tracked. Mallory keeps watching after this page renders.
scworld.com
Open sourcedarkreading.com
Open sourcethehackernews.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
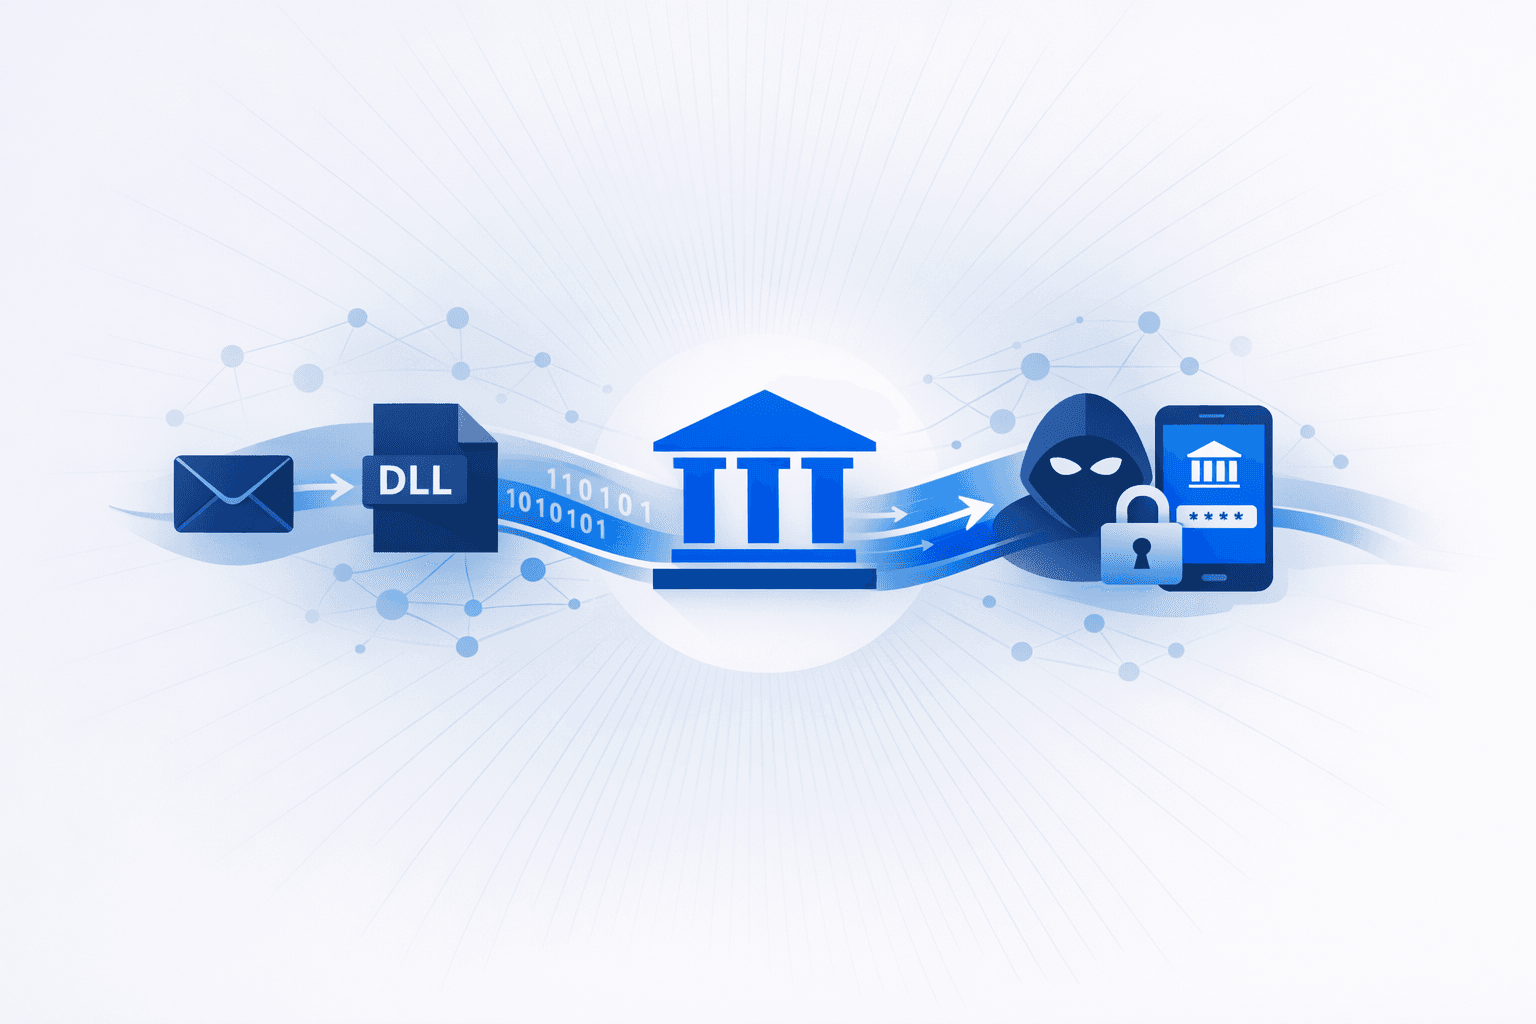
Multiple malware campaigns targeted users and organizations in Brazil with Latin American banking trojans including **Metamorfo** and **Mispadu/URSA**, using invoice-themed spam, malicious URLs, ZIP archives, MSI installers, and multi-stage loaders to infect Windows systems. Researchers reported delivery chains involving PowerShell, VBScript, AutoIT, and Delphi payloads, as well as abuse of `msiexec.exe`, AWS-hosted infrastructure, and DLL search-order hijacking through a renamed legitimate `VBoxTray.exe` binary that side-loaded a malicious `mpr.dll` file. The malware was built to steal banking credentials and broader account data through keylogging, fake banking pop-ups and overlays, and credential-harvesting tools such as NirSoft utilities, while some variants also sought CVV and two-factor authentication details. Reporting tied the activity to infrastructure largely observed in Brazil, a spam botnet with more than 700 compromised systems and over 4,000 fraudulently created BOL email accounts, and a later campaign that targeted up to 98 Brazilian organizations across IT, professional services, manufacturing, financial services, and government.
Aug 15, 2026
Check Point Research reported that **PixStealer**, an Android banking trojan, abuses the operating system's **Accessibility Services** to steal credentials and intercept financial activity on infected devices. The malware targets Brazil's instant payment ecosystem, particularly the **Pix** platform, and is designed to harvest sensitive banking information, manipulate on-screen activity, and facilitate fraudulent transactions by abusing permissions intended to assist users with disabilities. The campaign reflects a broader evolution in mobile banking malware, with attackers relying on accessibility abuse to gain extensive control over victim devices, monitor apps, capture input, and bypass normal user protections. By focusing on a widely used real-time payment method and leveraging trusted Android features, PixStealer increases the risk of account takeover and unauthorized transfers for mobile banking users and financial institutions operating in the region.
Jul 12, 2026
Brazilian banking malware has evolved from basic keyloggers and phishing Trojans into more sophisticated toolsets that use obfuscation, encryption, process injection, browser automation, remote administration, and even ransomware techniques. Researchers said operators adapted quickly to banking defenses such as virtual keyboards, machine fingerprinting, and two-factor authentication by shifting to mouseloggers, hosts-file redirection, Internet Explorer automation, RunPE-style loaders, AutoIt and .NET crypters, and live operator-controlled remote access Trojans, with code quality and operational tradecraft improving markedly over time. One delivery method highlighted in later activity used malformed ZIP archives prefixed with a UTF-8 Byte Order Mark to evade some email scanners and make the files appear corrupted to certain tools while remaining extractable with common utilities. The recovered loader decrypted an embedded DLL from its resources with an XOR-based routine, executed the exported function `BICDAT`, then fetched a second-stage password-protected ZIP that delivered a Banking RAT seen broadly in Brazil and Chile, underscoring how Brazilian cybercriminals combined local banking fraud expertise with increasingly advanced malware packaging and execution chains.
Aug 15, 2026