SmartApeSG ClickFix Campaign Delivering Remcos RAT
Malware Intelligence · 2 sources · Updated 4mo ago · First seen Mar 14, 2026
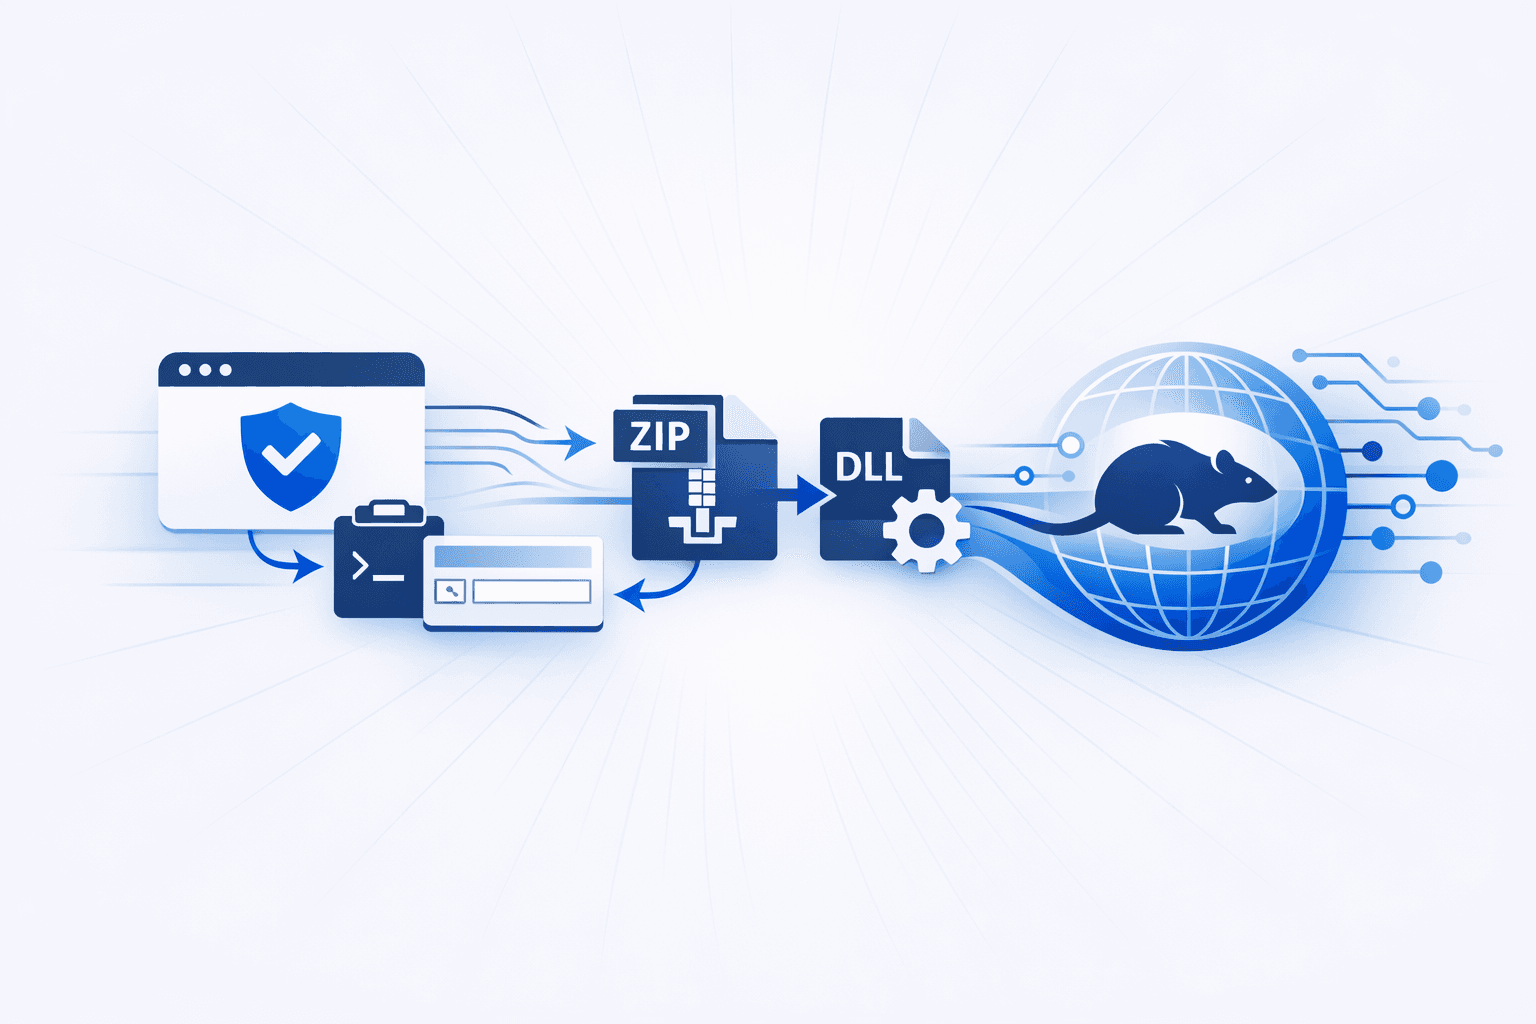
The SmartApeSG campaign is using compromised legitimate websites to inject malicious JavaScript that presents a fake CAPTCHA and ClickFix-style instructions, tricking users into opening the Windows Run dialog, pasting a clipboard-loaded command, and executing the next stage themselves. In the observed infection chain, the payload was delivered as a ZIP archive disguised with a .pdf extension, then executed via DLL side-loading to install Remcos RAT and establish persistence through a Windows Registry modification. The reporting ties this activity to infrastructure and indicators previously associated with SmartApeSG, also tracked as ZPHP and HANEYMANEY.
A separate report on a new ClickFix variant is relevant because it documents the same broader social-engineering delivery technique, but with a different infection chain: a fake CAPTCHA leads victims to run a command that maps a remote WebDAV share using net use, launches update.cmd, downloads a ZIP archive, and executes a trojanized WorkFlowy application containing malicious logic in an .asar archive that acts as both a C2 beacon and dropper. Other references describe unrelated APT campaigns, malware families, or vendor detection updates and do not cover the SmartApeSG/Remcos activity itself.