SmartApeSG ClickFix Pages Deliver NetSupport RAT and Stealc
Malware Intelligence · 3 sources · Updated 3mo ago · First seen Aug 13, 2026
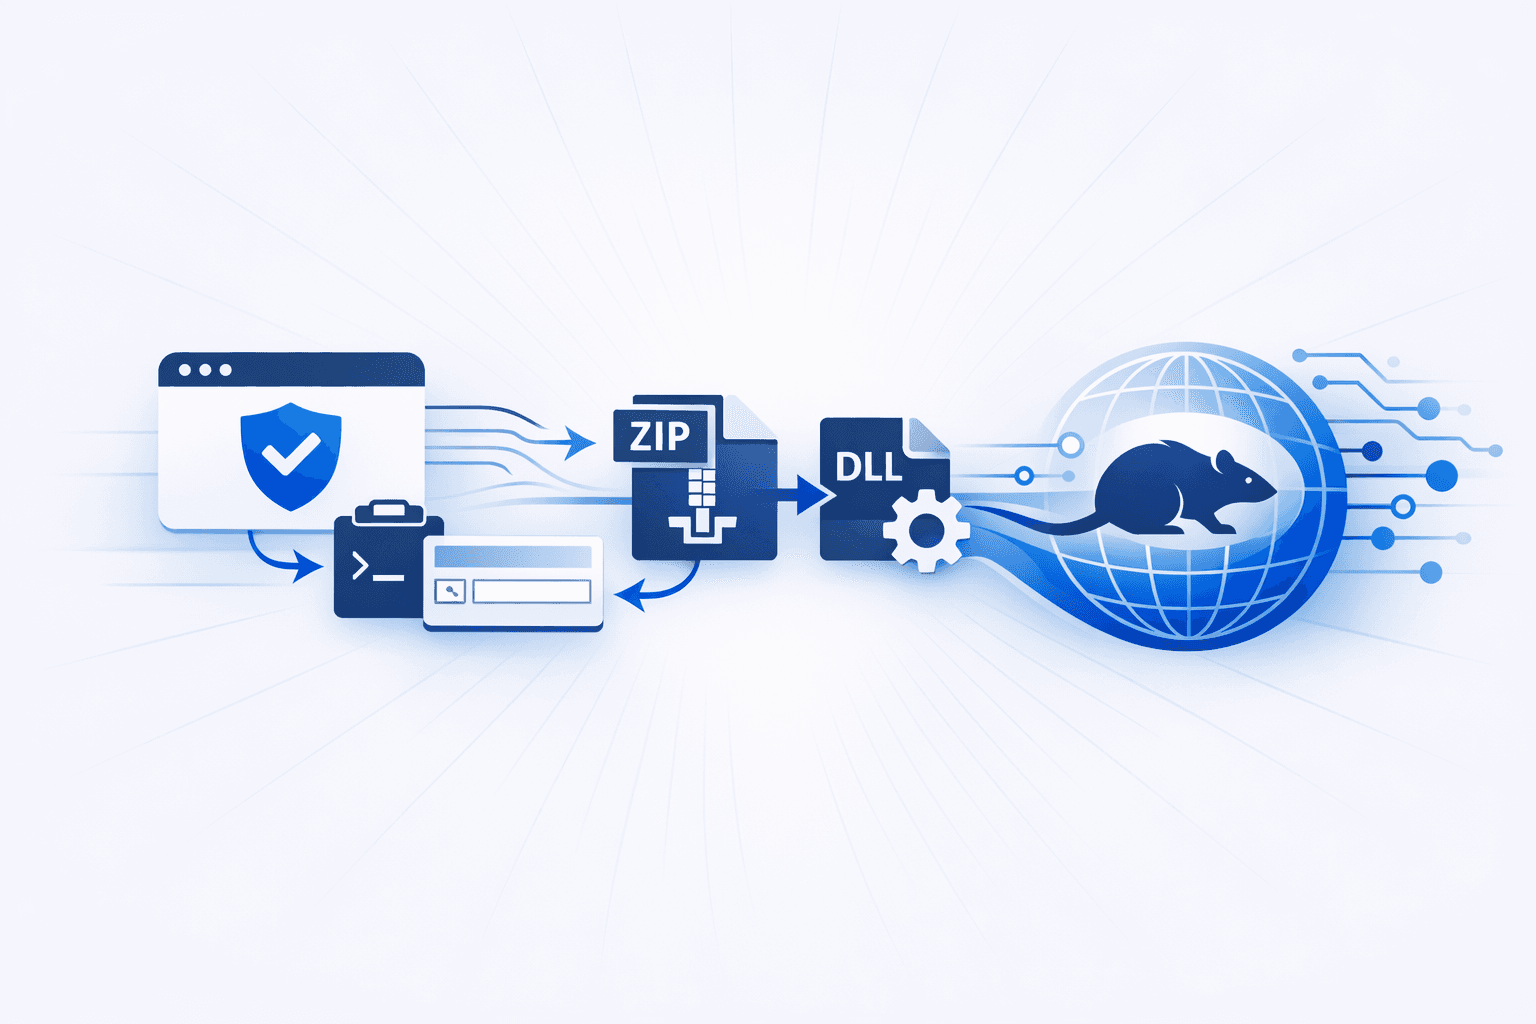
The SmartApeSG campaign has been using compromised websites to display fake CAPTCHA or browser-verification pages that trick users into launching a malicious command, shifting from earlier fake browser update lures to ClickFix-style social engineering. In observed infections, hidden injected scripts selectively present a “verify you are human” prompt, copy an mshta-based command to the victim’s clipboard, and instruct the user to paste it into the Windows Run dialog, triggering retrieval of additional payloads from attacker-controlled infrastructure.
Analysis of multiple infection chains shows the activity leading to NetSupport RAT and, in some cases, a second payload such as Stealc v2 or another RAT. Researchers reported a ZIP-delivered NetSupport package, persistence via a Start Menu shortcut that launches a .js file from the user’s Temp directory and then executes the RAT from C:\ProgramData\, while packet captures and recovered samples from later cases indicate traffic associated with two separate remote access trojans. The campaign is also tracked as ZPHP or HANEYMANEY, and its domains, payload packages, and command-and-control infrastructure have been observed changing frequently.