Hugging Face Diffusers Flaws Let Malicious Model Repositories Execute Code
Emerging Technology Risk · 4 sources · Updated 3mo ago · First seen Aug 3, 2026
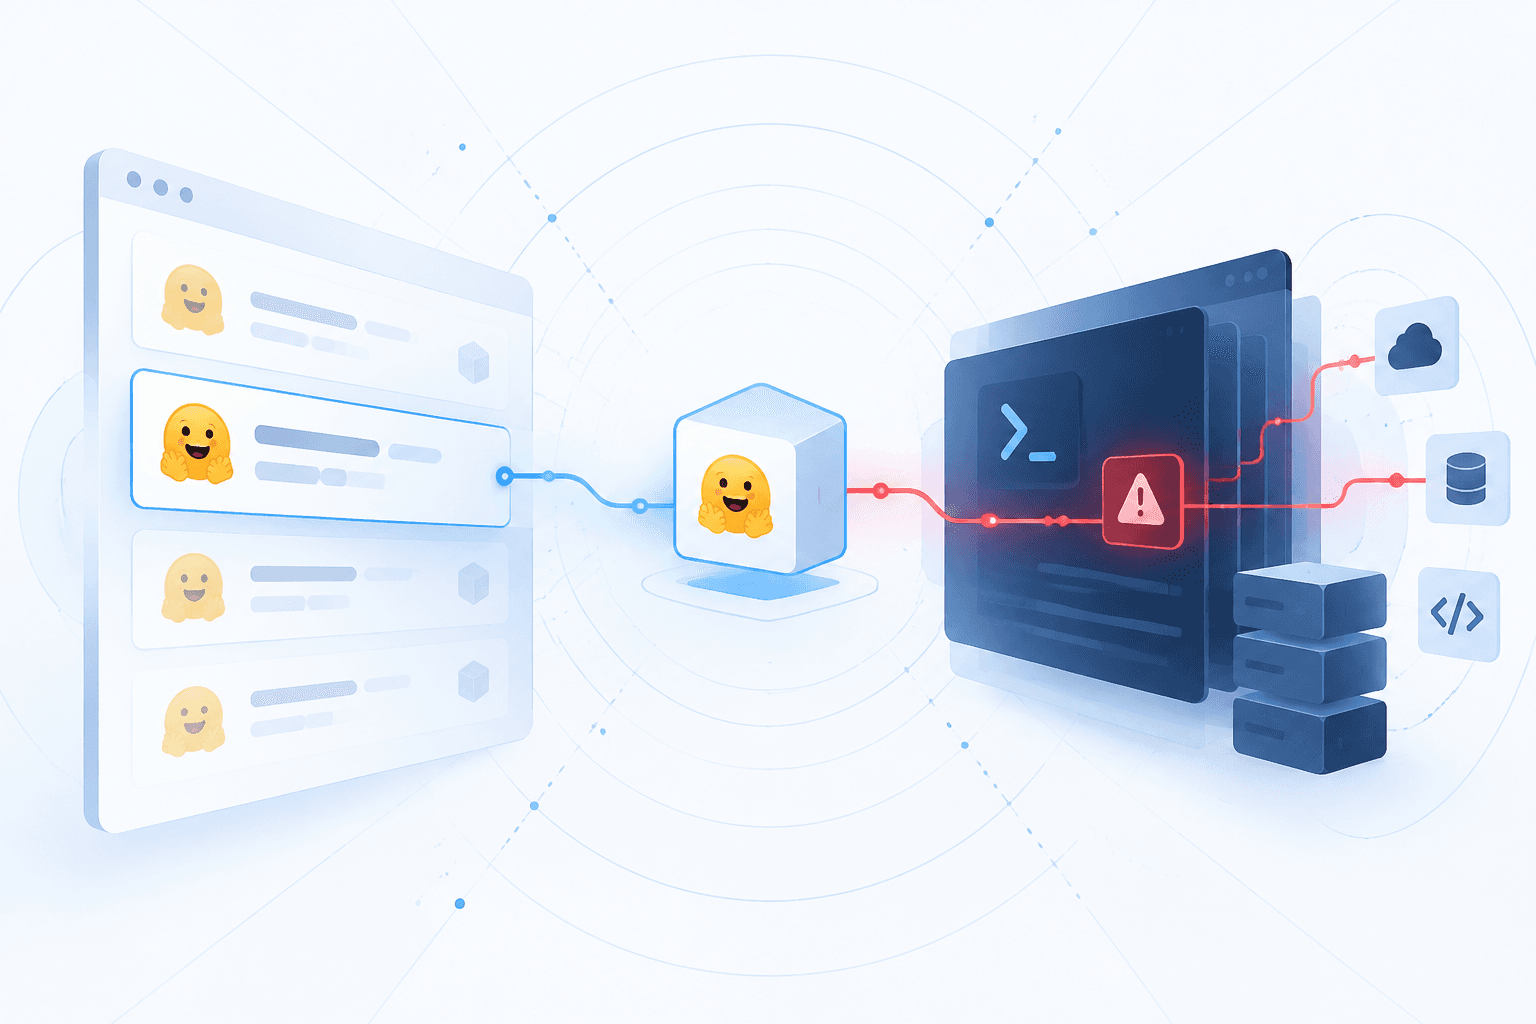
Researchers disclosed three high-severity vulnerabilities in Hugging Face’s Diffusers library that allow a crafted model repository to bypass the trust_remote_code safeguard and execute arbitrary code when a model is loaded. The issues, collectively dubbed FaceHugger, affect workflows using DiffusionPipeline.from_pretrained with custom pipelines and stem from time-of-check to time-of-use flaws in the model download and loading process, where trust validation occurs before later content can be swapped or injected through non-atomic HTTP requests.
The disclosure names CVE-2026-44827, CVE-2026-45804, and variants grouped under CVE-2026-44513, and also points to a related trust issue in Hugging Face’s Transformers library involving pinned commit hash propagation. Because Diffusers is widely used in production AI pipelines, CI/CD environments, and containerized workloads, successful exploitation could turn a routine model pull into an enterprise initial-access vector. The vulnerabilities were patched in Diffusers 0.38.0, and defenders are being urged to upgrade, pin repository revisions, and treat AI model repositories as untrusted executable content.