Unsloth Studio RCE Triggered by Selecting Malicious Hugging Face Models
Emerging Technology Risk · 3 sources · Updated 2mo ago · First seen Jun 18, 2026
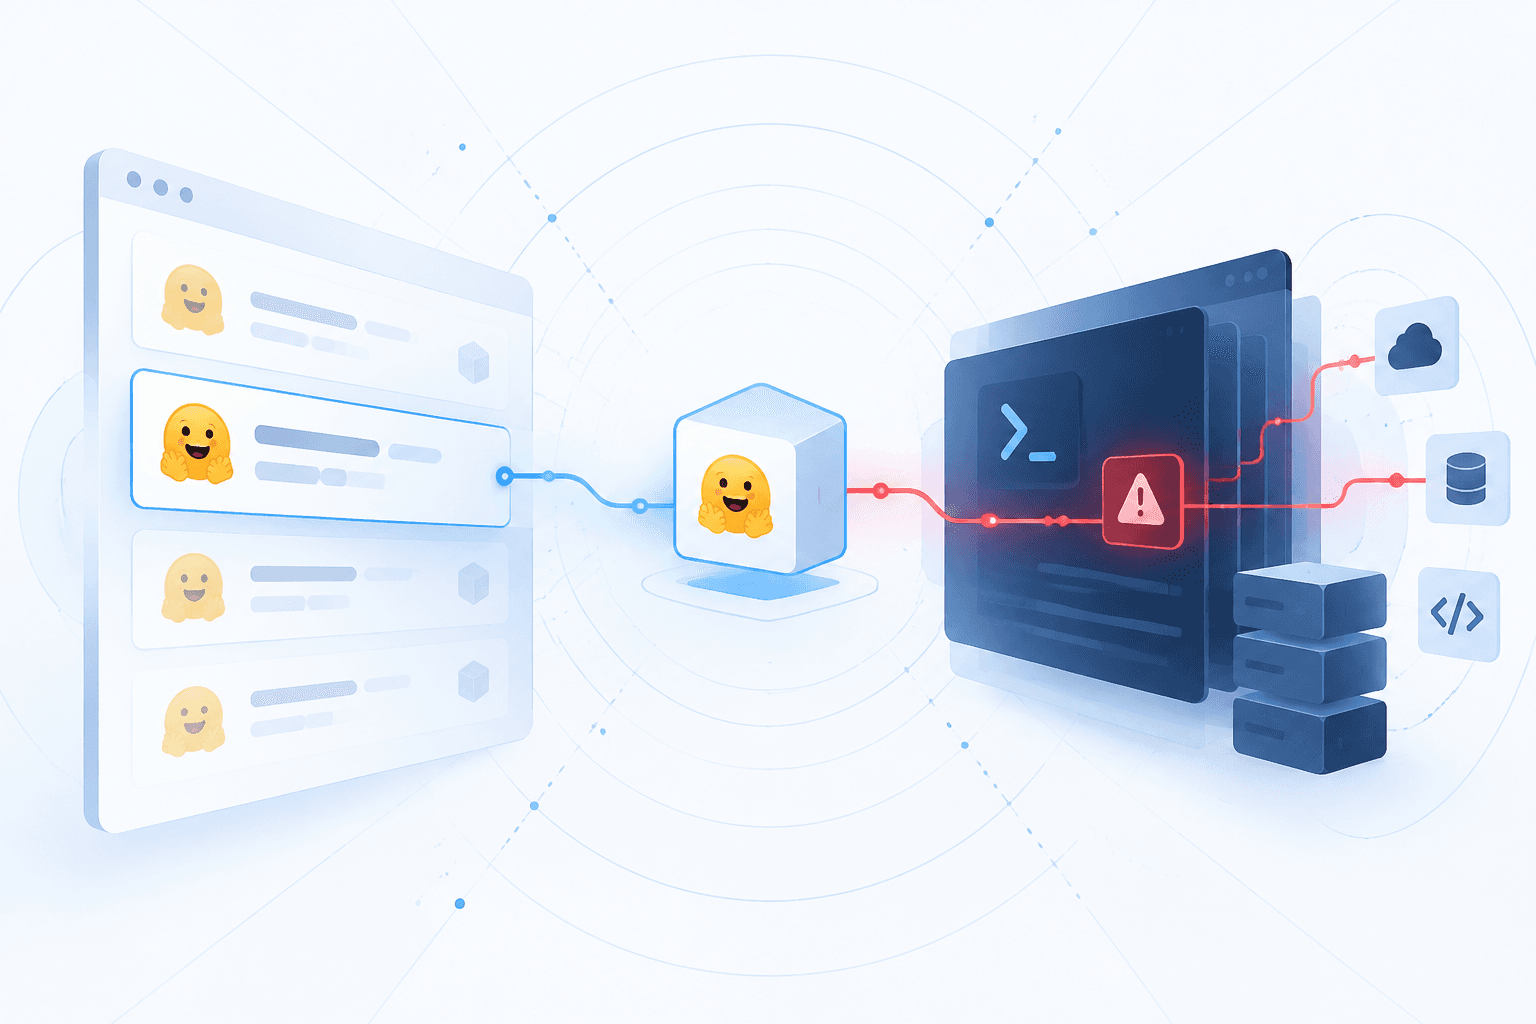
A now-patched remote-code-execution flaw in Unsloth Studio allowed attacker-controlled Hugging Face model repositories to run arbitrary Python code when an operator merely selected a model in the Studio browser interface. The backend inspection workflow enabled trust_remote_code=True by default, allowing a crafted config.json auto_map entry to make Hugging Face Transformers import Python modules supplied by the repository; exploitation did not require loading model weights, starting inference or training, or separately approving remote code execution.
The payload ran with the Studio operator's privileges and could expose Hugging Face tokens, cloud credentials, SSH keys, proprietary datasets, and model artifacts. Pillar Security privately reported the issue in early June 2026, and Unsloth fixed it in version 2026.6.9 on June 18; no CVE or public advisory was issued because Studio was in beta. Organizations using Studio should upgrade to 2026.6.9 or later and isolate model-loading workflows from sensitive credentials and resources.