Mallory
← Back to News
phishing-campaign-intelligenceremote-access-implantpersistence-methodcommand-and-control-method

Photo ZIP Phishing Campaign Hits Hotels With TonRAT Node.js Implant

Social Engineering & Fraud · 11 sources · Updated 3mo ago · First seen Jun 26, 2026
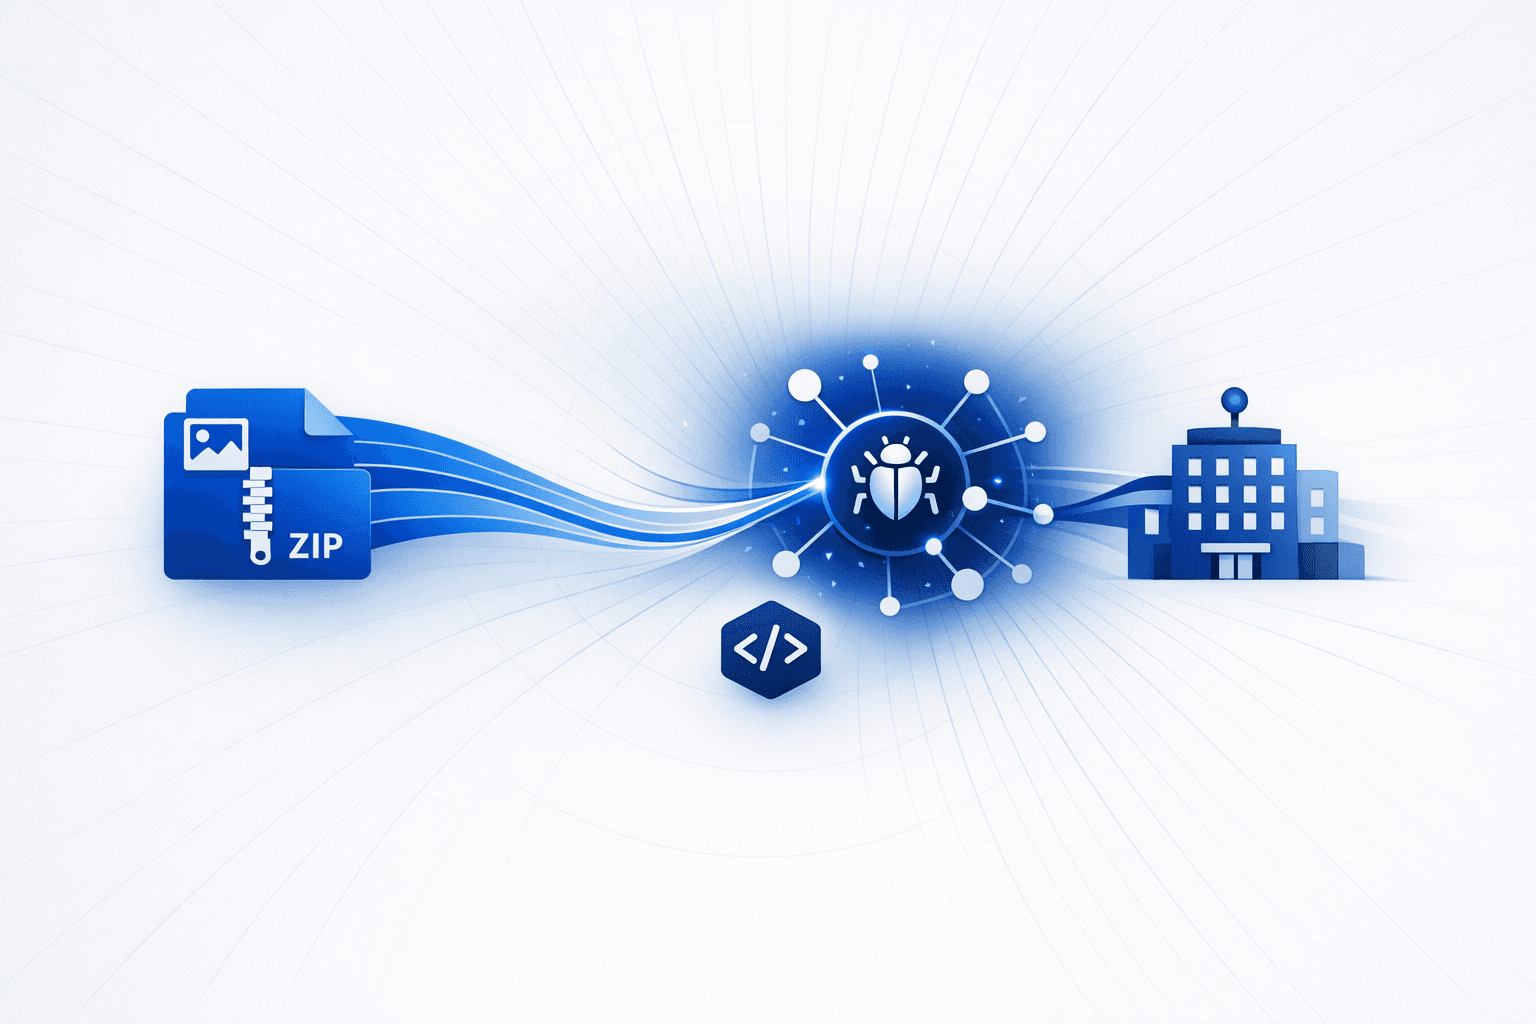
Photo ZIP Phishing Campaign Hits Hotels With TonRAT Node.js Implant

Microsoft reported an active phishing campaign targeting hotel and hospitality organizations across Europe and Asia, using booking-, complaint-, and photo-themed emails to pressure recipients into opening malicious ZIP archives. The messages were routed through trusted services including Calendly and Google redirects, and in later activity used Cloudflare-fronted .cfd domains to evade detection. The ZIP files contained fake PNG shortcut (.LNK) files that launched obfuscated PowerShell, then installed a Node.js-based implant Microsoft tracks as TonRAT; Microsoft said the campaign has been active since April and evolved across multiple waves while keeping the same core infrastructure and tradecraft.

On compromised systems, the attackers established persistence through HKCU\Run and HKCU\RunOnce, added Microsoft Defender process exclusions, and staged payloads in Temp and ProgramData, with some later samples dynamically compiling .NET DLLs via csc.exe and cvtres.exe. TonRAT communicated over encrypted WebSockets and used the TON blockchain API for command-and-control domain resolution, while Microsoft also observed beaconing on non-standard ports such as 56001 and 56002, browser automation, geolocation lookups through ip-api.com, and forced shutdown commands. Microsoft has not attributed the activity to a known threat actor or confirmed follow-on ransomware or data theft, but said the operator is investing in obfuscation, persistence, and delivery evasion to maintain access for later actions.

Is your org in this campaign?Get the infrastructure and lures behind it.
Hunt this campaign
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

5 events · May 2026 – Jun 29, 2026
  1. Jun 29, 20265mo ago

    Trend Micro details TONResolver campaign targeting Japan hotels

    On June 29, 2026, Trend Micro published analysis of a phishing campaign targeting Japanese accommodation facilities that are Booking.com partners in May and June 2026. The report described the TONResolver RAT, including its use of the TON blockchain via TonAPI to resolve rotating C2 infrastructure and its likely follow-on credential theft activity.

    TONResolver RAT Abuses TON Blockchain to Target Japan's Hotel Industry | Trend Micro (US)
  2. Jun 25, 20265mo ago

    Microsoft publishes analysis of TonRAT hospitality campaign

    On June 25, 2026, Microsoft Threat Intelligence published technical details on the Photo ZIP campaign, including its delivery chain, persistence mechanisms, and post-compromise behavior. Microsoft said it had not attributed the activity to a known threat actor.

    Photo ZIP campaign targeting hospitality industry delivers Node.js implant for persistent access | Microsoft Security Blog
  3. Jun 25, 20265mo ago

    Campaign evolves from Wave 1 to Wave 2 with updated delivery tactics

    Microsoft observed the intrusion set evolve from Wave 1 to Wave 2 while retaining core infrastructure and behaviors. Changes included PHOTO-prefixed LNK filenames, dynamic .NET DLL compilation via csc.exe and cvtres.exe, and phishing domains fronted by Cloudflare using .cfd domains.

    Photo ZIP campaign targeting hospitality industry delivers Node.js implant for persistent access | Microsoft Security Blog
  4. Jun 25, 20265mo ago

    Photo ZIP phishing campaign begins targeting hospitality organizations

    Microsoft said an active multi-stage intrusion campaign has targeted hotel and hospitality organizations in Europe and Asia since April 2026. The campaign used phishing emails routed through Calendly and Google redirects to deliver photo-themed ZIP archives containing malicious LNK files that launched PowerShell and installed the Node.js-based TonRAT implant.

    Photo ZIP campaign targeting hospitality industry delivers Node.js implant for persistent access | Microsoft Security Blog
  5. May 2026

    Trend Micro says TONResolver campaign also targeted hotels in 12 other countries

    TrendAI Research said the phishing campaign against Booking.com partner accommodations primarily targeted Japan but also hit hospitality organizations in Austria, Australia, France, Germany, Indonesia, Italy, the Netherlands, Russia, South Korea, Turkey, the UK, and the US. This expanded the known victim scope of the TONResolver campaign beyond Japanese hotels.

    Hackers Leverage Blockchain to Hit Japan's Hotels Through Booking.com - Infosecurity Magazine
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

2 linked

Organizations

1 linked
Booking.com partner hotels

Observables

237 linked

Indicator values are masked on this page. View all 237 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
Hunt This Campaign
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.