SmartApeSG Used Fake Browser Updates to Deploy NetSupport RAT
Malware Intelligence · 2 sources · Updated 3mo ago · First seen Aug 14, 2026
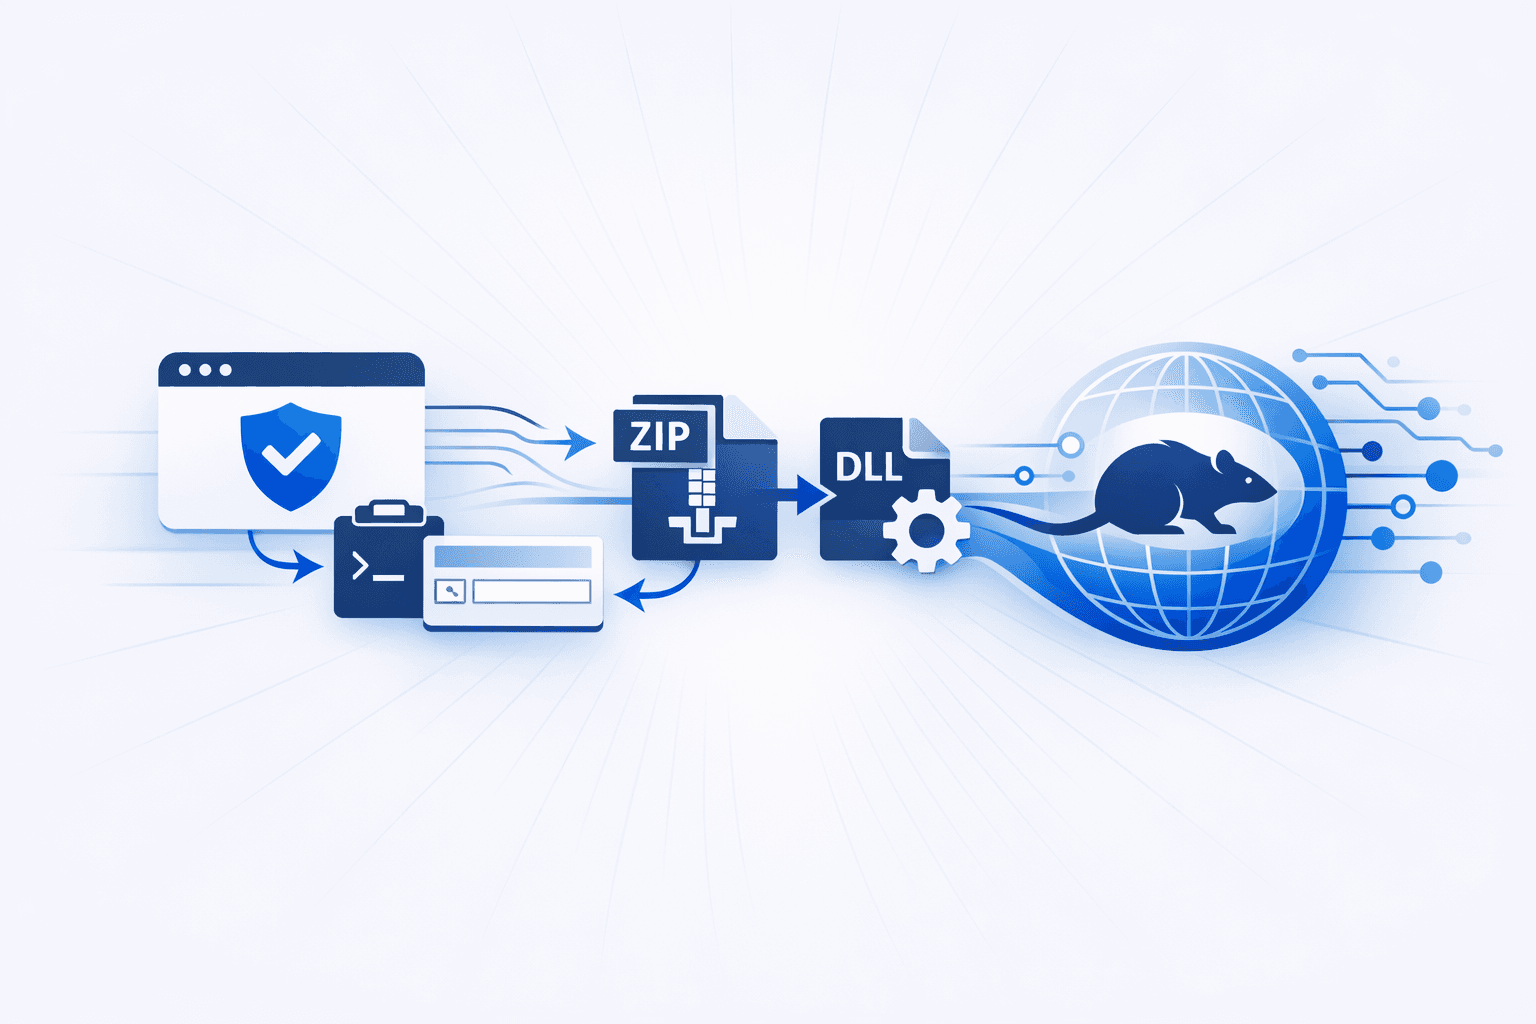
Security researchers linked SmartApeSG to an intrusion chain that used a compromised website to serve a fake browser update ZIP, leading victims to execute a malicious JavaScript file. The script retrieved additional payloads from attacker-controlled URLs, including Base64-encoded content that was decoded into a ZIP archive containing NetSupport RAT components, after which client32.exe was launched on the victim system.
The activity was detected during a January 2024 incident when eSentire's BlueSteel PowerShell classifier flagged malicious PowerShell execution. Investigators said the malware established persistence through the Windows Run registry key, confirming a full remote-access trojan deployment tied to SmartApeSG. eSentire reported that it isolated the affected host, contained the intrusion, and notified the customer.