njRAT Used in Targeted Espionage Campaigns in India and Colombia
Malware Intelligence · 3 sources · Updated 3mo ago · First seen Nov 30, 2021
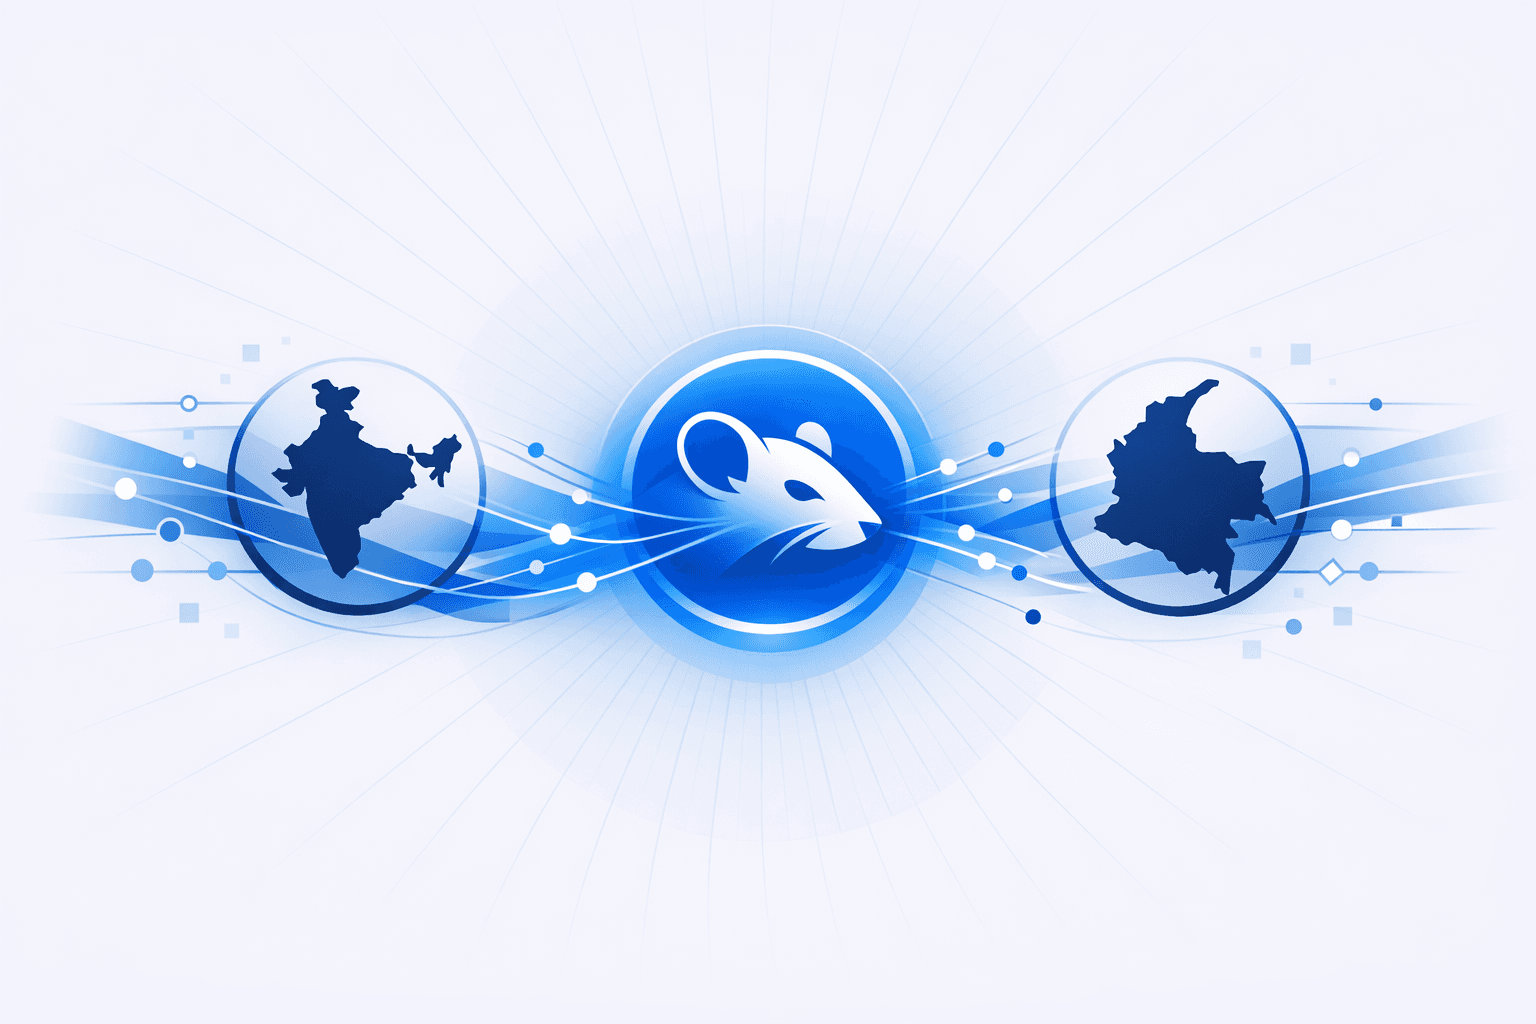
Researchers documented continued use of njRAT (also known as Bladabindi) in targeted intrusion campaigns alongside other commodity and custom remote access trojans. Cisco Talos said the SideCopy APT, which targets government personnel and other entities in India, incorporated njRAT into multi-stage infection chains that often begin with malicious .LNK files and progress through HTAs and loader DLLs before deploying RATs and post-compromise plugins for credential theft, file enumeration, and keylogging. ESET separately reported Operation Spalax, a phishing-driven campaign aimed at Colombian government institutions and private-sector organizations, especially in the energy and metallurgical sectors, where attackers used shortened links, RAR archives, and multiple droppers to install njRAT, Remcos, and AsyncRAT for surveillance and remote control.
A technical analysis of an njRAT 0.6.4 sample tied to the campaign ID splitgateukrayna showed how the malware persists by copying itself to %AppData%\services64.exe, creating a Run registry key, adding a Windows Firewall exception, and using the mutex 49e91d08e684b1770e0cefa60401157a. The sample connected to 44gang44.duckdns[.]org on port 2222, profiled infected systems, and supported a broad set of capabilities including hidden shell execution, keylogging, screenshot capture, registry manipulation, plugin loading, payload download-and-execute, self-update, and uninstall. Across the reported campaigns, njRAT remained a flexible, low-cost espionage tool used to establish persistence, collect victim data, and enable long-term remote access.