
Loading story…
Researchers assessing an espionage campaign targeting East Asian companies since May 2023 said the activity likely focused on semiconductor and rare-metal sectors and used the Xiangoop Loader to deliver fileless payloads including Cobalt Strike Beacon, EntryShell, and in some cases CrowDoor through SparrowDoor Loader. Malware analysis found strong overlap between EntryShell and the older KeyBoy family, including matching embedded and encrypted strings, leading investigators to assess EntryShell as an updated KeyBoy variant.
The same research identified technical overlap between CrowDoor and SparrowDoor, including identical loader shellcode and shared structural and command features, strengthening the case that Tropic Trooper and FamousSparrow are either the same threat actor or closely aligned operators. Earlier reporting on FamousSparrow described a cyberespionage group active since at least 2019 that exploited internet-facing applications such as Microsoft Exchange via ProxyLogon, Microsoft SharePoint, and Oracle Opera to deploy SparrowDoor, a backdoor capable of persistence, host reconnaissance, file theft, process creation, shellcode injection, and interactive remote shell access.
TTPs, infrastructure, and targeting history in one profile.
7 events from the most recent confirmed update back to the earliest known activity.
ITOCHU researchers observed attacks they estimate are linked to Tropic Trooper targeting East Asian companies from May 2023, with suspected focus on semiconductor and rare-metal sectors.
ESET telemetry indicated FamousSparrow began exploiting Microsoft Exchange ProxyLogon vulnerabilities on March 3, 2021, shortly after patches were released.
ESET assessed the cyberespionage group it named FamousSparrow had been active since at least 2019, with targeting that included hotels, governments, international organizations, engineering companies, and law firms.
The ITOCHU analysis describes Tropic Trooper as a cyber-espionage group that has been active since 2011.
Based on malware and loader similarities, ITOCHU assessed that Tropic Trooper and FamousSparrow are either the same group or have a very close operational relationship.
In their 2023 analysis, ITOCHU researchers documented the Xiangoop Loader campaign and found technical overlap showing EntryShell as an upgraded KeyBoy variant and CrowDoor as closely related to SparrowDoor.
ESET reported a newly identified cyberespionage group it named FamousSparrow and documented its custom SparrowDoor backdoor, along with its use of vulnerable internet-facing applications for initial compromise.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 28 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
See this adversary's TTPs, infrastructure, and targeting history, correlated against your exposure.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Kaspersky reported that the Chinese-speaking APT group **Tropic Trooper**—also tracked as **KeyBoy** and **Pirate Panda**—ran a persistent cyber-espionage operation against a Middle Eastern government entity after compromising a public **Umbraco CMS** server. The intrusion began in June 2023 and continued into 2024, with the attackers deploying a new **.NET-based China Chopper** web shell variant to gain foothold and support follow-on activity on the exposed system. Investigators said the operators then used post-exploitation tooling and **DLL search-order hijacking** loaders to deliver **Crowdoor** malware and maintain persistence, adapting their approach after security controls blocked an initial loader by introducing previously unreported `VERSION.dll`-based variants. Kaspersky linked the campaign to Tropic Trooper with high confidence based on code overlap, shared **RC4** keys, tooling, and similarities to earlier operations, while noting some tradecraft overlap with **FamousSparrow**; the case also marks an apparent expansion of Tropic Trooper targeting beyond Taiwan, the Philippines, and Hong Kong to a Middle Eastern system publishing human-rights studies related to the Israel-Hamas conflict.
Jun 29, 2026
Researchers tied multiple government-focused espionage campaigns to a shared malware development and logistics ecosystem built around **CMSTAR** and related tooling. FireEye’s analysis of 11 APT campaigns found common malware families, overlapping command-and-control infrastructure, reused code-signing certificates, clustered compile times, and distinctive NSIS manifest artifacts, leading to its assessment that a centralized **“Sunshop Digital Quartermaster”** supplied malware and operational support to otherwise separate intrusion groups. The report linked 110 malware binaries and 54 domains across campaigns that used families such as `Trojan.APT.9002`, **PoisonIvy**, and **Gh0st**, and described a Chinese-language **9002 Builder** that further suggested centralized tooling rather than fully independent operators. Palo Alto Networks later documented how that model appeared in real-world government targeting. In Mongolia, spear-phishing attacks used politically themed Word documents exploiting `CVE-2012-0158` and later `CVE-2014-1761` to deploy the **Cmstar** loader and **BBSRAT**, with some lures sent from compromised or likely compromised government-associated email accounts and one sample aimed at nearly 2,000 recipients. A separate campaign against Belarusian government entities used Zapad-2017-themed phishing emails, malicious RTF and macro-enabled Word files exploiting `CVE-2015-1641`, and a disguised SCR file to deliver updated **CMSTAR** variants alongside newly identified backdoors **PYLOT** and **BYEBY**. Across both cases, researchers highlighted shared infrastructure, malware lineage, and tooling overlaps that support the view that multiple espionage operators were drawing from a common malware supply chain.
Aug 15, 2026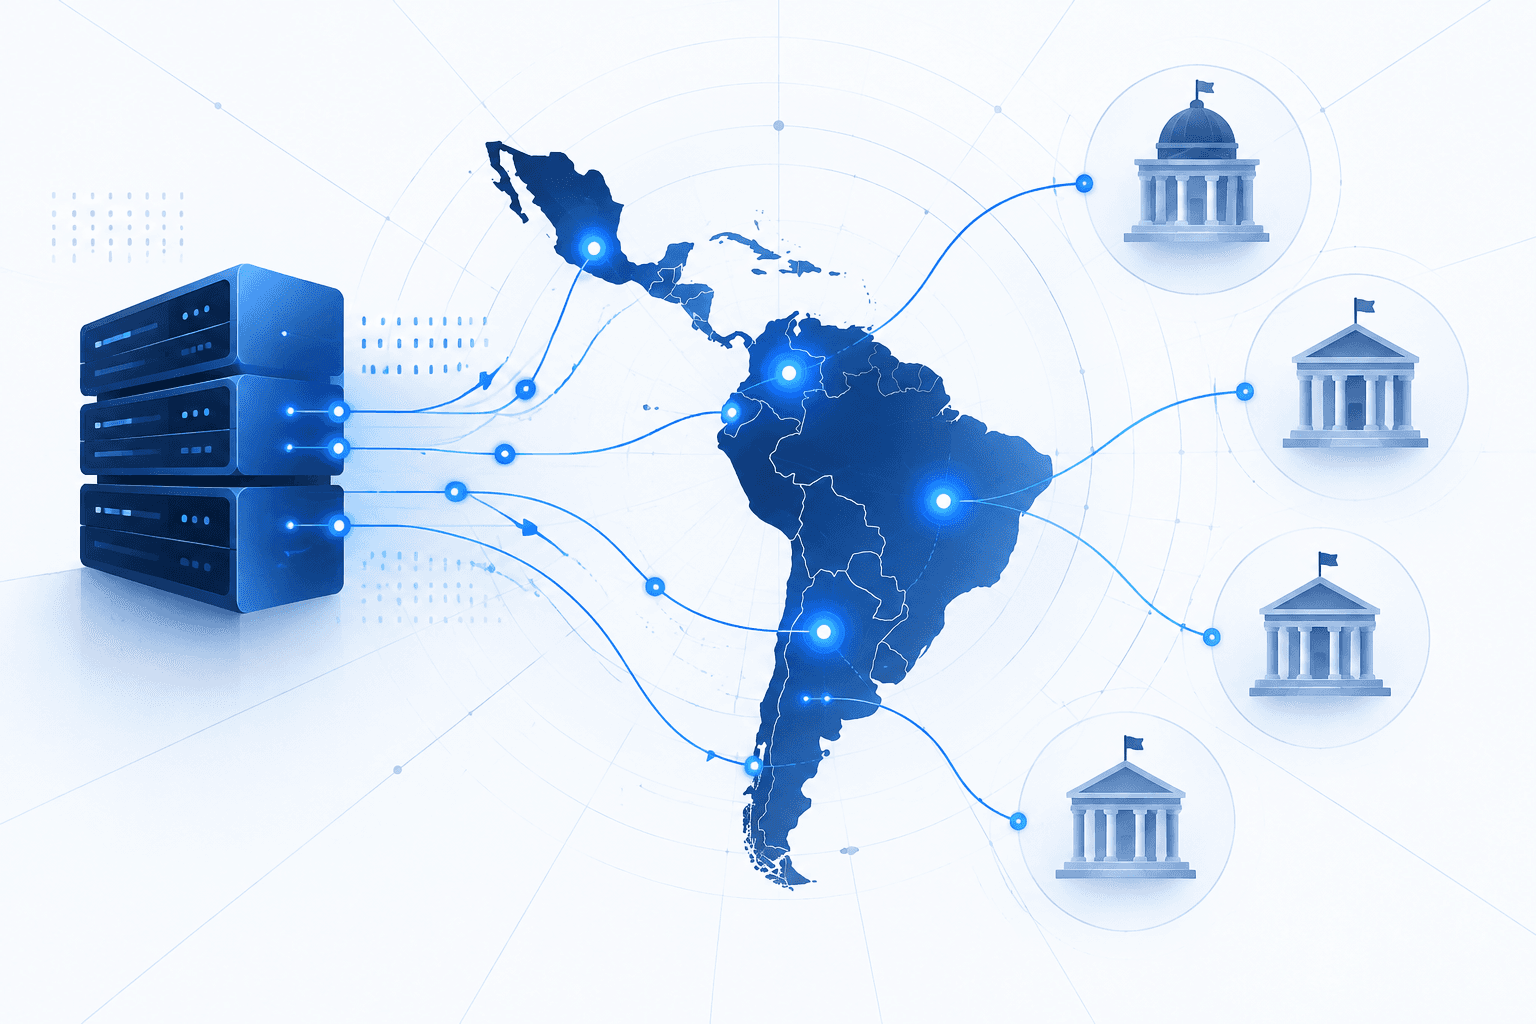
China-aligned cyberespionage group **FamousSparrow** has deployed a new modular C++ backdoor, **SparroWocky**, against government entities across Latin America since at least August 2025. The implant appears to replace the group’s earlier SparrowDoor malware and has disproportionately affected organizations in Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela; roughly 90% of observed targeting since mid-2025 has been in the region. The campaign is assessed as intelligence collection, potentially focused on government responses to U.S. pressure affecting Chinese economic interests. SparroWocky supports host reconnaissance, remote command execution, file collection and manipulation, screenshot capture, proxying, persistence, cross-session process creation, and encrypted exfiltration. Operators deliver it through DLL side-loading: an RC4-encrypted payload stored in a `.dat` file is loaded directly into memory. The malware incorporates open-source offensive tooling and native Beacon Object File execution, while using runtime patching, dynamic API resolution, stack and threat-origin spoofing, and `CreateThread` hooking to disguise malicious threads as legitimate `AnimateWindow` activity.
Sep 17, 2026