Mallory
← Back to News
state-sponsored-espionagegovernment-diplomatic-threatremote-access-implantdefense-evasion-method

FamousSparrow Deploys SparroWocky Backdoor Against Latin American Governments

Threat Actor Intelligence · 15 sources · Updated 2mo ago · First seen Sep 17, 2026
FamousSparrow Deploys SparroWocky Backdoor Against Latin American Governments

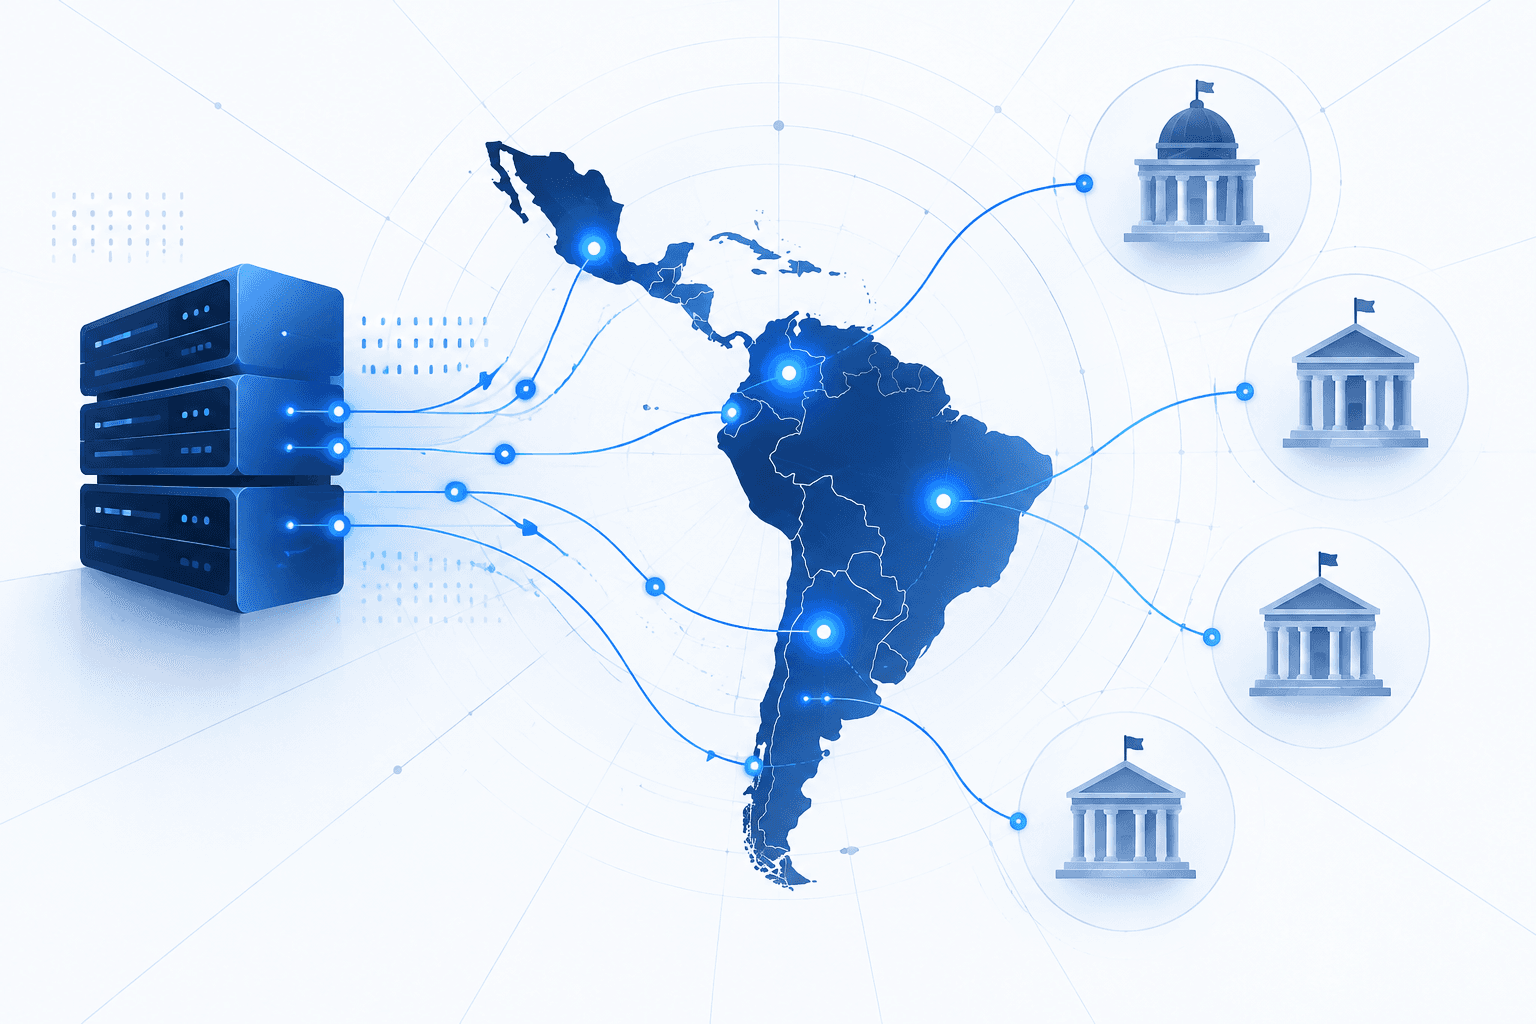
China-aligned cyberespionage group FamousSparrow has deployed a new modular C++ backdoor, SparroWocky, against government entities across Latin America since at least August 2025. The implant appears to replace the group’s earlier SparrowDoor malware and has disproportionately affected organizations in Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela; roughly 90% of observed targeting since mid-2025 has been in the region. The campaign is assessed as intelligence collection, potentially focused on government responses to U.S. pressure affecting Chinese economic interests.

SparroWocky supports host reconnaissance, remote command execution, file collection and manipulation, screenshot capture, proxying, persistence, cross-session process creation, and encrypted exfiltration. Operators deliver it through DLL side-loading: an RC4-encrypted payload stored in a .dat file is loaded directly into memory. The malware incorporates open-source offensive tooling and native Beacon Object File execution, while using runtime patching, dynamic API resolution, stack and threat-origin spoofing, and CreateThread hooking to disguise malicious threads as legitimate AnimateWindow activity.
Know this adversaryTTPs, infrastructure, and targeting history in one profile.
Get the profile
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

8 events · 2019 – Sep 17, 2026
  1. Reported Sep 17, 20262mo ago

    FamousSparrow uses public-facing Exchange servers to deploy SparroWocky

    Researchers reported that FamousSparrow compromised public-facing Microsoft Exchange servers to gain access and deploy the SparroWocky backdoor against government targets in Latin America. The report also provided loader and backdoor hashes and command-and-control IP indicators.

    FamousSparrow Exploits Public-Facing Exchange Servers to Deploy SparroWocky Backdoor
  2. Reported Sep 17, 20262mo ago

    ESET links FamousSparrow to Earth Estries and Salt Typhoon

    ESET assessed that FamousSparrow shares some level of operational overlap with the Earth Estries and Salt Typhoon threat clusters. The degree and nature of that overlap were not specified.

    China-Aligned FamousSparrow Deploys SparroWocky Backdoor Across Latin America
  3. Reported Sep 17, 20262mo ago

    SparroWocky identified as FamousSparrow's replacement for SparrowDoor

    SparroWocky was identified as a distinct malware family that appears to have superseded FamousSparrow's SparrowDoor implant. Attribution was supported by overlapping infrastructure and victimology, including SparroWocky deployments by SparrowDoor on previously compromised networks.

    New SparroWocky Backdoor Targets Latin America - Decipher
  4. Sep 17, 20262mo ago

    ESET publishes SparroWocky IoCs and payload extraction utility

    ESET added SparroWocky indicators to its malware-IoC repository, including five loader and in-memory backdoor samples and 18 command-and-control IP addresses observed from December 2025 through June 2026. The update also provided a Python utility that RC4-decrypts payloads and reconstructs stripped PE headers for analysis.

    Added IoCs for sparrowocky
  5. Reported Sep 17, 20262mo ago

    Technical capabilities and evasion methods of SparroWocky disclosed

    Analysis disclosed that SparroWocky supports reconnaissance, command execution, file exfiltration, screenshots, TCP proxying, reverse port forwarding, and in-memory PE and Beacon Object File execution. It is delivered through DLL side-loading and uses RC4, TLS, API hashing, call-stack spoofing, thread-start concealment, and forged Windows loader structures to evade detection.

    Beware the SparroWock: The backdoor that bites, the commands that catch
  6. Aug 2025

    FamousSparrow deploys SparroWocky against Latin American governments

    FamousSparrow deployed the new modular C++ SparroWocky backdoor in a cyberespionage campaign targeting government entities in Latin America. Victims were identified in Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela.

    New SparroWocky Backdoor Targets Latin America - Decipher
  7. 2025

    FamousSparrow activity shifts primarily to Latin America

    Telemetry indicated that FamousSparrow activity became primarily focused on Latin American targets from mid-2025, with government institutions heavily targeted.

    New SparroWocky Backdoor Targets Latin America - Decipher
  8. 2019

    FamousSparrow begins operating as an espionage group

    FamousSparrow, a China-aligned cyberespionage group, is believed to have operated since at least 2019.

    New SparroWocky Backdoor Targets Latin America - Decipher
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Organizations

8 linked
Government of VenezuelaGovernment of PanamaGovernment of Puerto RicoGovernment of GuatemalaGovernment of EcuadorGovernment of PeruGovernment of ArgentinaGovernment of Honduras

Observables

61 linked

Indicator values are masked on this page. View all 61 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?See this adversary's TTPs, infrastructure, and targeting history, correlated against your exposure.
Get the Full Actor Profile
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.