
Loading story…
A threat actor assessed as Kimsuky distributed malicious Windows shortcut (.LNK) files to South Korean targets, posing as a request to review a seafood-ingredient purchase document. Opening the shortcut displays a legitimate-looking HWP decoy while covertly launching PowerShell and obfuscated JavaScript payloads. The malware creates persistence through scheduled tasks, reportedly using names matching MicrosoftOffice2016_<UUID-prefix>, and removes or hides intermediate files and temporary CMD artifacts to hinder investigation.
The PowerShell payload inventories host and user information, including system and process details, then exfiltrates it to a Backblaze B2 cloud-storage-based command-and-control infrastructure. It also retrieves victim-specific follow-on commands from that service and executes them in a hidden window. AhnLab linked the activity to prior Kimsuky operations based on overlapping PowerShell syntax, LNK data-extraction behavior, file-size-based LNK identification, and scheduled-task registration patterns; defenders should hunt for the named task pattern, suspicious ProgramData artifacts, Backblaze B2 traffic, and connections to api.ipify.org.
TTPs, infrastructure, and targeting history in one profile.
1 event from the most recent confirmed update back to the earliest known activity.
AhnLab identified distribution of a malicious LNK file masquerading as a seafood-ingredient purchase-review request to users in South Korea. The LNK displayed an HWP decoy while deploying PowerShell and JavaScript payloads, establishing scheduled-task persistence, exfiltrating host information through Backblaze B2, and retrieving follow-on commands; AhnLab linked the activity to Kimsuky based on similarities with prior campaigns.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
See this adversary's TTPs, infrastructure, and targeting history, correlated against your exposure.
5 references tracked. Mallory keeps watching after this page renders.
infosec.pub
Open sourcemalware.news
Open sourcebsky.app
Open sourceasec.ahnlab.com
Open sourceasec.ahnlab.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
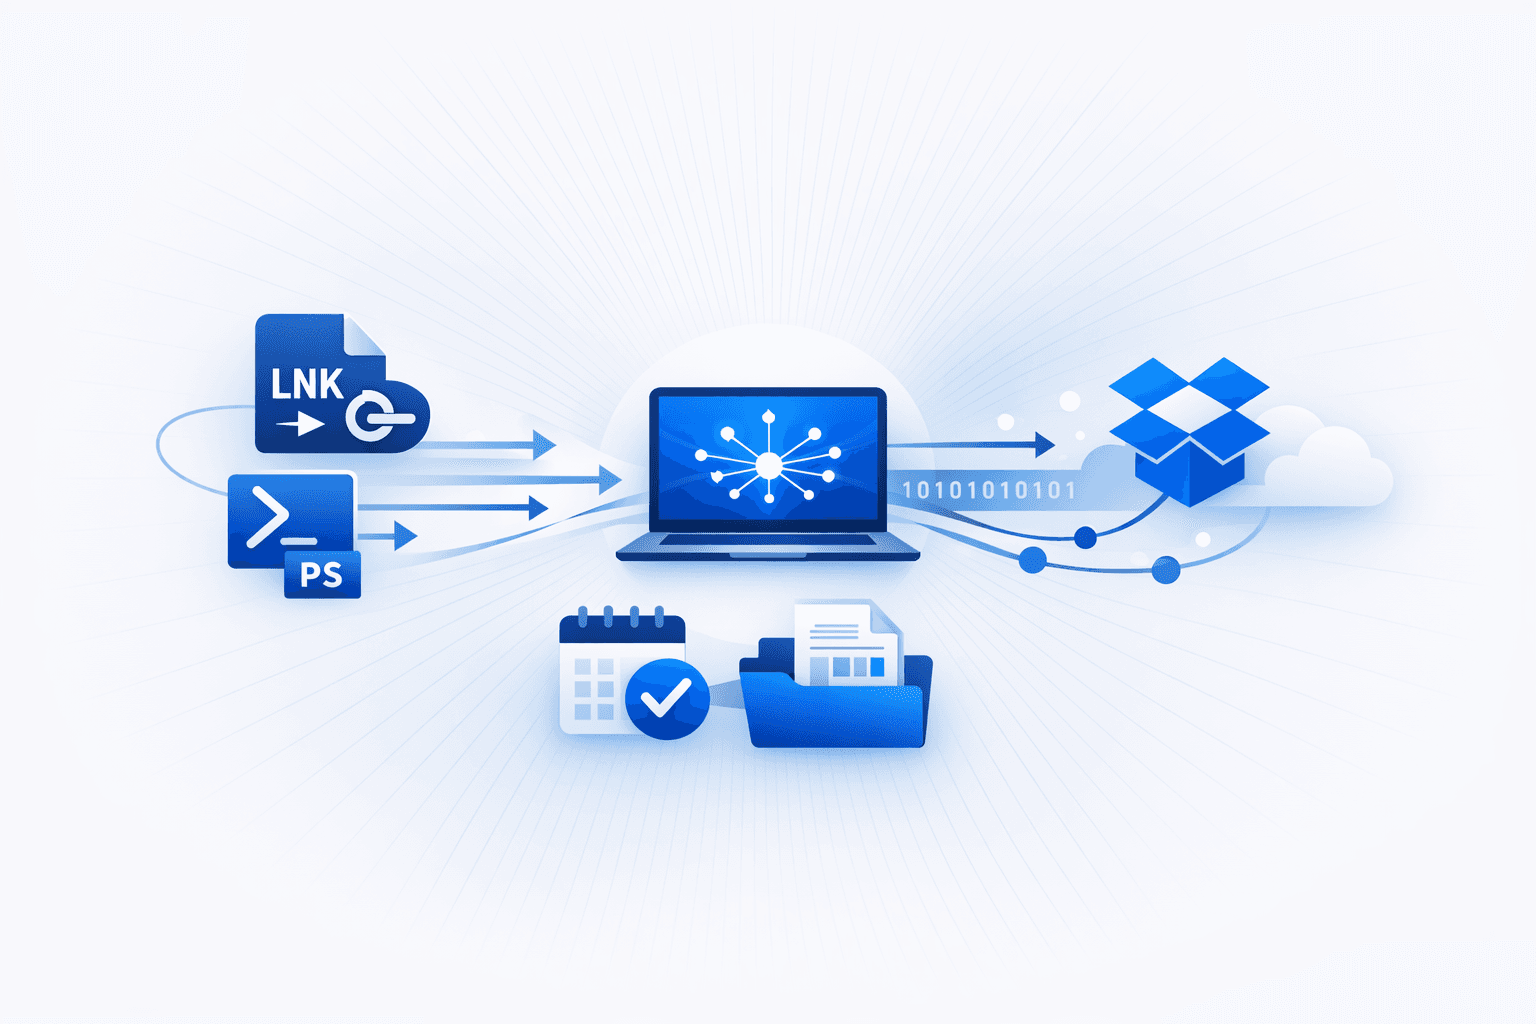
**Kimsuky**-linked malware delivered through malicious **LNK** files was observed targeting likely South Korean users, using shortcut execution to unpack a PowerShell-based implant, establish persistence via **Task Scheduler**, collect host information, and communicate through the **Dropbox API**. IIJ reported that the LNK extracts files into `C:\PerfLog`, deploys `www.ps1` and a VBScript launcher, creates a scheduled task named `P`, and drops a decoy document in a Hancom Office format. The malware generates a client ID from the victim MAC address, gathers system details including domain, username, OS version, process lists, and external IP address, then uploads the data to attacker-controlled Dropbox folders before attempting to download and run a follow-on batch payload. AhnLab's February 2026 APT trend reporting for South Korea provides broader context showing that **spear phishing** remained the dominant delivery method and that **LNK-based attacks** were the most prevalent format observed, including campaigns that used PowerShell to fetch additional components and register persistence. While AhnLab's report is a monthly trend overview rather than a dedicated write-up on the Dropbox variant, it aligns with IIJ's assessment that the malware shares substantial **TTP** overlap with previously reported **Kimsuky** activity. The reporting indicates continued abuse of legitimate cloud services such as **Dropbox** and, more broadly, GitHub and similar platforms to blend command-and-control and payload staging into normal network traffic.
Jun 30, 2026
North Korea-linked **Kimsuky** has been tied to a series of phishing campaigns that delivered malware through files disguised as PDFs, resumes, questionnaires, and North Korea-related consultation documents. Across the observed intrusions, victims were lured into opening password-protected archives, enabling Office macros, or executing VBS and CHM files, after which the malware launched follow-on payloads through tools such as `wscript.exe`, `mshta.exe`, `regsvr32.exe`, and PowerShell. The implants opened decoy documents to reduce suspicion, established persistence with scheduled tasks, Startup-folder copies, or `HKCU\Run` entries, and contacted attacker-controlled infrastructure including `kro.kr`, `webcindario`, and PHP-based command-and-control endpoints. The recovered payloads show Kimsuky broadening from simple downloaders into multi-stage surveillance and theft malware. Reported capabilities include host reconnaissance, browser and email data theft, crypto-wallet artifact collection, file upload and download, keylogging, clipboard capture, active-window monitoring, and registry changes that weaken Microsoft Office security settings. Researchers also linked newer operations to a wider infrastructure ecosystem, including SharpExt-related panels and a compromised site used to deliver browser-extension malware, while one later campaign exfiltrated stolen victim data through the **GitHub API** instead of FTP, indicating continued adaptation in both delivery and collection methods.
Aug 15, 2026
Attackers distributed malicious Windows shortcut (`.LNK`) files disguised as privacy consent forms and other work-related documents, tricking users into launching obfuscated PowerShell that fetched additional payloads from external infrastructure. Reporting indicates GitHub was used as a covert stage in the infection chain, helping operators blend malicious downloads and command retrieval into legitimate web traffic while keeping much of the activity fileless and in memory. Once executed, the malware created downloader and loader scripts, established persistence through Windows Task Scheduler, opened decoy documents to reduce suspicion, and deleted the original shortcut to limit forensic artifacts. Observed follow-on payloads included an information stealer and a backdoor loader that decrypted and loaded malware into memory; the theft activity gathered host, security product, network, IP, drive, file, and process data, with behavior resembling prior **Kimsuky**-linked operations.
Jun 29, 2026