APT40-Linked Campaign Used DLL Side-Loading Against Malaysian Officials
Threat Actor Intelligence · 3 sources · Updated 2mo ago · First seen Jun 22, 2022

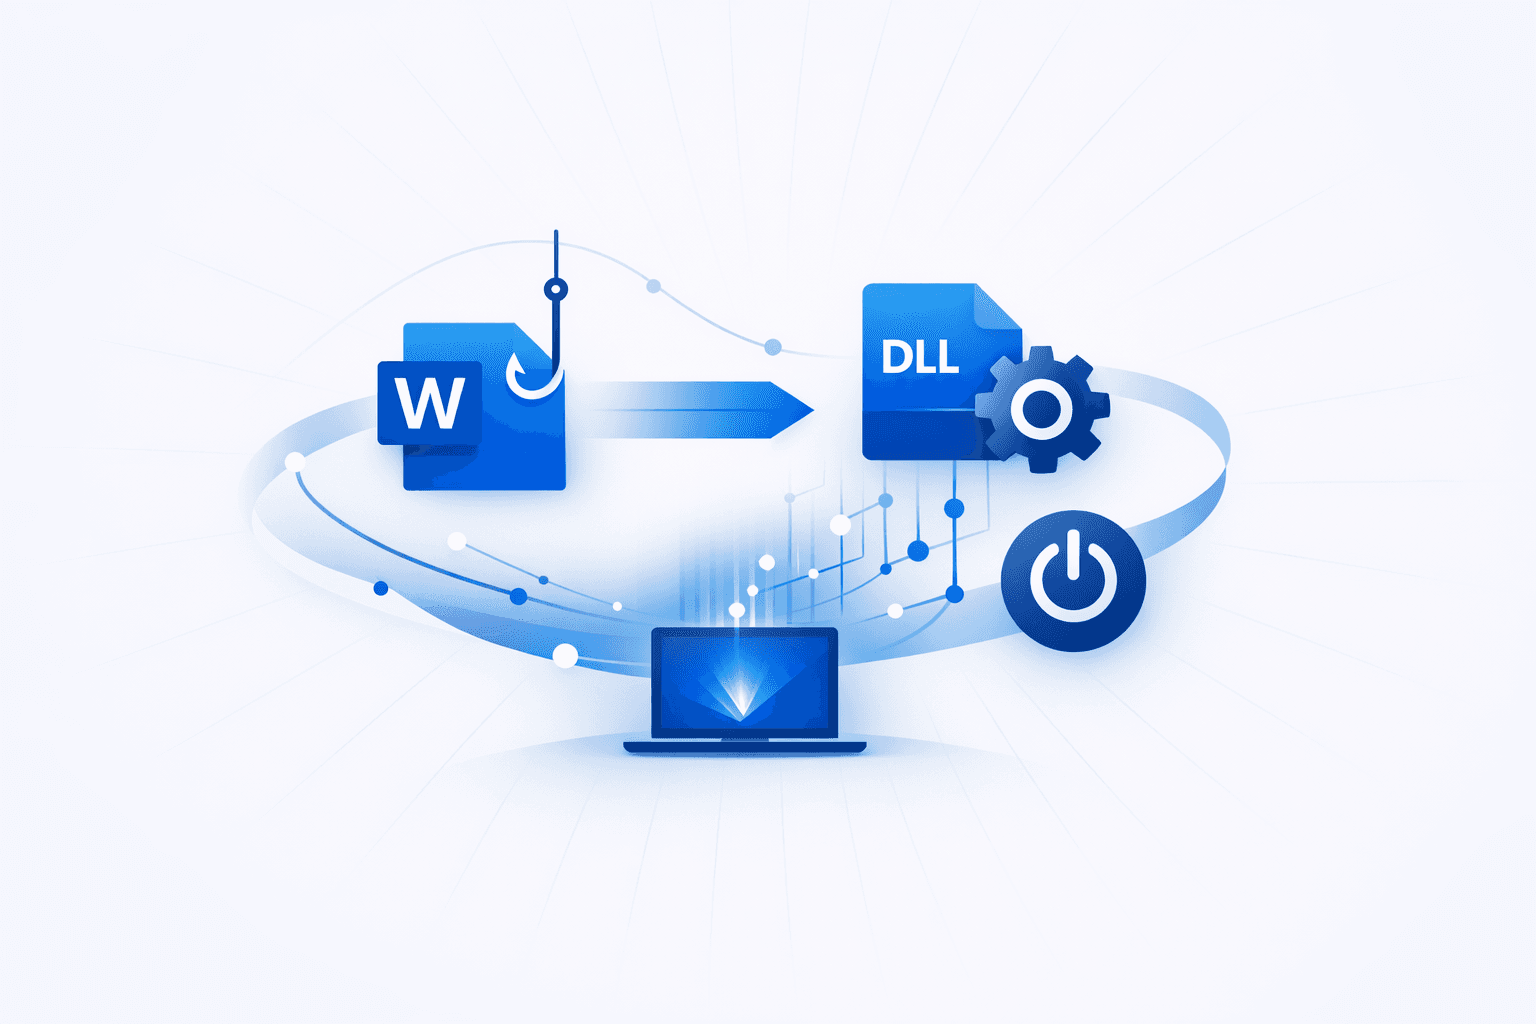
Elastic analyzed a spearphishing operation targeting Malaysian government officials with a malicious Word document themed around Malaysia's 2020 political crisis. The document remotely loaded a VBA template that wrote DLL payloads to disk, downloaded Logitech's legitimate LogiMailApp.exe, and exploited DLL side-loading by placing a malicious LogiMail.dll beside it for execution.
The backdoor retrieved and decrypted a second-stage implant in memory, enabling host reconnaissance, command execution, file transfers, Registry Run-key persistence, and AES-encrypted command-and-control through dynamic-DNS infrastructure. Elastic linked the activity with moderate confidence to the China-nexus APT40/Leviathan group, citing overlaps in strings, URLs, functionality, and tactics with indicators previously published by MyCERT; DLL side-loading is a widely used execution and defense-evasion technique tracked as MITRE ATT&CK T1574.001.