Casbaneiro Banking Trojan Uses Distributed Servers Against Latin American Users
Social Engineering & Fraud · 5 sources · Updated 2mo ago · First seen Sep 11, 2026
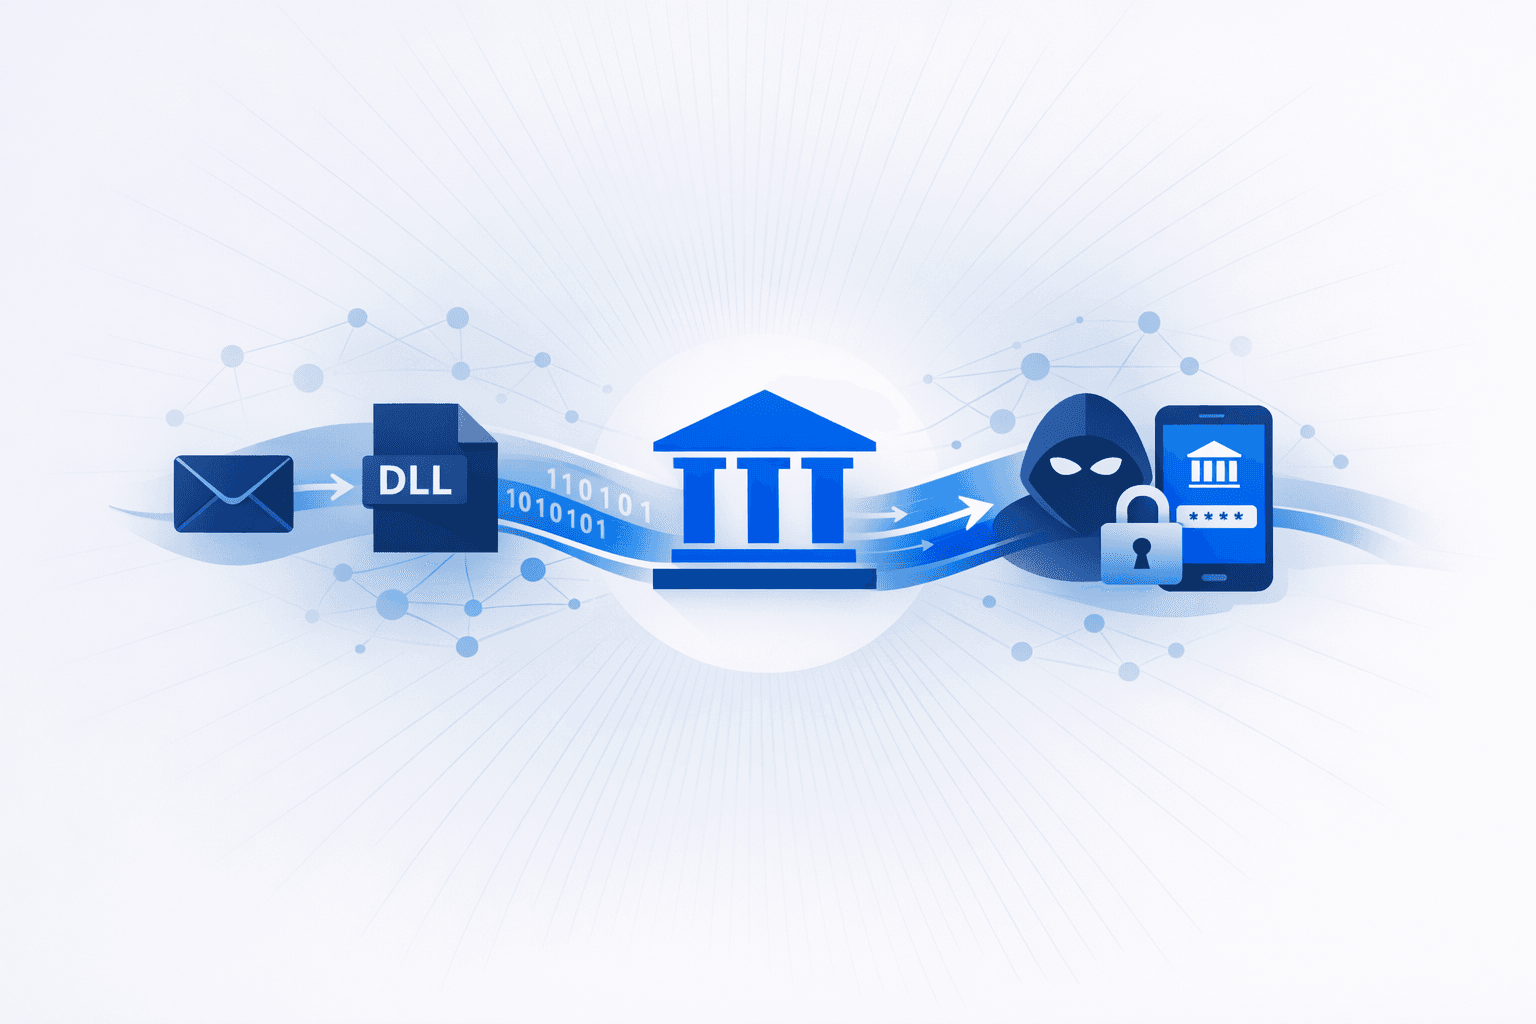
A high-severity Casbaneiro banking-trojan campaign is targeting Microsoft Windows users in Latin America through phishing emails masquerading as invoices and legal notices. The messages deliver a multi-stage infection chain involving an HTA downloader, an AutoIt interpreter and loader, and a final payload injected into legitimate Windows processes such as RegSvcs.exe or mobsync.exe; persistence is established through a Startup-folder LNK file.
The malware activates command-and-control activity after victims visit targeted banking sites and enables financial fraud through clipboard manipulation and fraudulent windows. It also harvests Outlook address-book data and email metadata, sending it unencrypted to multiple attacker-controlled data-receiving servers. Casbaneiro evades analysis through fragmented runtime string decryption and HTTP 403 responses, while avoiding systems configured in German, French, or English; defenders should prioritize blocking the campaign's published malicious domains, IP addresses, and file hashes and investigate suspicious HTA, AutoIt, and Startup-folder activity.