
Loading story…
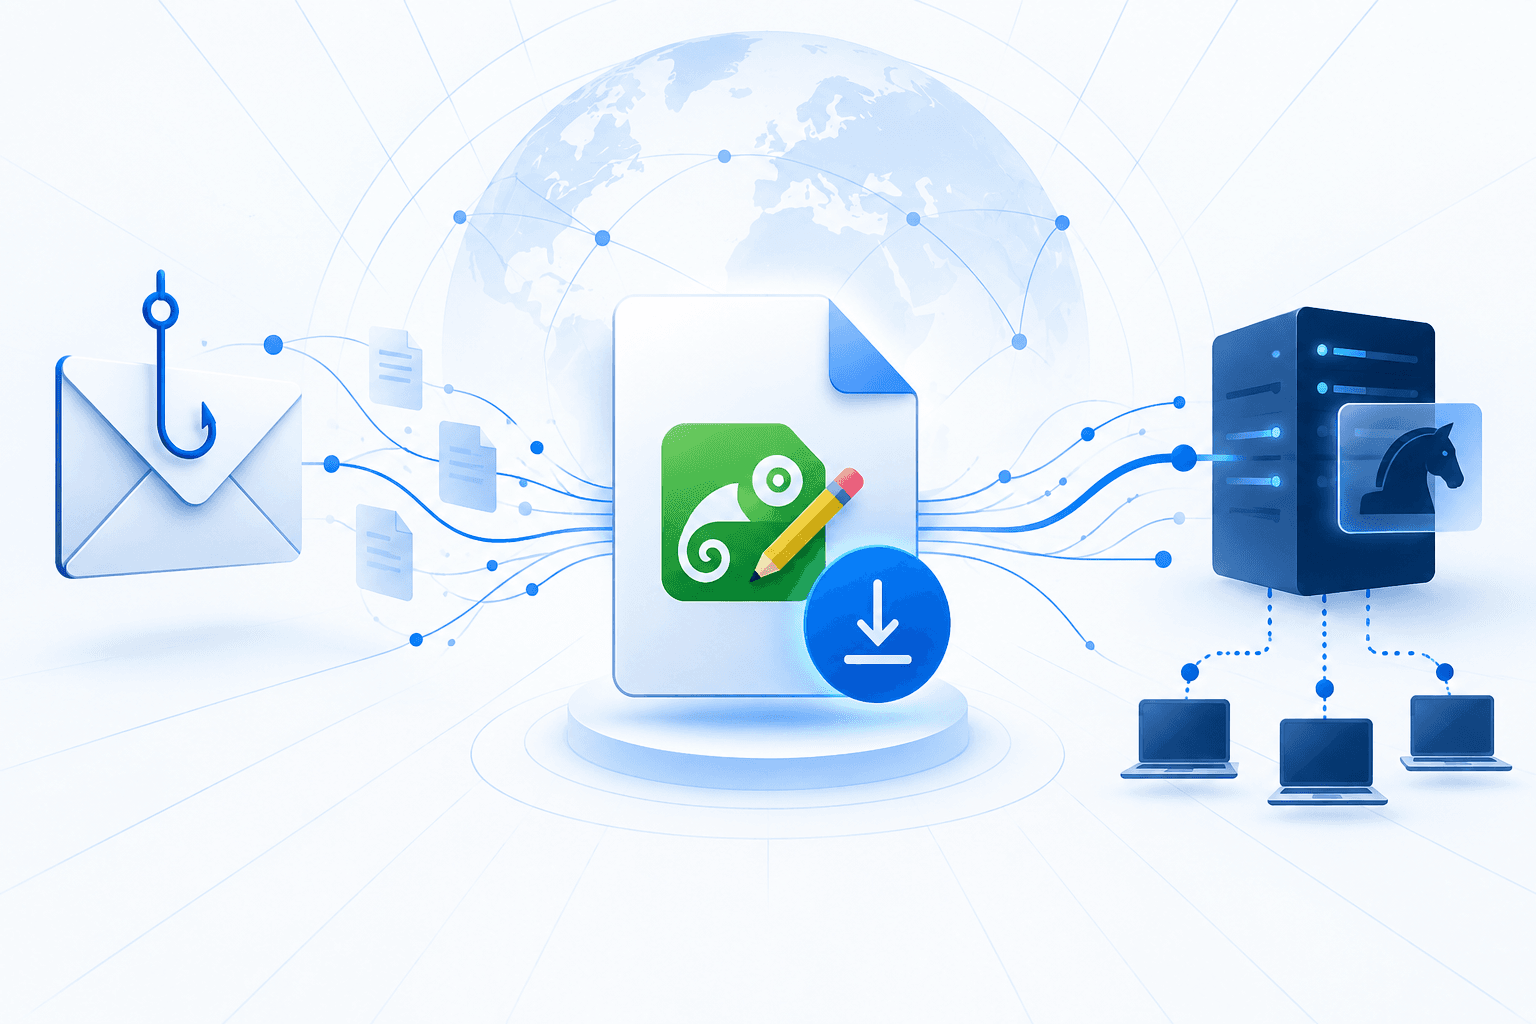
The emerging PAPERMILL cluster is targeting Indian organizations with tax-audit-themed phishing emails carrying an ISO 9660 disk-image attachment disguised as an .img file. Mounting the image helps evade Mark-of-the-Web protections; victims are then induced to launch a renamed, legitimately signed Notepad++ executable posing as a tax notice. That executable DLL-sideloads a malicious libcurl.dll proxy, which decrypts and executes a multistage payload.
The loader employs anti-analysis delays and sandbox checks, may request UAC elevation and create RunOnce persistence, and uses Donut reflective loading to launch VenomRAT 6.0.3 in memory. The configured command-and-control server is 154.36.188.201:4449; VenomRAT enables hidden VNC, data theft, file collection, remote command execution, and follow-on intrusion. Researchers assess the financially motivated activity as likely China-nexus and Silver Fox-adjacent based on its lures, delivery methods, and infrastructure, but have not attributed it conclusively to Silver Fox.
Get the infrastructure and lures behind it.
4 events from the most recent confirmed update back to the earliest known activity.
Multiple sibling disk-image samples, including Tax_Notice_16695.img, ITDENF2026-4281.img, and Tax_436454367.img, were associated with the same VenomRAT builder certificate later linked to PAPERMILL. Additional samples Tax_Notice_23665.img and Tax_Notice_99674.img reportedly contacted the same command-and-control infrastructure.
JUMPSEC documented that the Tax_Notice_45594.img chain used a malicious libcurl.dll loader that attempted UAC elevation, established RunOnce persistence via a masqueraded RuntimeBroker.exe, and delayed execution under sandbox-like conditions. The researchers also disclosed the phishing URL, sender and mail-host infrastructure, and hashes for the ISO, loader, encrypted stage, and VenomRAT payload.
JUMPSEC assessed the activity with high confidence as China-nexus, financially motivated commodity crimeware targeting Indian entities. The researchers found moderate-to-high-confidence similarities to Silver Fox tradecraft but stated that the available evidence did not support confident attribution to Silver Fox.
The PAPERMILL cluster conducted phishing attacks using Indian tax-audit notices and an ISO 9660 disk image masquerading as an IMG attachment. The image used a renamed, legitimately signed Notepad++ executable to sideload a malicious libcurl.dll loader, which decrypted and launched VenomRAT v6.0.3; the analyzed payload was configured to use 154.36.188.201:4449 for command and control.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 47 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
4 references tracked. Mallory keeps watching after this page renders.
cryptika.com
Open sourcejumpsec.com
Open sourcejumpsec.com
Open sourcejumpsec.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.

The Chinese threat actor known as **Silver Fox** has launched a targeted phishing campaign against Indian organizations, using income tax-themed emails to deliver the modular remote access trojan **ValleyRAT**. Attackers impersonate the Indian Income Tax Department, sending emails with decoy PDF attachments that, when opened, direct victims to a malicious website hosting a ZIP archive. This archive contains a disguised installer that leverages DLL hijacking, specifically abusing a legitimate executable (`thunder.exe`) and a malicious DLL (`libexpat.dll`), to establish persistent access and evade detection. The campaign demonstrates a sophisticated multi-stage infection chain, with the initial payload acting as a loader for subsequent malware modules designed to maintain deep access to compromised systems. Researchers from CloudSEK have attributed this campaign to Silver Fox, correcting previous misattributions to other threat groups. The group, also known as SwimSnake and Void Arachne, has expanded its targeting beyond Chinese-speaking entities to include Indian public, financial, medical, and technology sectors. The use of socially engineered tax documents and trusted file formats highlights the attackers' ability to bypass traditional security controls, while the complex kill chain and modular malware architecture underscore the evolving threat posed by Silver Fox to Indian organizations.
Jun 29, 2026
The China-linked threat group **Silver Fox** ran a phishing campaign that impersonated tax authorities in India and Russia to infect organizations with **ValleyRAT** and a newly documented Python backdoor, **ABCDoor**. Researchers said the activity began with fake tax notices sent as PDF attachments that directed victims to download a malicious archive. That archive contained a modified Rust-based loader, **RustSL**, which used geofencing, environment checks, stealth features, and persistence mechanisms before deploying ValleyRAT and then ABCDoor. More than 1,600 malicious emails were observed between early January and early February 2026, with victims spanning the industrial, consulting, retail, and transportation sectors. Analysis tied ABCDoor to Silver Fox’s toolkit since at least late 2024, with confirmed operational use starting in early 2025. On infected Windows systems, the malware established persistence through the **Run** registry key and a scheduled task named **`AppClient`**, concealed files under **`C:\ProgramData\Tailscale`**, and abused **`pythonw.exe`** and **`ffmpeg.exe`** to blend in while enabling surveillance, remote interaction, module execution, command-and-control, and data exfiltration. Researchers also identified a new ValleyRAT plugin that acted as a loader for ABCDoor, showing the group is expanding a malware chain built for covert access and follow-on control.
Jun 29, 2026
Multiple campaigns are using phishing emails and archive-based lures to deliver remote access malware through stealthy, multi-stage infection chains. Point Wild documented **Remcos RAT**, **DesckVB RAT**, and a Rust-based **COVERT RAT** being delivered through ZIP attachments, weaponized `LNK` files, obfuscated JavaScript droppers, and hidden PowerShell execution, often with decoy documents to mask activity. The payloads were loaded filelessly through .NET reflection and in-memory execution, with operators abusing legitimate binaries and services such as `aspnet_compiler.exe`, GitHub, and paste or web-hosting platforms to stage malware while evading detection. Reported command-and-control infrastructure included `192.3.27.141:8087`, `172.245.246.77:8080`, and `181.231.253.69:4444`, while observed artifacts included `C:\ProgramData\remcos\logs.dat`, `C:\ProgramData\colors\logs.dat`, and payload names such as `ALTERNATE.dll`, `ClassLibrary3.dll`, `Keylogger.dll`, and `msedge_proxy.exe`. Separate reporting showed the same tradecraft extending beyond custom RATs to commodity remote-access software and credential theft. A campaign targeting Russian aerospace and aviation organizations used invoice-themed phishing and spoofed domains to install a portable **AnyDesk** instance for unattended access, maintain persistence with a scheduled task, minimize visibility with Tray Minimizer, and exfiltrate configuration data through a command-line SMTP mailer; Seqrite linked the activity to **Rare Werewolf (Librarian Ghouls)**. Securonix research cited by Trojan Killer described **VEIL#DROP** using fake document-style JavaScript files, Blogspot-hosted staging, PowerShell download cradles, XOR decoding, and in-memory .NET loading to deploy **PureLog Stealer**, which targets browser credentials, cookies, session tokens, wallet data, and host information. Across the campaigns, the common pattern is phishing-led initial access followed by LOLBins, PowerShell, staged downloads, persistence, and covert data theft or long-term remote control.
Jul 12, 2026