
Loading story…
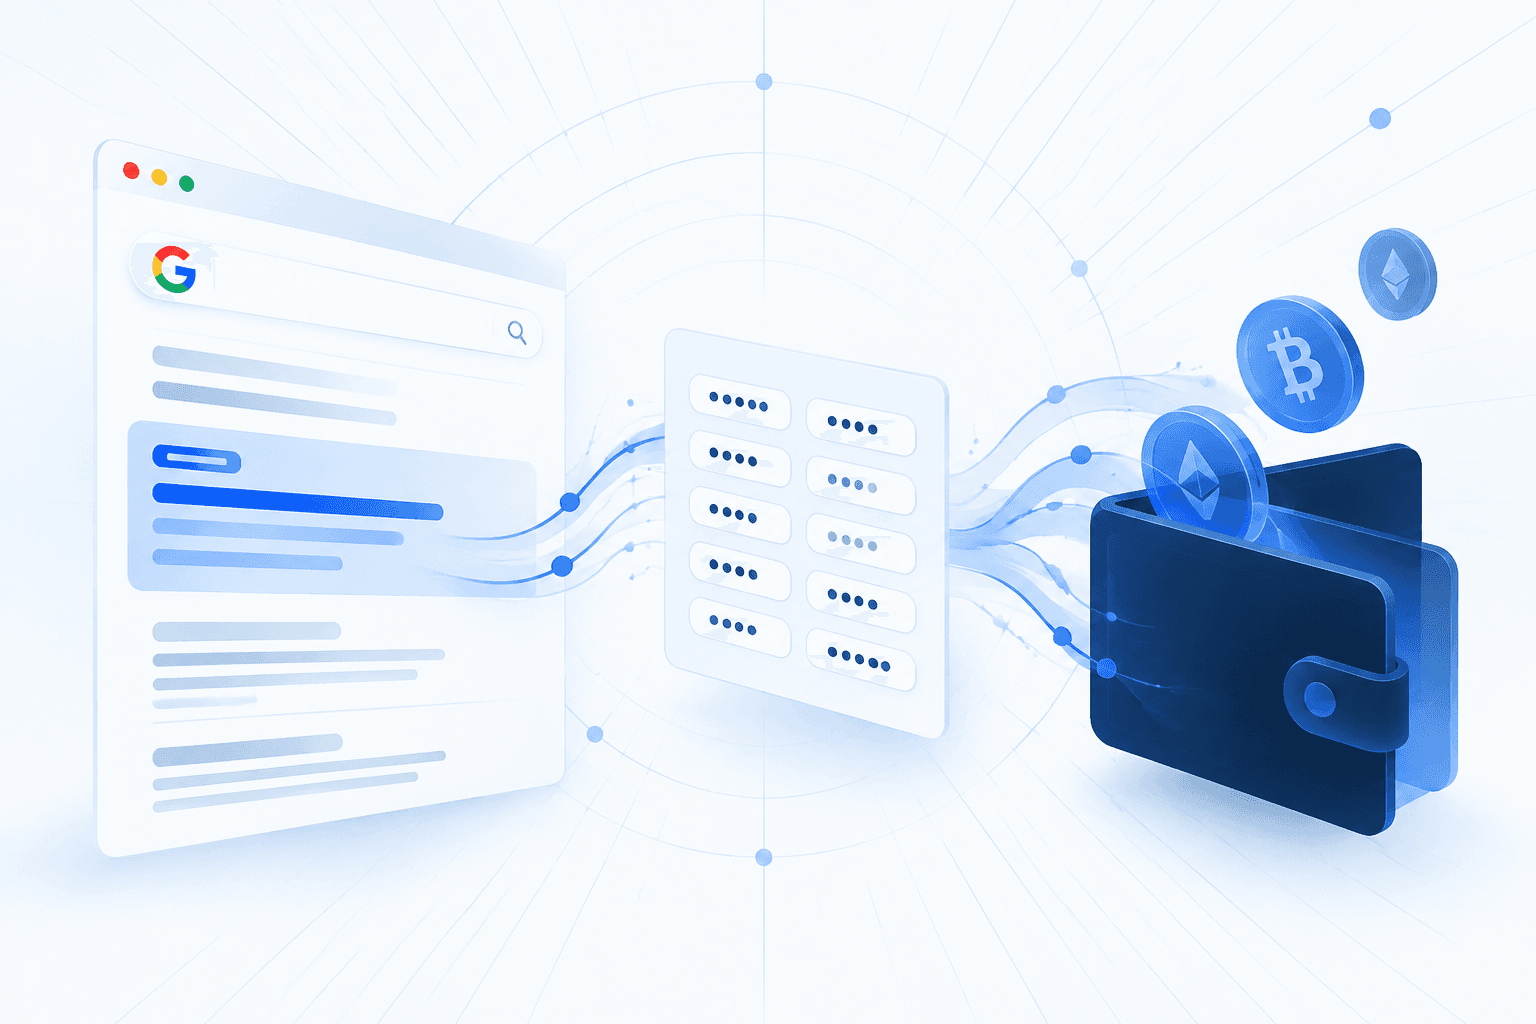
Threat actors used fraudulent, Google-verified sponsored advertisements impersonating Ledger to target hardware-wallet users in the United States, Europe, and parts of Asia. Victims were routed through a multi-stage chain involving Google Cloud Storage, rapidly rotating Vercel redirect domains, and Google Sites pages that embedded a counterfeit Ledger site in an iframe; the Vercel infrastructure rotated approximately every 15–20 minutes to frustrate reputation-based blocking.
The fake site fingerprinted visitors and mimicked Ledger software-download, device-setup, and firmware-verification workflows before requesting the victim's secret recovery phrase. It used the BIP-39 English wordlist to provide phrase autocomplete and collected device and behavioral metadata; submitted phrases were exfiltrated, including to attacker-controlled Vercel endpoints, enabling operators to restore victims' wallets and transfer funds without access to the physical Ledger devices.
Get the infrastructure and lures behind it.
1 event from the most recent confirmed update back to the earliest known activity.
In August 2026, Zscaler ThreatLabz analyzed a campaign that used malicious sponsored Google ads impersonating Ledger to target cryptocurrency users in the United States, Europe, and parts of Asia. The ads routed victims through Google Cloud Storage, rotating Vercel redirects, and Google Sites-hosted iframe content to harvest Ledger secret recovery phrases.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Threat actors used **punycode and other lookalike domains** to impersonate Ledger and target cryptocurrency users after the company's customer data breach became public. Proofpoint reported thousands of phishing emails directing victims to a spoofed Ledger site that offered trojanized `Ledger Live` installers for **Windows, macOS, and Linux**. The altered application removed normal setup options, coerced users into entering wallet recovery phrases, validated the words against the **BIP-39** mnemonic list, and exfiltrated completed seed phrases over HTTP, enabling theft of associated cryptocurrency. A parallel campaign used fake Ledger web pages, likely distributed by SMS, to steal recovery phrases without requiring a download. Separate infrastructure analysis tied Ledger-themed domains to a broader **homograph-domain** operation that also impersonated **Brave, Signal, and Telegram** through internationalized domain names encoded with the `xn--` **Punycode** prefix. Silent Push identified domains such as `xn--brav-yva[.]com`, promoted through Google ads, that delivered ISO files linked to the **RedLine infostealer**, and said the registrations and hosting overlapped with other brand-impersonation activity. Together, the reporting shows attackers combining breach-themed social engineering, IDN spoofing, and malware delivery to compromise cryptocurrency holders and steal credentials or wallet access without attacking Ledger hardware directly.
Aug 15, 2026
Rapid7 uncovered an active cryptocurrency fraud operation, tracked as **Operation ASTERIX**, after finding an exposed attacker server containing phone-number datasets, account-validation tools, phishing panels, Asterisk-based dialing infrastructure, and counterfeit wallet applications impersonating **Trezor**, **Ledger**, and **Exodus**. The campaign validated more than 100,000 phone numbers against cryptocurrency services including **Crypto.com** and **Kraken**, enriched confirmed leads with personal details, and then used coordinated phishing emails and vishing calls to direct victims to fake wallet software or recovery-phrase entry pages. The malware and infrastructure were built to steal wallet seed phrases and other victim data, with artifacts showing Telegram bot exfiltration, deceptive domains, trojanized installers, and macOS persistence via LaunchAgents. Rapid7 said the fake Trezor malware used Electron, process replacement, hidden windows, and local logging, while a trojanized **Claude Code** installer secretly deployed a fake **Ledger Live** payload alongside the legitimate tool to reduce suspicion. Recovered logs also showed the operator relied heavily on AI coding assistants including **GitHub Copilot**, **Claude Code**, and **Kimi** to develop, obfuscate, and host components of the scam infrastructure.
Aug 18, 2026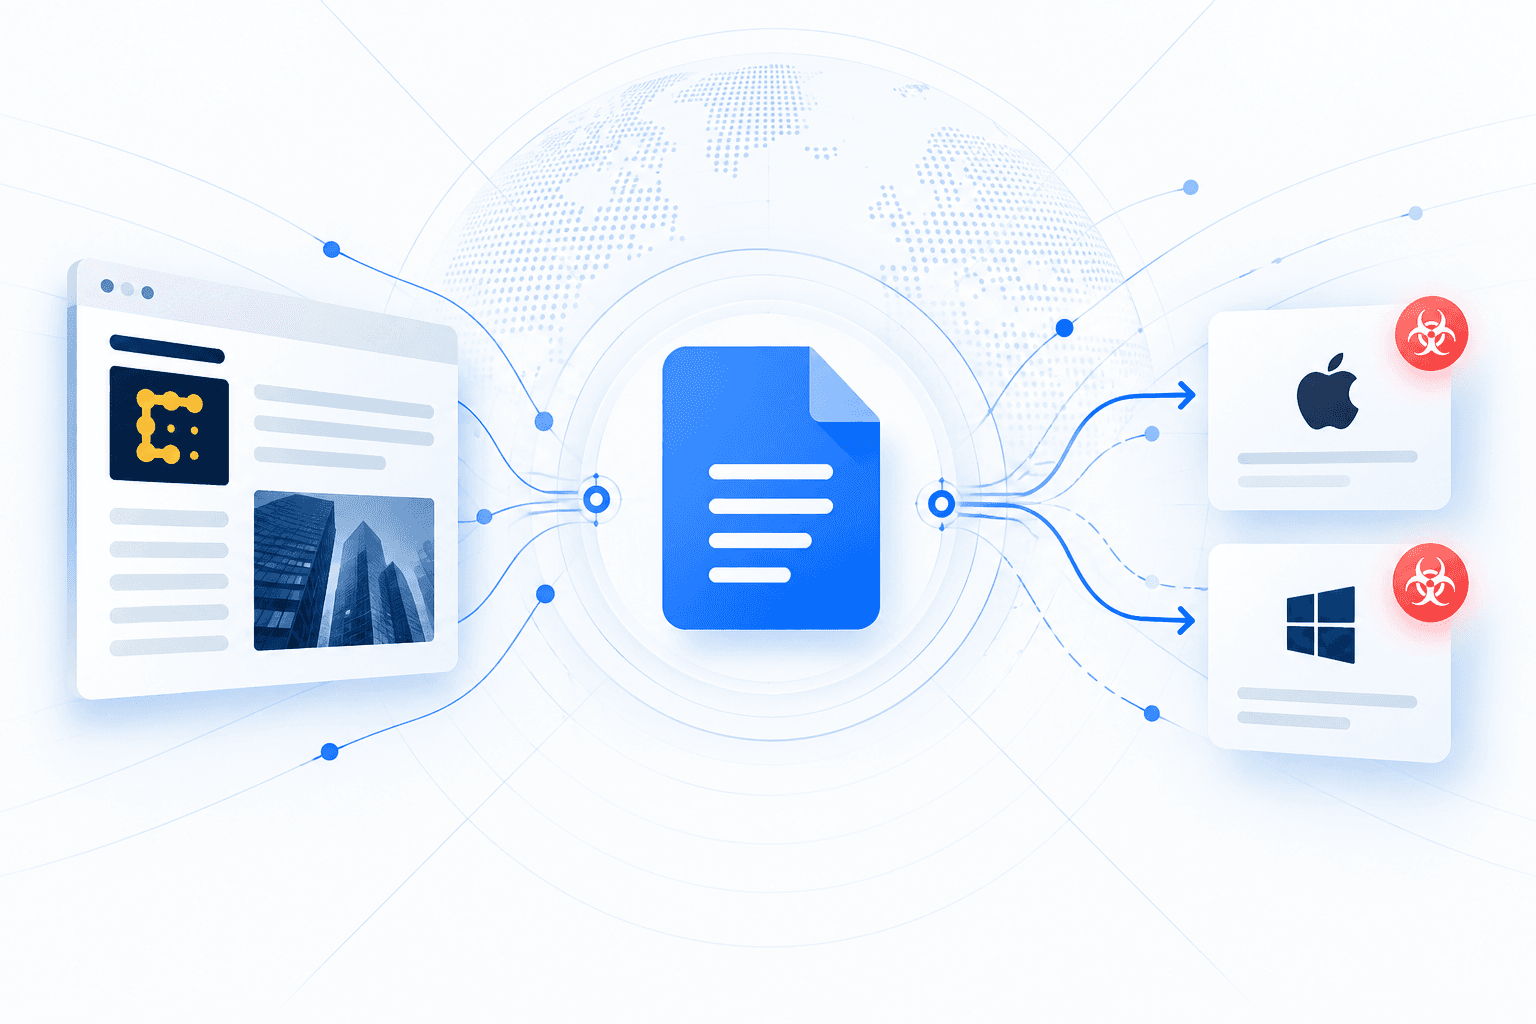
A threat actor impersonated a CoinDesk marketing executive in X direct messages, using post-Black Hat and DEFCON cryptocurrency-conference lures to target security researchers. The messages linked to legitimate Google Docs containing container-bound Google Apps Script that profiled visitors and sent their IP address, geolocation, browser details, and cryptocurrency-wallet-extension data to the operator through Telegram. The campaign routed victims to operating-system-specific malware: macOS users received a variant of the AMOS infostealer, while Windows users were served an encoded PowerShell loader chain and installers signed with three stolen or fraudulently issued certificates. Recovered Windows components included a malicious NetSupport Manager deployment, a persistent rogue local certificate authority capable of TLS interception, and a Ledger-wallet-focused implant. Russian-language comments and C2 artifacts indicate the operator may be Russian-speaking, but no threat group has been attributed.
Sep 14, 2026