Star Blizzard Expands Phishing With RedFlick and New Backdoor Delivery Chains
Threat Actor Intelligence · 14 sources · Updated 1mo ago · First seen Sep 29, 2026
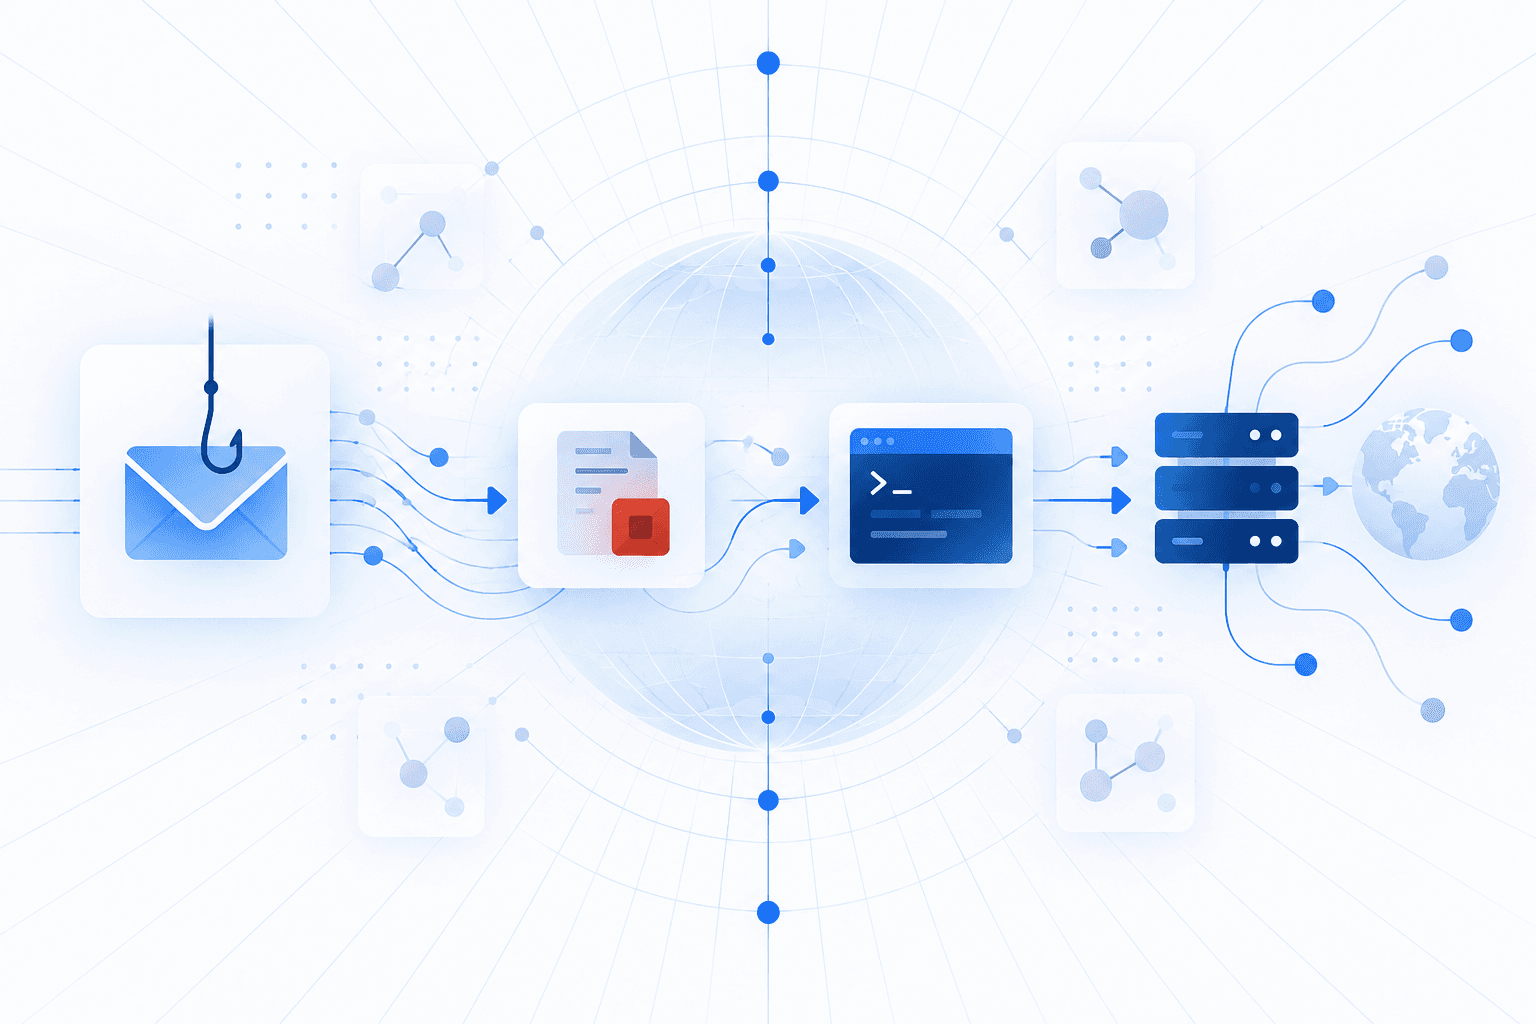
Russian state-linked Star Blizzard (also tracked as COLDRIVER) expanded its espionage phishing activity between January and August 2026, targeting more than 100 organizations, principally in the United States and United Kingdom. Targets included Ukrainian individuals and institutions, governments, NGOs, think tanks, financial organizations, academics, media, and diplomatic entities involved in Ukraine policy or support. The actor abused compromised cPanel- and WordPress-hosted sites to create sender accounts, then sent password-protected archives to recipients who engaged with initial lures.
Microsoft identified the actor’s RedFlick technique as a low-interaction delivery chain that uses VHDX/LNK files, MSI packages, Control Panel applets, PowerShell, and scheduled tasks to deploy the Python-based CosmicPulse backdoor. Persistence tasks impersonate network components, beacon host details, enable WebDAV remote execution, and retrieve a CosmicPulse downloader; July activity also hid Base64-encoded PowerShell payloads in PDFs. This development follows COLDRIVER’s 2025 rollout of the obfuscated PowerShell backdoor MAYBEROBOT (also called SIMPLEFIX), which replaced the Python-dependent YESROBOT and supported remote command execution and payload retrieval, indicating continued investment in adaptable malware delivery and evasion.