
Loading story…
Jamf Threat Labs identified CloudSyncD, a universal macOS backdoor distributed in a disk image masquerading as a Zoom installer. The lure persuades users to bypass Gatekeeper and enter their account password into a fraudulent authorization prompt; the installer stores the password in a disguised Zoom configuration file, obscuring it with Base64 encoding, random filler, and zero-width Unicode characters, then uses it locally to launch an elevated second-stage payload.
CloudSyncD supports both Apple silicon and Intel Macs, surveys compromised hosts, communicates with encrypted command-and-control infrastructure every 8–16 seconds, and can execute supplied Mach-O binaries or unpack gzipped tar archives. Researchers found live C2 infrastructure spanning multiple domains after first observing a development-stage build, suggesting progression toward operational deployment, but reported no confirmed infections, persistence mechanism, or attribution. Organizations should block the identified fake-installation delivery pattern, reinforce Gatekeeper and software-installation controls, and investigate suspicious Zoom-related disk images and unexpected password prompts.
Pull IOCs and campaign context straight into your stack.
3 events from the most recent confirmed update back to the earliest known activity.
Jamf Threat Labs published research detailing CloudSyncD's fake Zoom installer, Gatekeeper-bypass social engineering, local password capture, elevated second-stage execution, and encrypted C2-enabled backdoor capabilities. Jamf reported no confirmed infections, persistence mechanism, or attribution to a specific threat actor.
Two days after its initial discovery, Jamf identified CloudSyncD samples configured with live command-and-control infrastructure across multiple domains, indicating the operation was progressing toward deployment.
Jamf Threat Labs first encountered a development-stage build of the CloudSyncD macOS backdoor through VirusTotal monitoring. The malware was packaged in a disk image masquerading as a Zoom installer.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Microsoft said the North Korea-linked threat group **Sapphire Sleet**—also tracked as **APT38** and tied to the Lazarus ecosystem—targeted macOS users in cryptocurrency, finance, venture capital, and blockchain through social engineering rather than software exploits. The operation reportedly used fake recruiter personas on platforms including LinkedIn to lure victims into sham job interviews, then directed them to open a malicious AppleScript file masquerading as a Zoom update, **`Zoom SDK Update.scpt`**. That file launched a multi-stage infection chain using native macOS tools, downloaded additional payloads, and executed in a user-initiated context to help evade protections such as Gatekeeper, notarization, quarantine enforcement, and TCC controls. The intrusion deployed multiple backdoors, including **`systemupdate.app`**, which displayed a fake macOS password prompt to capture credentials, and **`icloudz`**, which loaded payloads directly into memory via **`NSCreateObjectFileImageFromMemory`**. Microsoft said the malware manipulated the TCC database, established persistence, and exfiltrated cryptocurrency wallets, browser data, Telegram sessions, SSH keys, Apple Notes, keychain material, and other sensitive information, with some stolen credentials sent through the Telegram Bot API. Apple was notified through responsible disclosure and subsequently added **Safari Safe Browsing** protections and **XProtect** signatures to detect and block the campaign’s infrastructure and malware.
Jun 29, 2026
A new **MacSync** malware-as-a-service campaign targets macOS cryptocurrency users and developers with trojanized DMG applications, binary loaders, and droppers. Originally advertised as Mac.c in 2025, the stealer has progressed from AppleScript payloads to Swift and Objective-C binaries and now uses Apple iCloud Calendar and file-hosting infrastructure to retrieve subsequent payloads. MacSync collects browser and cryptocurrency-wallet data, credentials, Keychain-related material, Telegram data, cloud and developer configuration files, system details, and shell histories. It persists through LaunchAgents, modified ZSH settings, global Git hooks, Login Items, and restoration scripts while suppressing user notifications; its backdoor can receive C2 tasks to install browser extensions, replace Ledger wallet software, repeat collection, and potentially intercept browser traffic.
Sep 30, 2026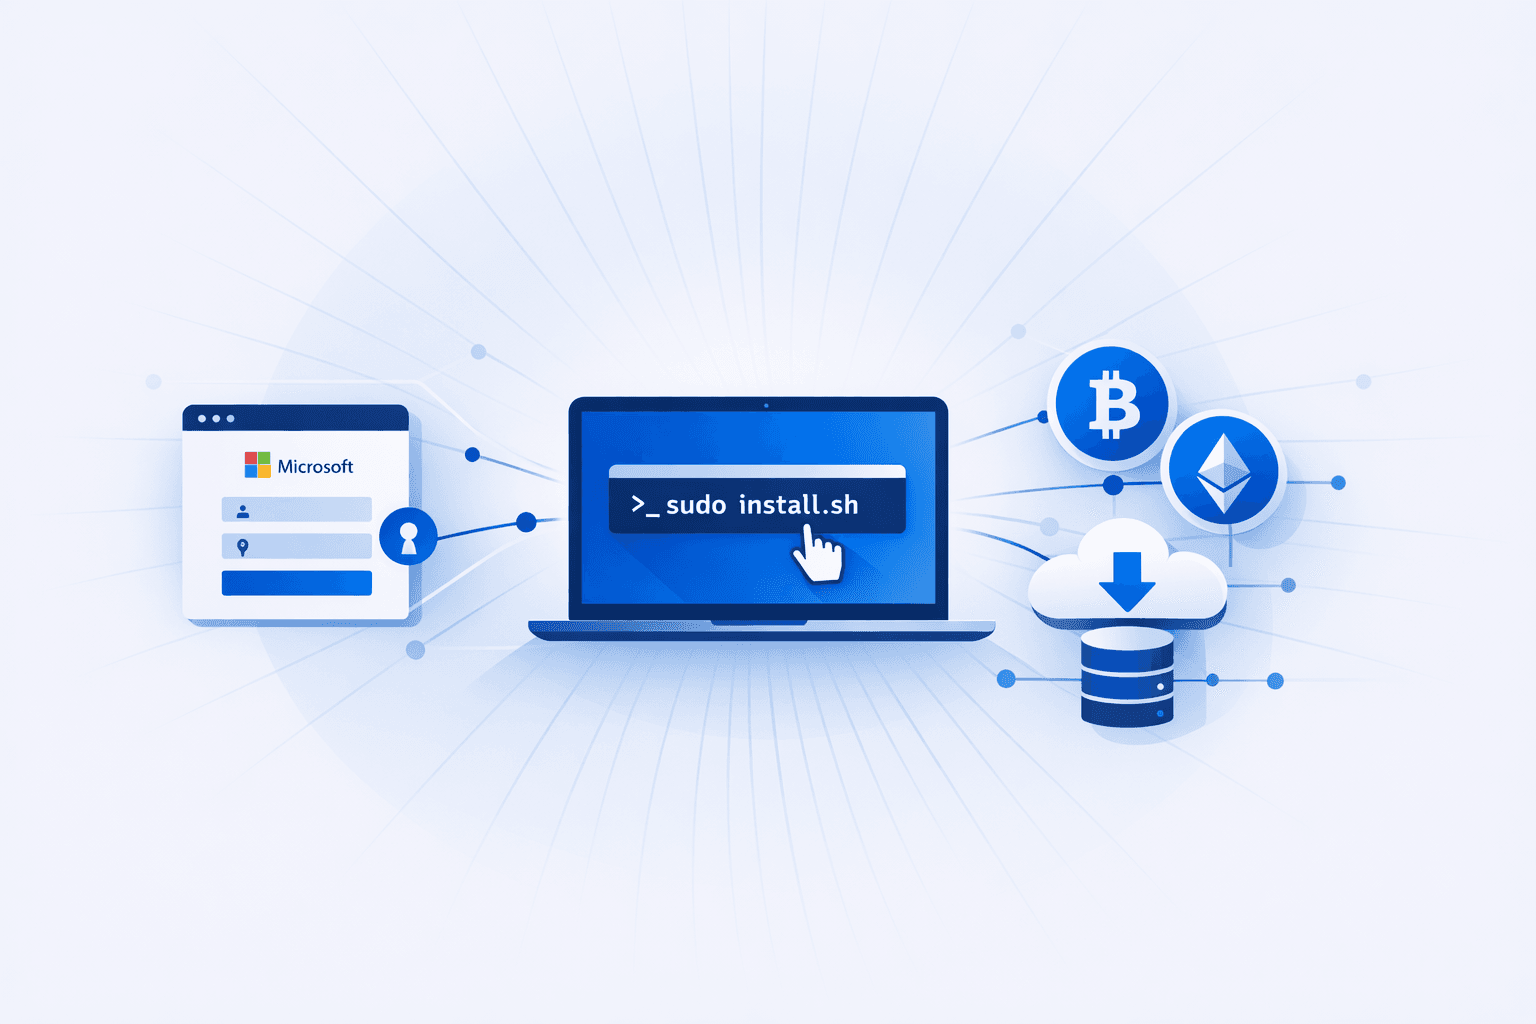
Security researchers reported a **macOS infostealer** dubbed **MacSync** being distributed as a low-cost **Malware-as-a-Service (MaaS)**, primarily targeting **cryptocurrency users** via a *ClickFix*-style social engineering lure. The campaign uses phishing infrastructure (including domains mimicking **Microsoft login** pages) to redirect victims to a fake macOS *cloud storage installer* site that instructs users to “install” by copying and pasting a **single Terminal command**. This approach relies on user execution rather than a signed app package, allowing the infection chain to **bypass macOS protections** such as **Gatekeeper** and **notarization**. Technical analysis describes a **script-based, multi-stage** infection chain: the pasted one-liner fetches a remote script that installs a **daemonized Zsh loader** which detaches from the Terminal session and runs in the background, then retrieves additional payloads (including **AppleScript**) to perform data theft. Beyond credential and wallet data harvesting, reporting indicates MacSync can **persist and expand impact** by **trojanizing Electron-based cryptocurrency applications** (e.g., *Ledger Live* and *Trezor Suite*) by overwriting components to present convincing phishing flows designed to capture **PINs** and **recovery phrases**, potentially triggering theft well after the initial compromise.
Jun 29, 2026