
Loading story…
Rapid7 identified two overlapping Linux malware campaigns targeting South Korean and Taiwanese telecom and network-edge email security environments. One uses BPFDoor variants and a BPF-enabled Rekoobe backdoor to impersonate South Korean SpamSniper anti-spam software and legitimate background processes. The other targets Taiwanese ShareTech appliances with a vendor-oriented dropper and AVERAT, a newly identified remote-access tool analyzed across six builds. Appliance-specific masquerading, passive packet triggers, and SMTP-disguised communications over TCP port 25 help the implants evade detection, particularly on secure email gateways with limited endpoint visibility and difficult-to-baseline outbound mail traffic.
The Taiwanese deployment chain launches AVERAT and a resident watchdog, then deletes their staged executables while the processes remain active. AVERAT supports remote shells, file operations, module loading, proxying, and configurable command-and-control through compromised Taiwanese consumer and small-business appliances. The relay infrastructure resembles operational relay box networks described in China-nexus advisories, but Rapid7 found no evidence establishing membership in a named network or definitive actor attribution. Recommended detection priorities include unexpected raw packet sockets and BPF filters, deleted executable mappings, appliance-specific staging artifacts, and outbound port-25 connections originating from non-mail processes.
Pull IOCs and campaign context straight into your stack.
3 events from the most recent confirmed update back to the earliest known activity.
Rapid7 traced three AVERAT relay addresses to a fuel retailer's Synology NAS, an obsolete SMB appliance, and a Dahua recorder on Chunghwa Telecom's network; all exposed PPTP with an identical fingerprint. Researchers assessed the devices as SMTP-disguised relays and VPN footholds but found no indicator overlap establishing membership in a named relay network or definitive actor attribution.
Rapid7 examined six AVERAT builds targeting Taiwanese appliances and reconstructed a ShareTech-oriented installer that launches the backdoor and a watchdog before deleting their staged executables while the processes remain active. AVERAT disguises encrypted command-and-control as SMTP traffic and supports remote shells, file operations, module loading, and proxying.
Rapid7 analyzed Linux implants that impersonate SpamSniper software and legitimate background processes on South Korean telecom and email-security systems. The analysis revealed passive BPF packet triggers, shell-access functionality, and a Rekoobe reverse shell disguised as a SpamSniper service using TCP port 25.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 18 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Rapid7 reported that the China-linked espionage group **Red Menshen** has expanded a long-running campaign against global telecommunications providers by deploying upgraded **BPFDoor** implants designed for covert, persistent access inside Linux-based core infrastructure. Victims span the Middle East, Africa, Asia-Pacific, and Europe, with reporting tying activity to telecom environments in South Korea, Hong Kong, Myanmar, Malaysia, Egypt, and other regional networks. The malware abuses Berkeley Packet Filter functionality to inspect traffic from within the kernel and stays dormant until it receives specially crafted trigger packets, allowing it to avoid exposed listening ports and conventional command-and-control patterns. Researchers said the campaign supports strategic surveillance and pre-positioning, potentially exposing telecom signaling and authentication data tied to subscriber identity, mobility, and government communications. Newly documented BPFDoor variants hide activation inside seemingly legitimate **HTTPS** traffic, use fixed trigger offsets and magic markers, add **ICMP-based** relay and shell capabilities, and in some cases beacon outbound over port `443` while masquerading as normal NTP- or management-related traffic. Rapid7 also described variants that monitor telecom-relevant protocols such as **SCTP**, wipe file descriptors, timestomp artifacts, run from paths such as `/var/run/user/0`, and disguise themselves as **HPE ProLiant** or Kubernetes-related processes. Alongside BPFDoor, operators used tools including **CrossC2**, **TinyShell**, **Sliver**, brute-force utilities, and credential theft tooling to move from exposed edge devices into telecom cores. Rapid7 released a detection script for known BPFDoor samples and urged defenders to hunt for structural indicators such as **AF_PACKET** socket creation, attached BPF filters, spoofed root processes, and anomalous ICMP markers rather than relying on payload inspection alone.
Jun 29, 2026
Security researchers detailed **BPFDoor**, a stealthy Linux backdoor attributed by PwC to the China-linked group **Red Menshen**, describing its use in long-running intrusions against telecommunications, government, logistics, and education organizations in the Middle East and Asia. The malware is designed for covert re-entry and persistence, using raw sockets and **Berkeley Packet Filter (BPF)** logic to inspect network traffic for specially crafted magic packets, then launching a reverse shell, bind shell, or pingback without exposing obvious new listening services. Researchers said BPFDoor can hide behind legitimate network activity by listening on traffic destined for existing services such as `443`, allowing operators to execute commands while avoiding conspicuous firewall or port changes. Analysis showed the malware often copies itself into `/dev/shm`, deletes the original binary, spoofs process names, creates PID files under `/var/run`, and can temporarily alter `iptables` to hijack traffic for command and control; historical samples appeared functionally stable over time, with changes largely limited to hardcoded passwords, filenames, and process names. Elastic and other researchers published hunting guidance, YARA signatures, and tooling to help defenders identify infections.
Aug 15, 2026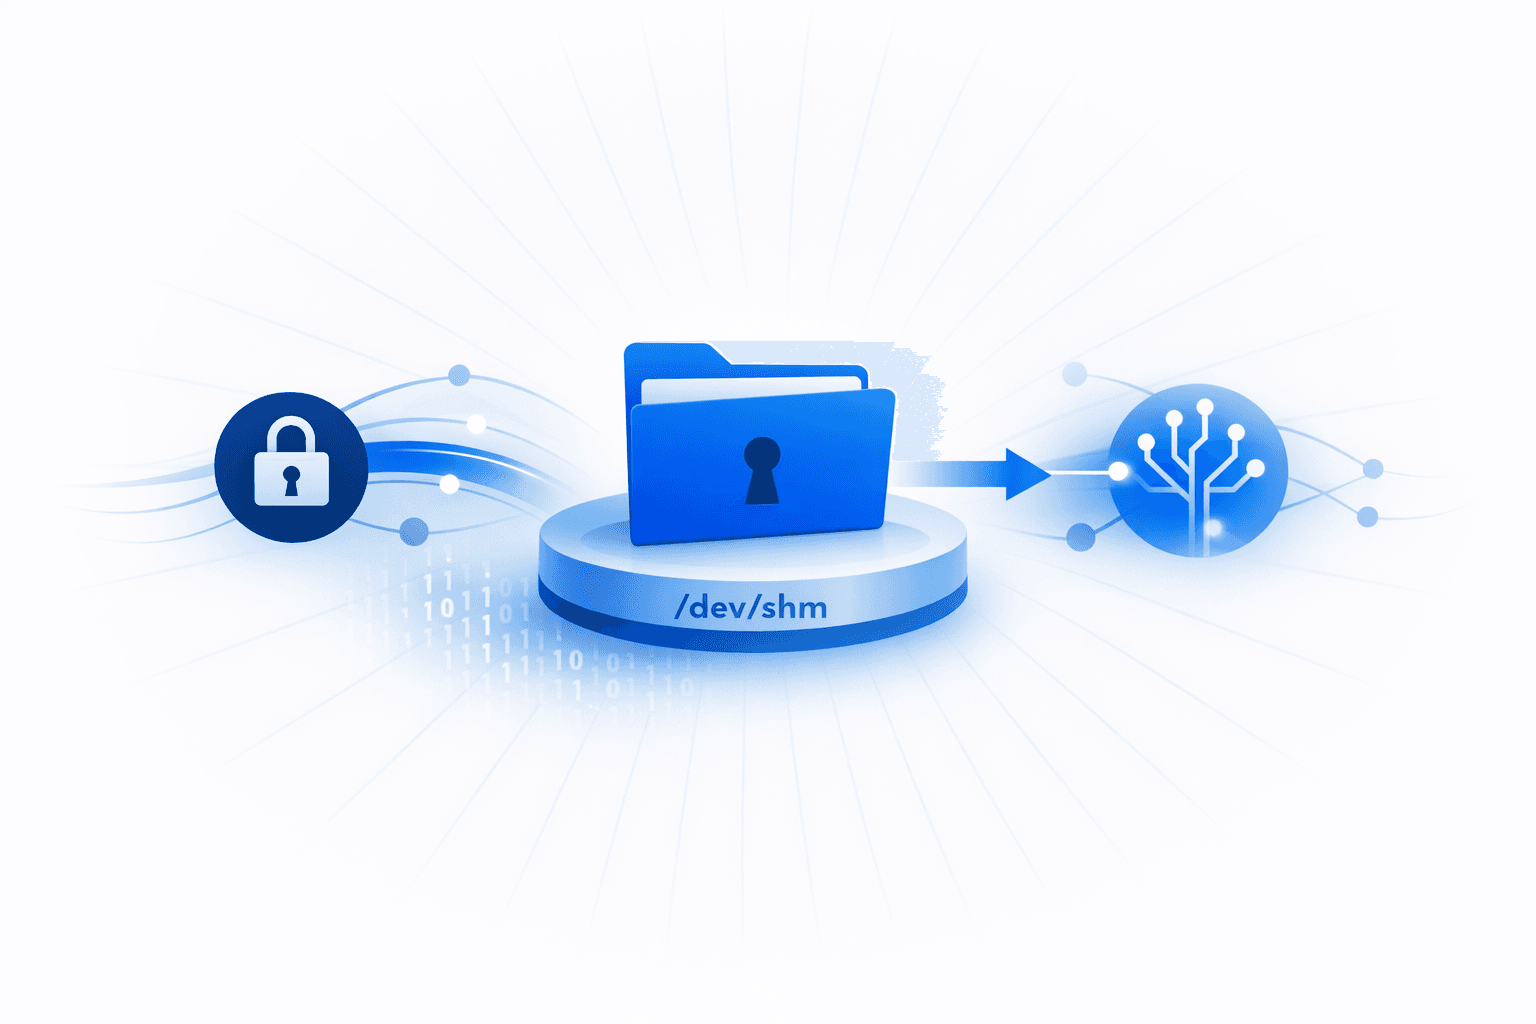
Analysis of the Linux backdoor **BPFDoor** shows the malware copying itself to `/dev/shm/kdmtmpflush`, changing the file’s permissions, and then re-launching the new instance through `execve` with the `--init` flag to complete setup. During execution it checks for `/var/run/haldrund.pid` to avoid multiple starts, deletes any prior copy of the payload, and timestomps the replacement file to `2008-10-30 19:17:16 UTC` to reduce suspicion. Runtime tracing also showed the malware adopting deceptive process names including `dbus-daemon --system` and `/usr/libexec/postfix/master` to blend into normal Linux activity. The traced sample then created a raw packet socket and attached a BPF filter with `SO_ATTACH_FILTER`, enabling BPFDoor to watch for specially crafted network traffic used to activate the implant. The backdoor was reported to respond to magic packets containing hardcoded passwords such as `justforfun` or `socket`, after which it could send a ping, spawn a reverse shell, or open a bind shell. The behavior highlights a stealth-focused Linux implant that combines fileless-style staging in shared memory, process masquerading, and packet-triggered remote access.
Aug 1, 2026