ESET Reports Belarus-Linked Wiper Attack in Ukraine and Closer Alignment With Russia
Active Exploitation · 10 sources · Updated 15d ago · First seen Oct 28, 2026
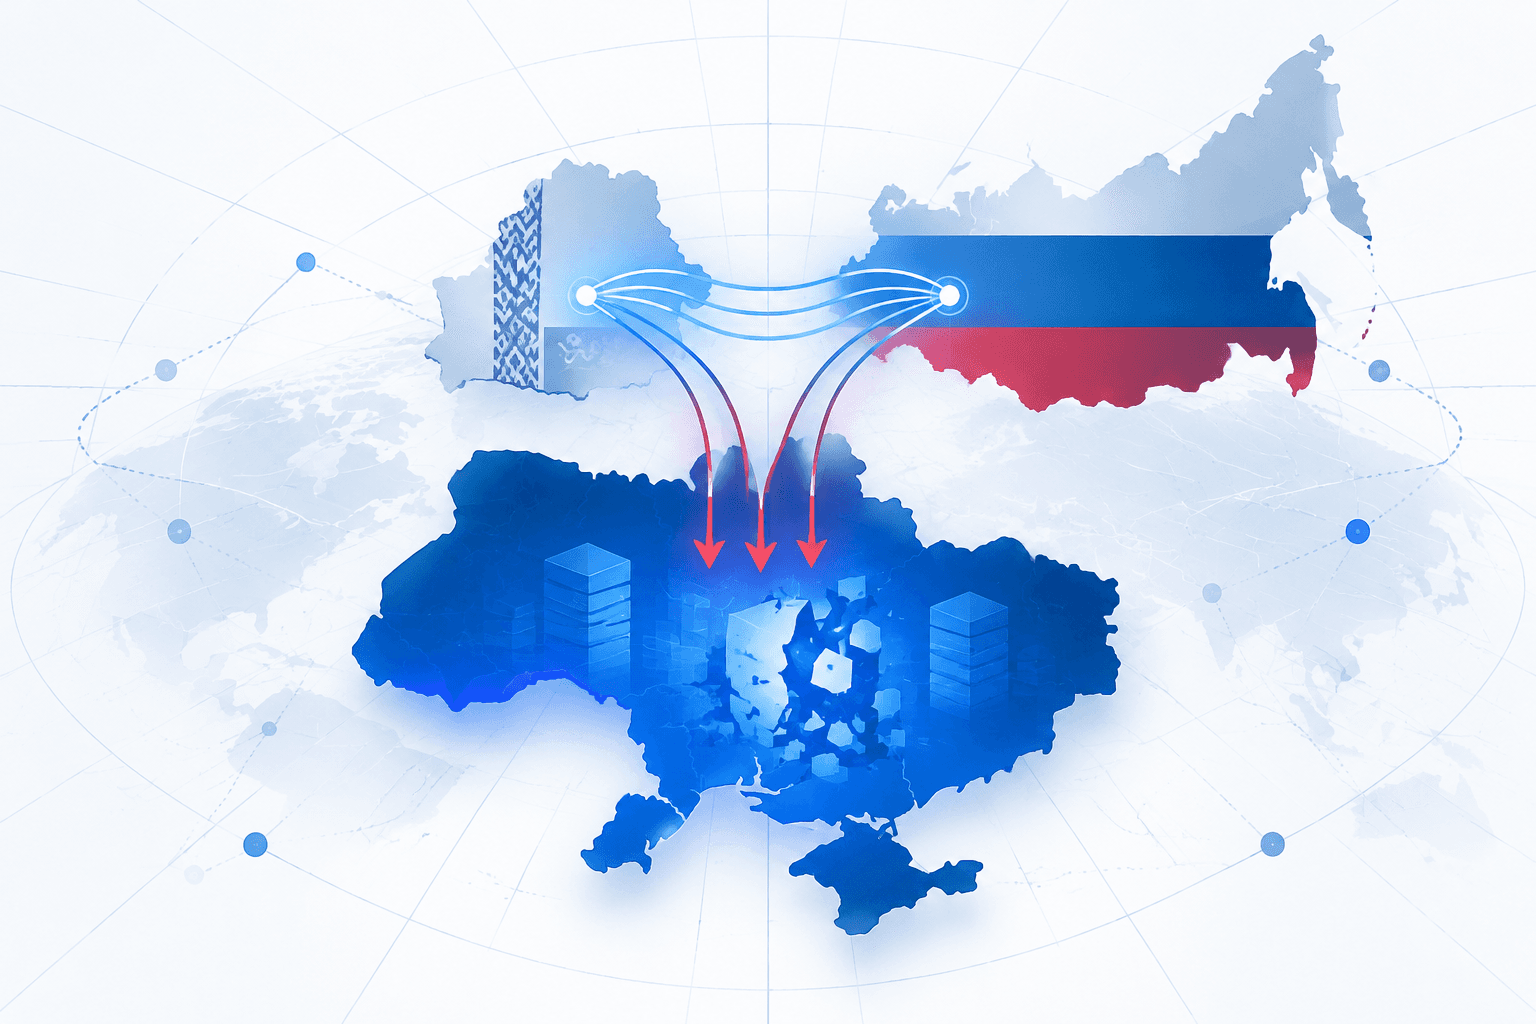
ESET reported increasingly close alignment between Belarus-linked cyber operations and Russian intelligence priorities in its review of advanced persistent threat activity from April through September 2026. In late May, GhostWriter deployed data-wiping malware against a Ukrainian manufacturer believed to be important to the transportation sector—the first destructive attack by a Belarus-aligned group that ESET had documented in Europe. Researchers could not determine whether the wiping was intended to cause damage or conceal espionage. ESET warned that Belarusian groups could increasingly serve as Russian proxies, potentially sharing tools and infrastructure or collaborating on attacks.
The report also documented broader espionage, software supply-chain compromises, and destructive operations. China-aligned actors targeted government entities and Taiwan’s semiconductor industry; Iran-aligned groups resumed operations primarily against Israeli entities; and North Korea-aligned actors continued targeting technology companies, cryptocurrency businesses, and developers while expanding their attention to Ukraine, including drone-related interests. Evidence that North Korean activity directly supported Russia’s war remained less definitive. Other findings included exploitation of MDaemon mail servers in Ukraine and attempted deployment of PrincessSpy Android spyware. ESET observed AI use for malware development, decoy creation, and attempts to obstruct automated security analysis, but found no substantial shift toward fully autonomous operations.