Evooo1Bot Uses Five-Minute Cron Jobs to Restore Malware on Network Appliances
Attack Tradecraft · 3 sources · Updated 20h ago · First seen Nov 18, 2026
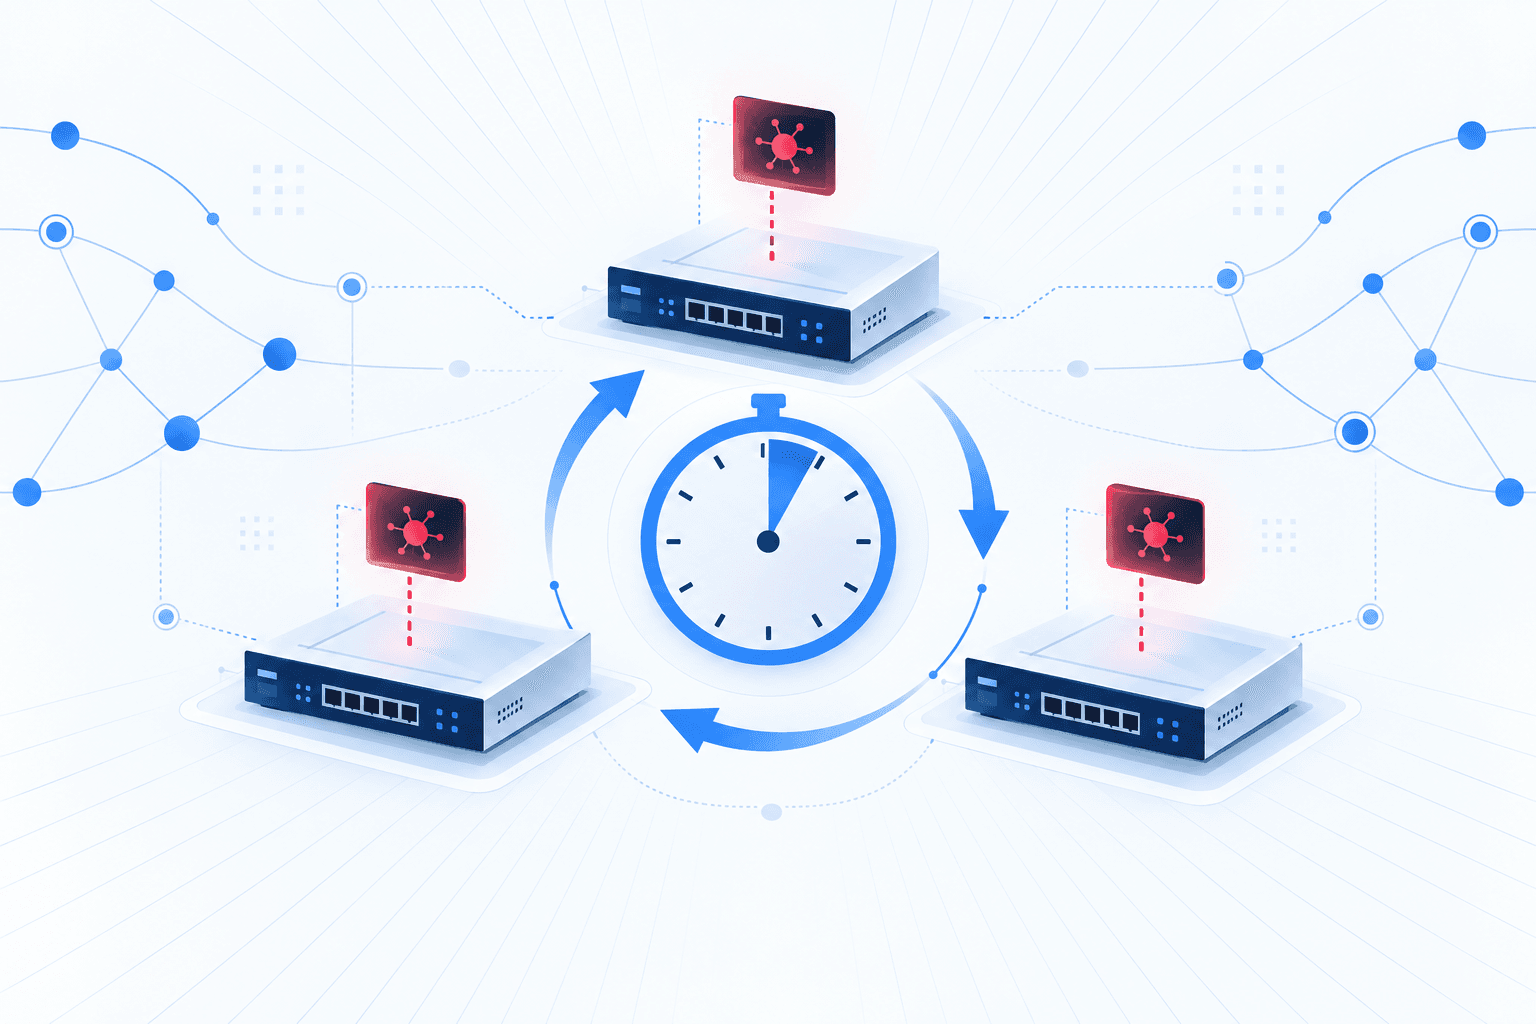
Evooo1Bot uses malicious cron jobs to restore malware on compromised Linux-based firewalls, routers, and other network appliances, undermining cleanup that only kills processes or deletes binaries. The botnet targets internet-facing devices through known vulnerabilities and SSH password guessing. Its persistence command installs a scheduled task that downloads and executes a loader every five minutes, alongside systemd, init, and login startup mechanisms. Evooo1Bot combines Mirai-derived attack code with encrypted command-and-control traffic and SOCKS proxy functionality that can conceal attacker activity and support movement deeper into networks.
Eclypsium warned that appliance management interfaces and limited endpoint visibility can leave underlying Linux persistence mechanisms uninspected. Its research also described SSHStalker’s one-minute relaunch mechanism, illustrating why patching an entry point does not eliminate established persistence. Responders should preserve evidence and remove malicious scheduler entries before terminating malware, then inspect system and user cron files, vendor-native schedulers, startup services, and login scripts. Cleanup should distinguish legitimate vendor tasks from malicious execution, address the initial entry points, and verify that no additional persistence remains before devices return to service.