Turla Uses Cereal Malware to Spy on Government Exchange Servers in Kazakhstan and Romania
Sector Threat Intelligence · 31 sources · Updated 51m ago · First seen Jan 15, 2026
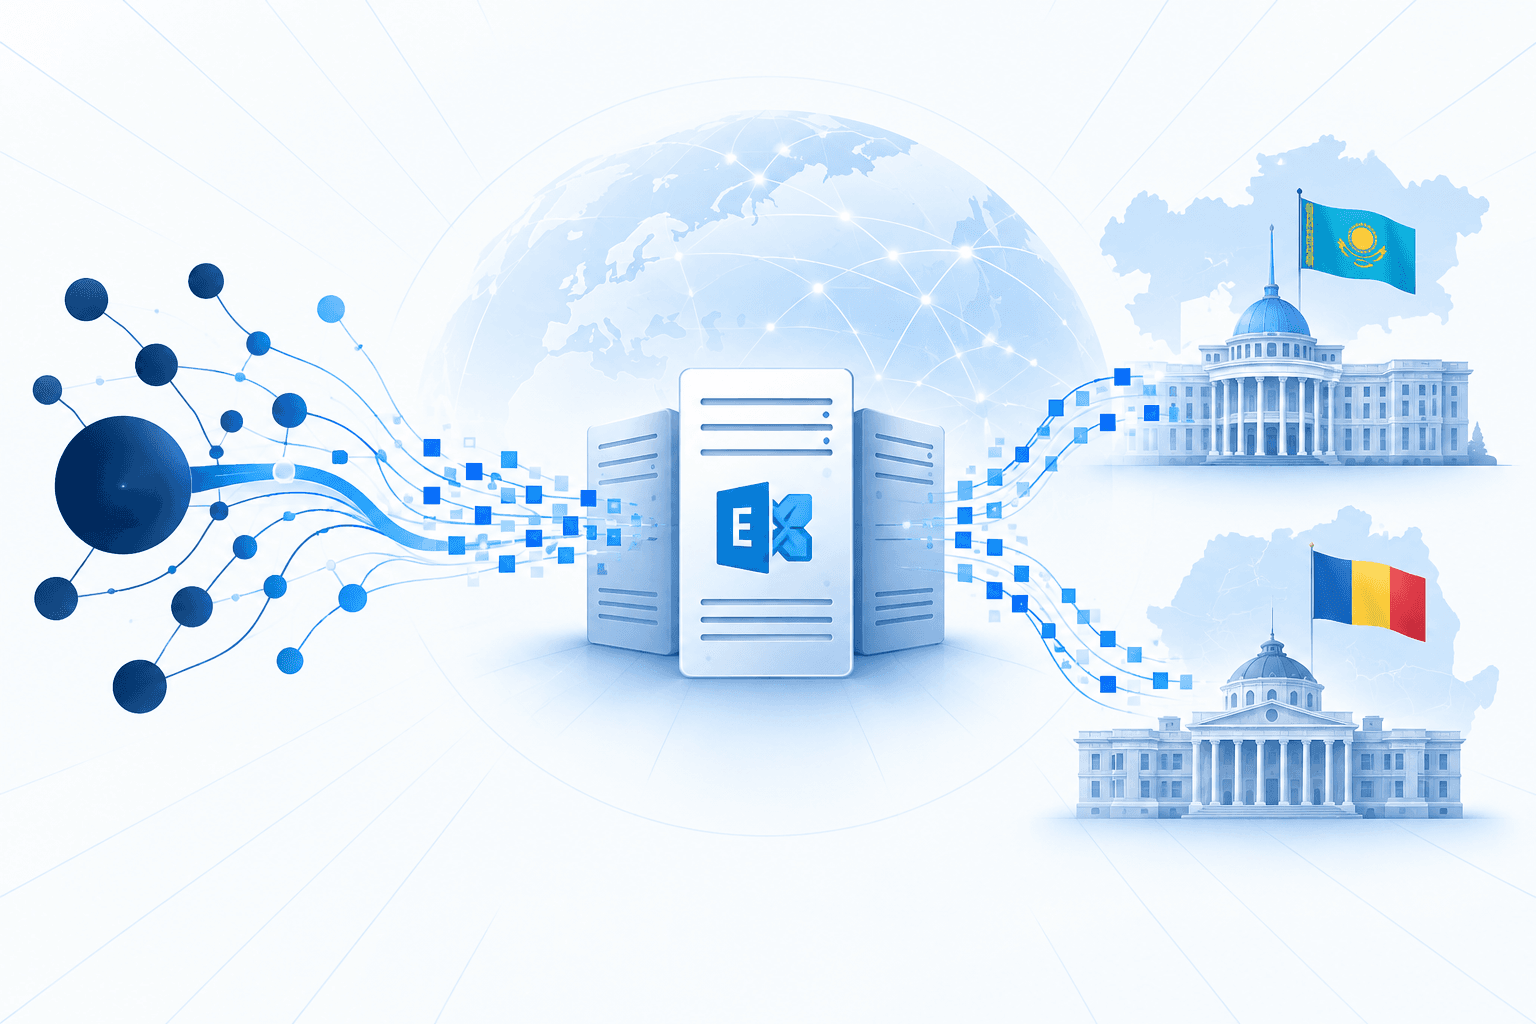
Russia-aligned cyberespionage group Turla deployed the previously undocumented Cereal toolset on Microsoft Exchange servers at government organizations in Kazakhstan and Romania, according to ESET. Researchers discovered the malware at the Kazakh organization on November 28, 2025, and identified a Romanian organization compromised on December 23, 2025. The Romanian deployment selectively collected correspondence involving NATO and European Union institutional addresses. ESET attributed Cereal to Turla with high confidence based on an accompanying Turla-linked component and similarities to older malware; the initial access vector remains unknown.
Cereal's eight-component, modular .NET architecture turns compromised Exchange servers into espionage and command-processing hubs, with no external command-and-control infrastructure observed. Its CerealNeuron backdoor receives encrypted commands through web requests resembling legitimate Exchange traffic, while CerealBox hijacks existing transport-agent handlers to inspect email without registering a new agent or disrupting delivery. Other components execute encrypted tasks in memory to retrieve messages, query Active Directory, extract credentials, and manipulate files. The design reduces forensic evidence and conventional outbound-beaconing indicators, making Exchange process behavior, transport-handler integrity, and suspicious inbound web requests important investigation priorities.